Bemærk
Adgang til denne side kræver godkendelse. Du kan prøve at logge på eller ændre mapper.
Adgang til denne side kræver godkendelse. Du kan prøve at ændre mapper.
Note
Some capabilities of App Control for Business are only available on specific Windows versions. Learn more about App Control feature availability.
Create the policy using the App Control Wizard
You can use the App Control for Business Wizard to create an AppId Tagging policy. The App Control Wizard is available for download at the App Control Wizard Installer site.
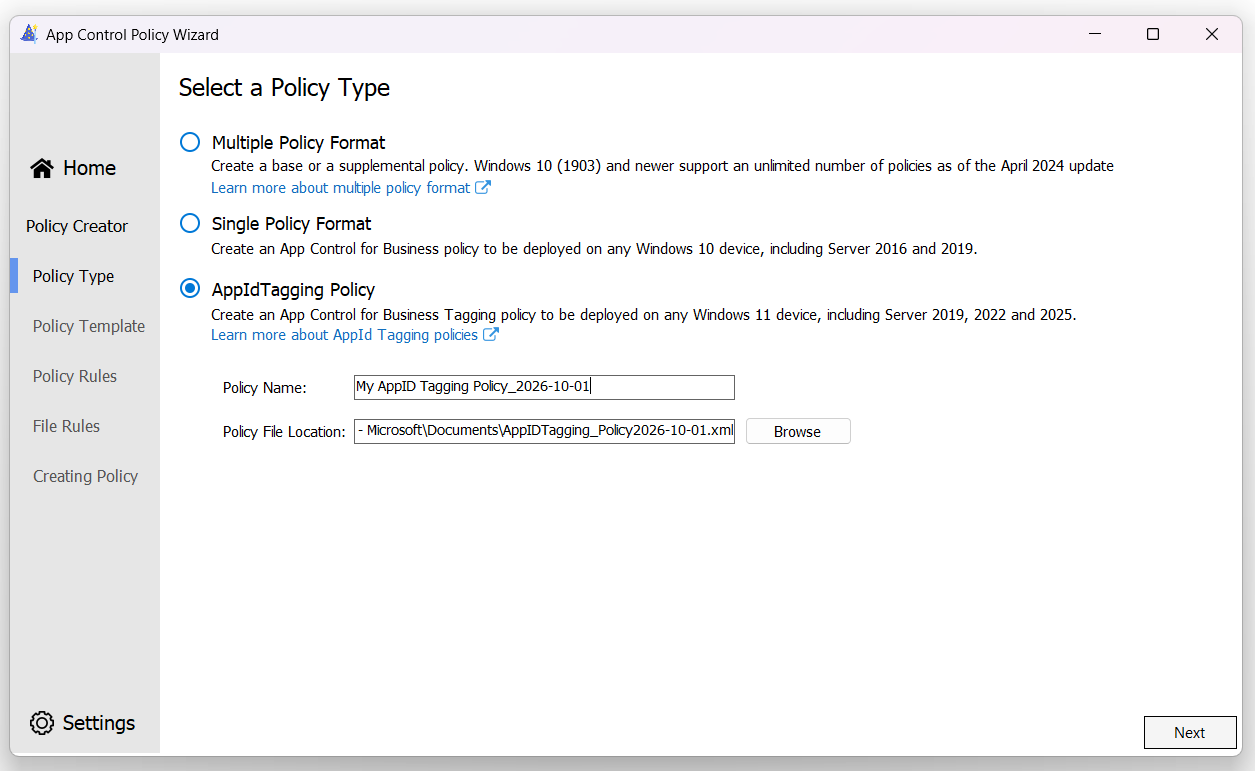
Start the Policy Creator workflow. On the Select a Policy Type page, select AppIdTagging Policy, enter a policy name and file location, and then select Next.
As of version 2.6, the App Control Wizard supports creating AppId Tagging policies directly. You don't need to select Multiple Policy Format or convert the completed policy to an AppId Tagging policy.
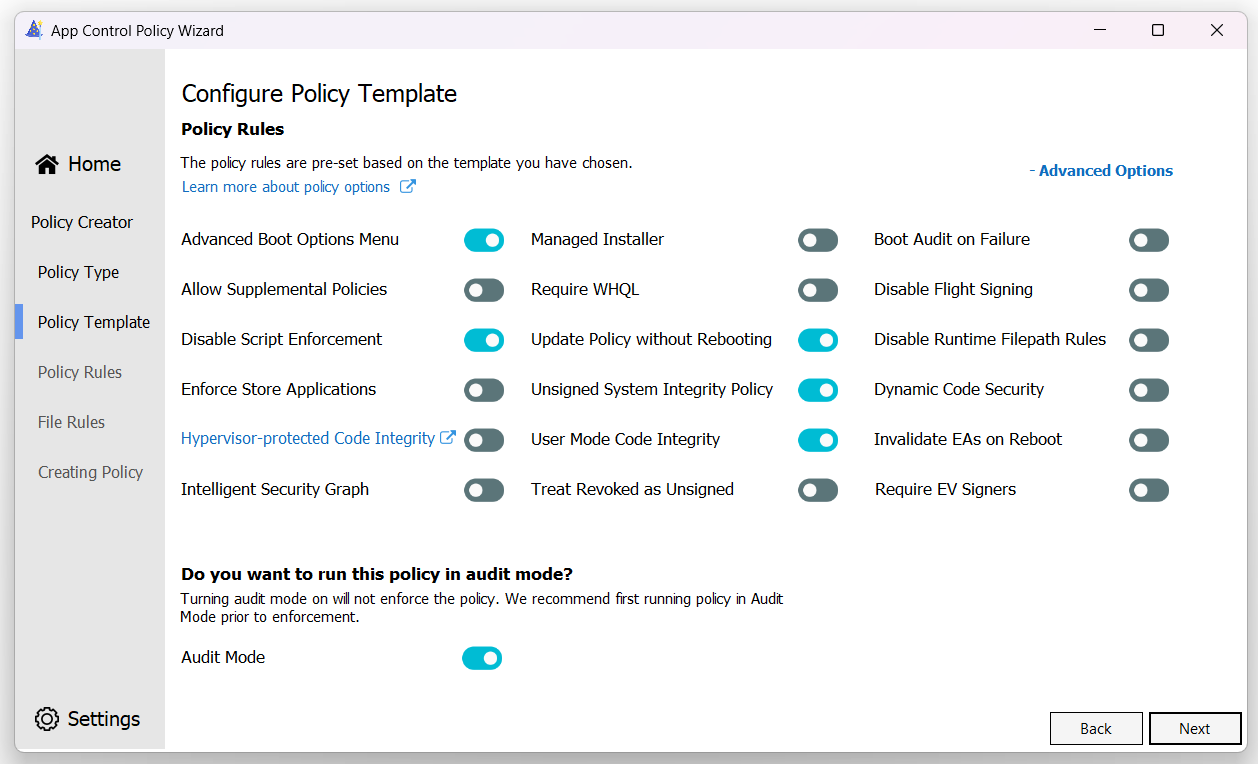
Set the following policy rule options, and then select Next.
Create custom rules. These are the criteria for which processes App Control will tag.
Selecting the
+ Custom Rulesbutton opens the Custom Rules panel. The Wizard supports five types of file rules:- Publisher rules: Create a rule based off the signing certificate hierarchy. Additionally, the original filename and version can be combined with the signing certificate for added security.
- Path rules: Create a rule based off the path to a file or a parent folder path. Path rules support wildcards.
- File attribute rules: Create a rule based off a file's immutable properties like the original filename, file description, product name or internal name.
- Package app name rules: Create a rule based off the package family name of an appx/msix.
- Hash rules: Create a rule based off the PE Authenticode hash of a file.
For more information on creating new policy file rules, see the guidelines provided in the creating policy file rules section.
Note
Keep the Allow *DLL rule in the policy. AppId tags apply only to executable files, so keeping this rule avoids unnecessary DLL evaluation and can dramatically improve performance. The security impact is benign because DLL files aren't in scope for AppId tagging. For more information, see AppId Tagging policy evaluates DLL files that aren't in scope for tagging.
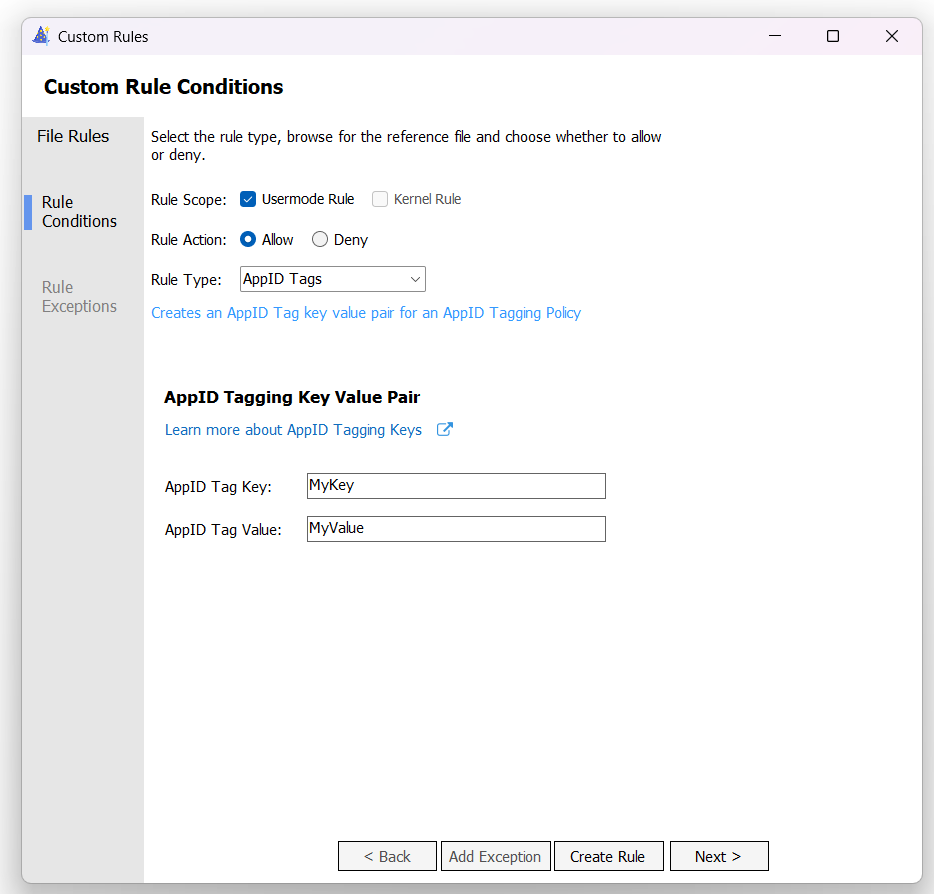
Add the AppId Tagging key-value pair. Select AppID Tags for Rule Type, enter the desired values in the AppID Tag Key and AppID Tag Value fields, and then select Create Rule. These key-value pair fields will be applied to the process tag by App Control.
Complete the remaining Wizard pages to create the policy.
Create the policy using PowerShell
Using this method, you create an AppId Tagging policy directly using the App Control PowerShell commands. These PowerShell commands are only available on the supported platforms listed in AppId Tagging Guide. In an elevate PowerShell instance:
Create an AppId rule for the policy based on a combination of the signing certificate chain and version of the application. In the example below, the level has been set to SignedVersion. Any of the App Control File Rule Levels can be used in AppId rules:
$rule = New-CiPolicyRule -Level SignedVersion -DriverFilePath <path_to_application>Create the AppId Tagging Policy. Replace the AppIdTagging Key-Value pair for your scenario:
New-CIPolicy -rules $rule -FilePath .\AppIdPolicy.xml -AppIdTaggingPolicy -AppIdTaggingKey "MyKey" -AppIdTaggingValue "MyValue"Set the rule-options for the policy:
Set-RuleOption -Option 0 .\AppIdPolicy.xml  # Usermode Code Integrity (UMCI)
Set-RuleOption -Option 16 .\AppIdPolicy.xml # Refresh Policy no Reboot
Set-RuleOption -Option 18 .\AppIdPolicy.xml # (Optional) Disable FilePath Rule Protection
If you're using filepath rules, you may want to set option 18. Otherwise, there's no need.
Set the name and ID on the policy, which is helpful for future debugging:
Set-CIPolicyIdInfo -ResetPolicyId -PolicyName "MyPolicyName" -PolicyId "MyPolicyId" -AppIdTaggingPolicy -FilePath ".\AppIdPolicy.xml"The policyID GUID is returned by the PowerShell command if successful.
Deploy for Local Testing
After creating your AppId Tagging policy in the above steps, you can deploy the policy to your local machine for testing before broadly deploying the policy to your endpoints:
Depending on your deployment method, convert the xml to binary:
Convertfrom-CIPolicy .\policy.xml ".\{PolicyIDGUID}.cip"Optionally, deploy it for local testing:
copy ".\{Policy ID}.cip" c:\windows\system32\codeintegrity\CiPolicies\Active\
./RefreshPolicy.exe
RefreshPolicy.exe is available for download from the Microsoft Download Center.
Next Steps
For more information on debugging and broad deployment of the AppId Tagging policy, see Debugging AppId policies and Deploying AppId policies.