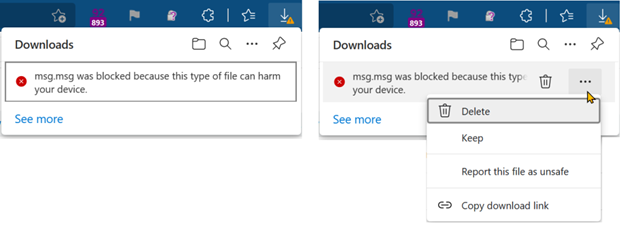
Since Windows Security is detecting and quarantining it at startup every time, the likely issue is a recurring malware component or startup mechanism that is reinstalling or relaunching the threat.
Recommended cleanup path:
- Run a Microsoft Defender Offline scan.
- Go to Start > Settings > Update & Security > Windows Security > Virus & threat protection.
- Under Current threats, select Scan options.
- Select Windows Defender Offline scan and then Scan now.
- Important: save work first, because the PC will restart before the scan starts.
- After Windows restarts, review what Defender found.
- Go to Start > Settings > Update & Security > Windows Security > Virus & threat protection.
- Under Current threats, select Threat history.
- Under Quarantined threats, select See full history.
- For detected items, use Remove to delete them. Leave them quarantined if not certain they are safe. A quarantined file does not pose a risk while it remains in quarantine.
- Run the Malicious Software Removal Tool if Defender reports the threat was only partially removed.
- Press Windows logo key + R.
- Run:
%windir%\system32\mrt.exe
- Allow it to make changes if prompted, then follow the prompts to scan and clean the PC.
- Restart the PC and install the latest Windows updates.
- Security updates are delivered through Windows Update and help close malware-related gaps.
- If another antivirus or antispyware product is installed, uninstall it unless it is intentionally being used.
- Go to Start > Settings > Apps.
- Select the unwanted security app and choose Uninstall.
- Caution: removing security software leaves the PC temporarily unprotected unless Microsoft Defender Antivirus is enabled and Windows Firewall is on.
- If the same detection still returns after reboot, avoid revisiting any site or file source that may be reintroducing it.
- Repeated detection can happen if the malware is being downloaded again or if a hidden component is restoring it.
About PowerShell removal: removing PowerShell does not by itself remove malware persistence. If the threat is triggered at startup, the cause is more likely a remaining malicious component than PowerShell itself.
If Windows Security shows Threat found - action needed, choose Quarantine unless the file is fully trusted. Allow on device should only be used for software that is known to be safe.
References:
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ECR%3C/text%3E%3C/svg%3E)