Note
Access to this page requires authorization. You can try signing in or changing directories.
Access to this page requires authorization. You can try changing directories.
After you create and configure a health model, monitor the health model resource itself in the Azure portal. Resource-level monitoring is separate from entity-level monitoring inside the model.
Use the following monitoring options:
- Metrics to track model-level telemetry, such as the number of entities and relationships in the model or discovery execution performance.
- Alerts to create alert rules on health model platform metrics and events.
View health model metrics
Use model-level metrics to monitor model growth, discovery activity, and platform behavior.
Open your health model resource in the Azure portal.
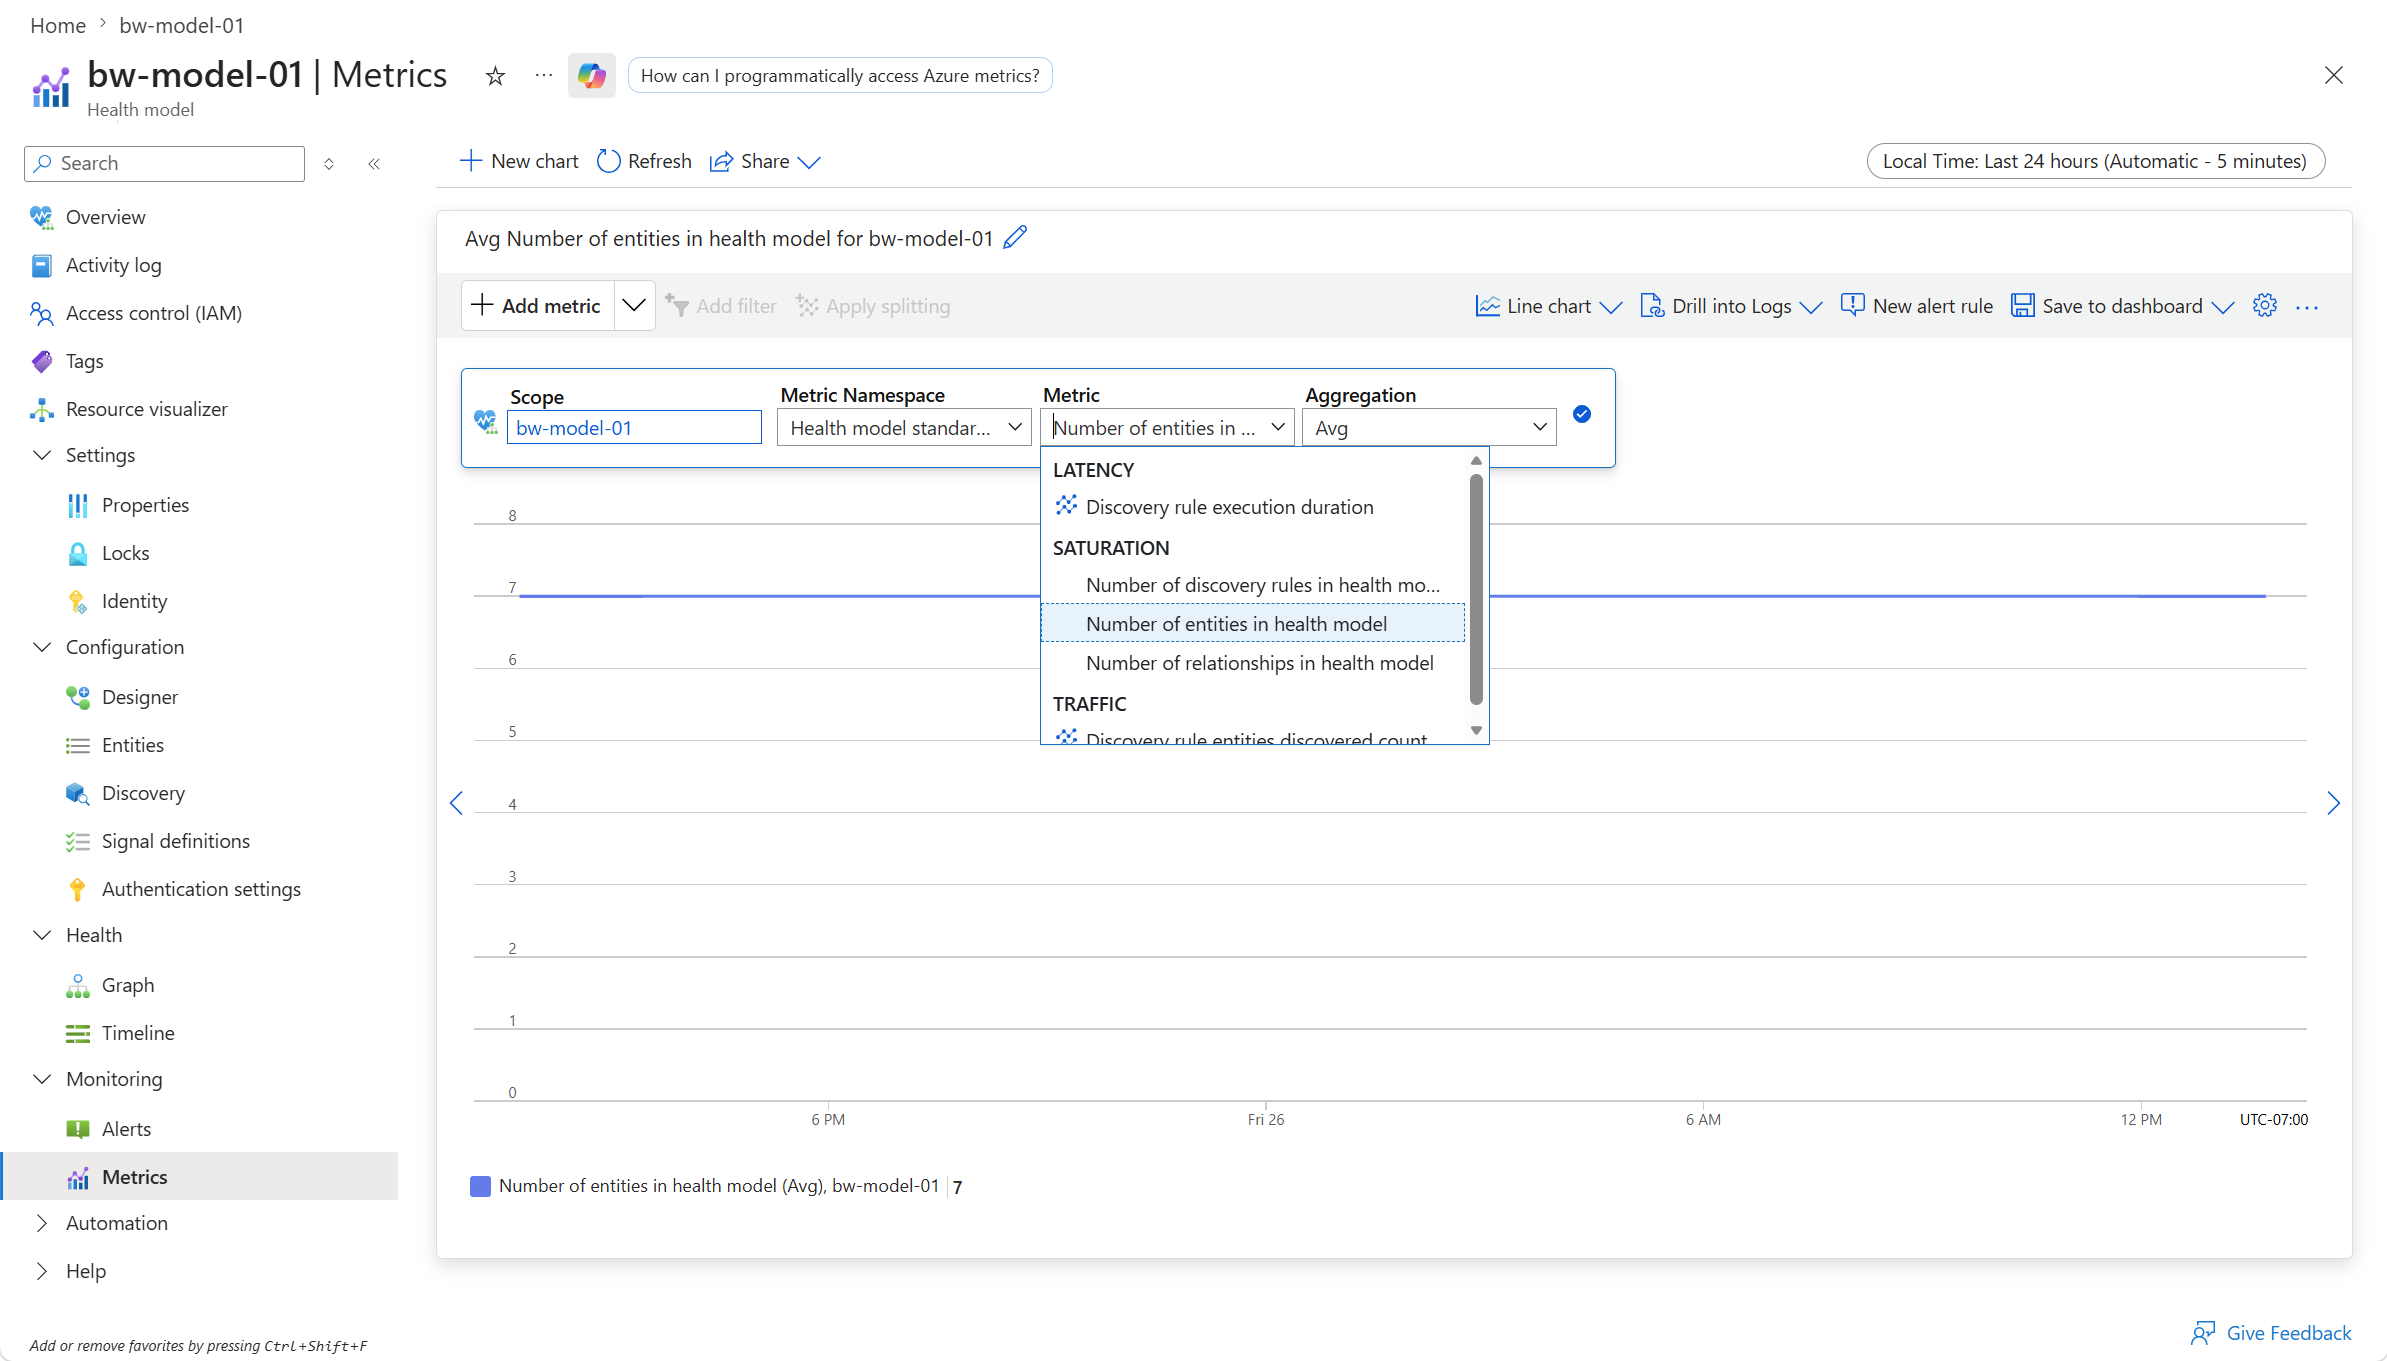
Under Monitoring, select Metrics.
In Metric namespace, select Health model standard metrics.
Select a metric and aggregation to visualize a trend over time.
Common metrics include:
- Number of entities in health model to track model size.
- Number of relationships in health model to track topology complexity.
- Discovery rule execution duration to track discovery performance.
- Discovery rule entities discovered count to track discovery results.
Create alerts for the health model resource
Model-level alerts are alert rules on the health model resource itself. They're not the same as alerts configured inside the health model for monitored entities. For details on entity-level alerts, see Enable alerts in Azure Monitor health models.
Use model-level alerts for scenarios such as:
- Notifying when discovery behavior changes unexpectedly.
- Notifying when discovery events indicate model updates, such as newly discovered entities.
- Notifying when model-level metric values cross expected thresholds.
To create a model-level alert:
Open your health model resource in the Azure portal.
Under Monitoring, select Alerts.
Select Create and then Alert rule.
Select a model-level signal, configure condition logic, and set thresholds.
Configure an action group and alert details, and then create the rule.