Compare Configuration Manager, Intune, and co-management
Microsoft Configuration Manager and Microsoft Intune serve different purposes and work best in different environments. Co-management lets you use both tools on the same Windows 10/11 devices so you can transition workloads gradually.
The following diagram compares the three approaches and shows which device workloads each one manages.
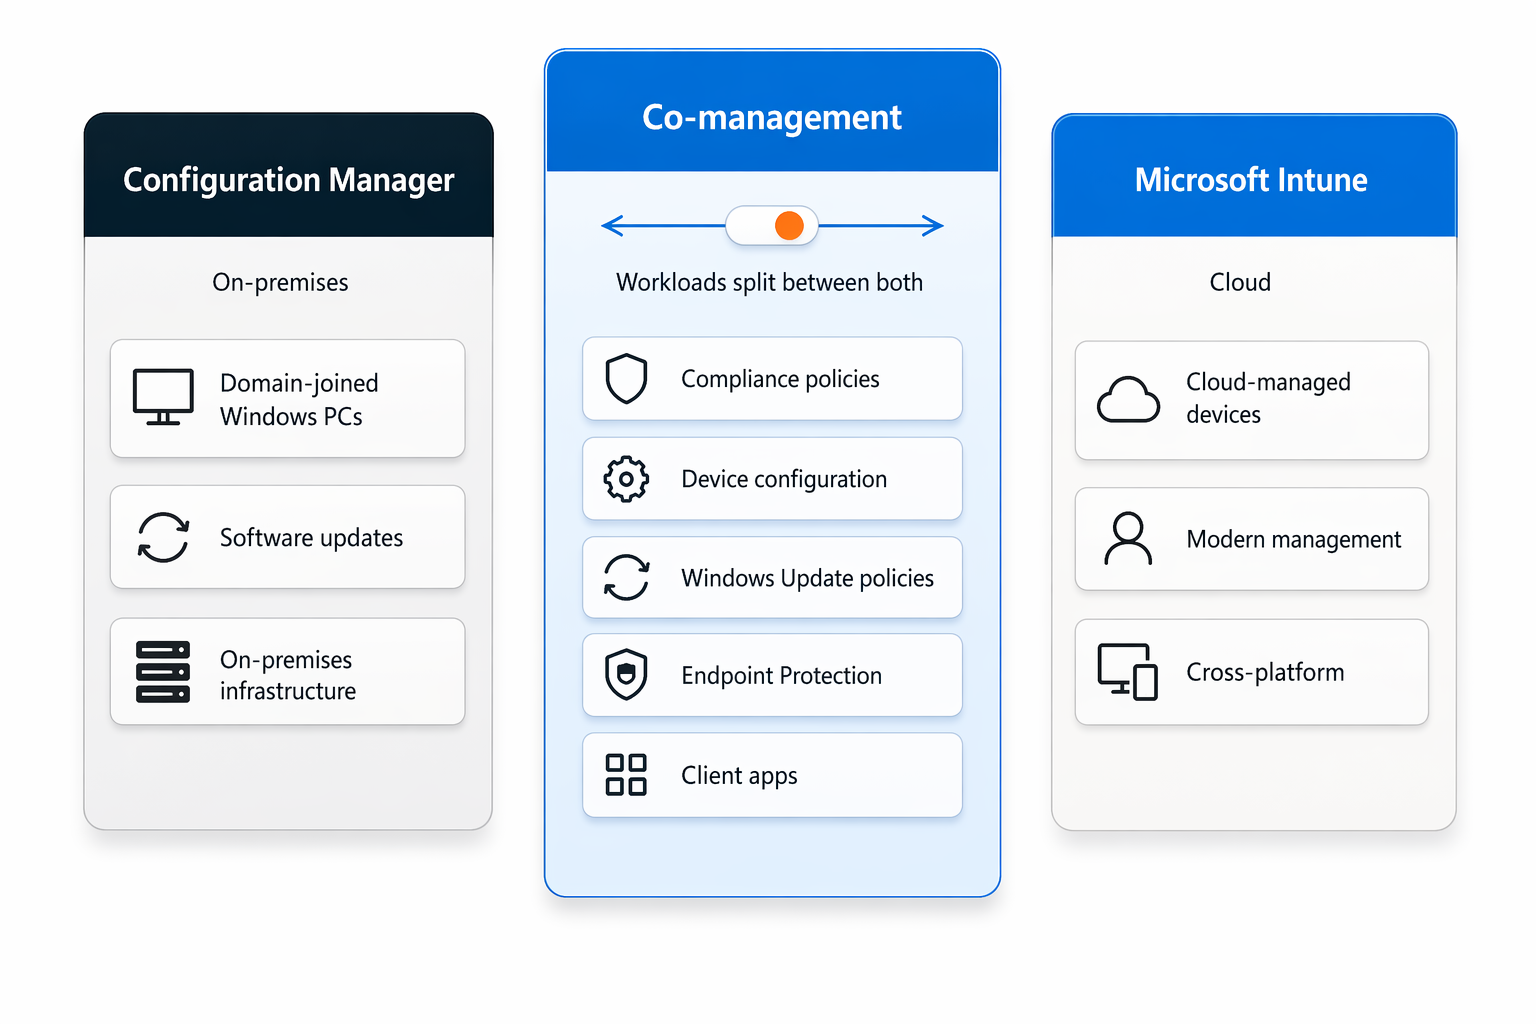
What does each solution manage?
| Feature | Configuration Manager | Intune | Co-management |
|---|---|---|---|
| Device management | Primarily on-premises, using a client that connects to the site server | Cloud-based, communicates over HTTPS | Devices are enrolled in both; workloads can shift to Intune over time |
| Supported platforms | Windows (extensive) | Windows, macOS, iOS/iPadOS, Android | Windows only (other platforms managed by Intune alone) |
| Policy delivery | Packages, software updates, Group Policy integration | Configuration profiles, compliance policies, MDM standards | Policies delivered by the active tool for each workload |
| Software deployment | Traditional MSI, scripts, packages | Modern app types: Win32, MSIX, Microsoft Store apps | Both models can coexist; Intune apps for new scenarios |
| Inventory and reporting | Deep hardware/software inventory with SQL Server Reporting Services | Cloud inventory with limited detail | Use the tool that holds the workload data |
Pros and cons
- Configuration Manager
- Pros: rich inventory, powerful scripting and customization, works offline
- Cons: expensive infrastructure, limited to Windows, requires on-premises servers and bandwidth
- Intune
- Pros: no on-premises servers, supports multiple operating systems, easier for remote/modern work
- Cons: less granular inventory, certain controls are still maturing, requires reliable internet
- Co-management
- Pros: allows phased migration, choose best tool per workload, protects investments in Configuration Manager
- Cons: added complexity, must manage dual-enrollment, not all workloads can be shifted (for example, Endpoint Protection)
When to choose which model?
- Cloud-first organizations with mostly mobile or remote users typically adopt Intune exclusively. They benefit from the simplicity of cloud management and cross-platform support.
- Large enterprises with existing Configuration Manager investments often start with co-management. They can migrate workloads such as compliance, device configuration, or Windows updates to Intune while keeping software deployment and imaging in Configuration Manager.
- Scenarios requiring deep control or offline management (isolated networks, specialized devices) still rely on Configuration Manager exclusively.
How co-management works in practice
To enable co-management, you first enroll a device in Intune while it's already managed by Configuration Manager. In the Configuration Manager console, you configure a co-management policy and select which workloads—such as Compliance policies, Resource Access policies, or Windows Update for Business—should be managed by Intune. The device receives settings from the tool that currently controls each workload.
Example scenario
Contoso has 10,000 corporate laptops managed by Configuration Manager. They want to start using Intune for compliance policies and remote assistance. By enabling co-management, they configure those workloads to move to Intune immediately while leaving software distribution and imaging handled by Configuration Manager. Over six months, as teams become comfortable with the cloud, they gradually shift more workloads until the devices are managed entirely through Intune.
The following short video animates that six-month journey, one workload at a time.
Understanding when each management strategy makes sense helps you plan a migration path using co-management.