Understand the role of Microsoft Entra ID in Intune
Microsoft Entra ID serves as the foundational identity service that powers Microsoft Intune's device management capabilities. It provides the essential user, group, and device identities that Intune relies on for authentication, authorization, and policy enforcement.
Microsoft Entra ID is Microsoft's cloud-based identity and access management solution that manages digital identities for users, devices, and applications. Without Microsoft Entra ID, Intune can't function because all device management operations depend on verified identities.
Why does Microsoft Entra ID matter for Intune?
Intune uses identity-based assignments for all its policies and configurations. Whether you deploy apps, enforce compliance, or control access, Entra ID ensures that the right resources are delivered to the right users and devices at the right time. This integration creates a secure, unified management experience across your organization.
How does Microsoft Entra ID work with Intune?
When you enroll a device in Intune, the process begins with Entra ID authentication. The device must first be registered or joined to Entra ID, creating a device object that Intune can reference. This device object contains critical information like the device type, ownership status, and join type.
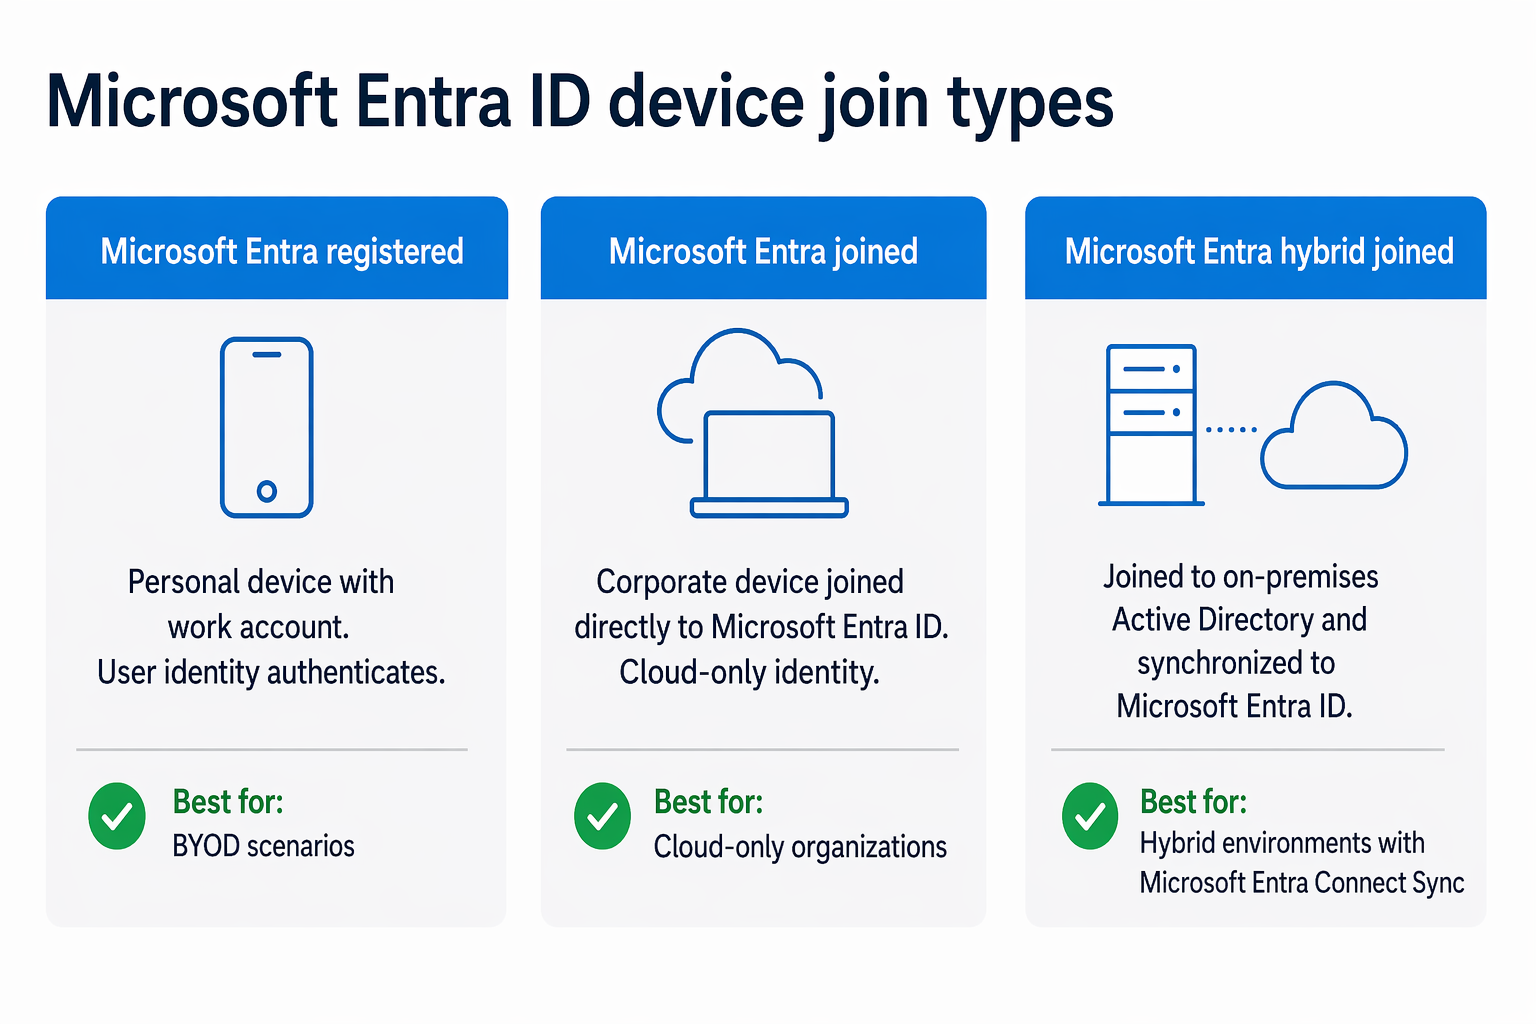
There are three main device join types in Entra ID that affect Intune management:
- Microsoft Entra registered: For personal or bring-your-own-device (BYOD) scenarios, providing light management through app protection policies
- Microsoft Entra joined: For cloud-only corporate devices, enabling full mobile device management (MDM) capabilities
- Hybrid Microsoft Entra joined: For devices connected to on-premises Active Directory, allowing co-management scenarios
The following diagram shows the three Microsoft Entra device join types and how they differ.
Intune uses these identities to assign policies. For example, you create groups in Entra ID and assign Intune policies to those groups, ensuring consistent management across your organization.
Authentication and token issuance are also handled by Entra ID. When users access resources, Entra ID issues tokens that verify their identity and device compliance status. Intune integrates with Conditional Access policies in Entra ID to enforce security requirements.
Key components of Microsoft Entra ID in Intune
- User identities: Enable enrollment and authentication for Intune
- Group identities: Organize users and devices for policy assignment
- Device identities: Track device information and compliance status
- Authentication tokens: Verify access rights and device state
- Conditional Access: Enforce security based on identity and compliance
Example scenario
Consider a healthcare organization that needs to protect patient data. They use Entra ID to manage identities and Intune to enforce device compliance. When a doctor tries to access medical records from a device, Entra ID checks the user's identity and the device's compliance status before granting access.
This integration ensures that only compliant devices can access sensitive resources, combining Entra ID's identity management with Intune's device control capabilities.