Примечание.
Для доступа к этой странице требуется авторизация. Вы можете попробовать войти или изменить каталоги.
Для доступа к этой странице требуется авторизация. Вы можете попробовать изменить каталоги.
Important
Work IQ Dev Tools (preview) - Work IQ Dev Tools (wiqd) are experimental, prerelease tools for building, validating, provisioning, packaging, publishing, evaluating, and monitoring Microsoft 365 Copilot declarative agents from the terminal. They're not production-ready or officially supported, and breaking changes are expected. For more information, see the Work IQ Dev Tools documentation.
Microsoft 365 Copilot supports federated Copilot connectors to enable organizations to connect their data to Copilot by using Model Context Protocol (MCP). Federated connectors use MCP to access data in real time, so Copilot can retrieve up-to-date information directly from external systems. This approach makes it easy to integrate live, dynamic data sources while keeping the data in its original location.
Where a connector provides the tools, Copilot can also create, update, or delete data in the connected system on the user's behalf.
Federated connectors can be Microsoft-published or submitted by partners to Microsoft for approval and publication in the Connectors Gallery.
By using federated connectors, organizations can extend Copilot to work seamlessly with their existing tools and data to unlock more relevant and timely insights across their workflows.
Note
Support for write, update, and delete actions begins rolling out in early October 2026. For availability by Copilot experience, see Write, update, and delete actions.
What are federated connectors?
Federated Copilot connectors:
- Use Model Context Protocol (MCP) to fetch data in real time.
- Access data using the user's identity and permissions.
- Don't index external data into Microsoft 365.
- Are managed and governed by admins in the Microsoft 365 admin center.
- Can be Microsoft-published or partner-submitted and Microsoft-approved.
- Can read data and, where a connector provides the tools, create, update, or delete data with the user's approval. Admins can audit activity in Microsoft Purview.
Supported Copilot experiences
Microsoft 365 Copilot supports federated Copilot connectors in the following experiences:
- Microsoft 365 Copilot Chat
- Agents
- Cowork
- Copilot in Word, Excel, PowerPoint, and Outlook
- Researcher agent
The Researcher agent doesn't support write, update, or delete actions. Federated Copilot connectors remain read-only in this experience.
Federated connectors in the Connectors Gallery
Microsoft provides a set of federated connectors in the Connectors Gallery. These connectors can be Microsoft-published or submitted by partners and approved by Microsoft.
Currently, federated connectors are available for the following data sources, organized by category:
| Category | Data sources |
|---|---|
| Accounting and finance | Aiwyn Tax, CB Insights, Clarity AI, D&B Finance Analytics, D&B Risk Analytics, DiligenceSquared, FactSet, FinancialReports, Fiscal.ai, Fitch Solutions, Klardaten DATEV-Connector, LSEG, Mercury, Money Forward, Moody's, Morningstar, Morningstar Credit Analytics, MT Newswires, PrivCo, Quartr, S&P Kensho, Square, Syrto, Xero, Zacks, Zoho Books |
| Collaboration | Gmail, Linear, Miro, TeamsMaestro, Trello |
| Content management | PandaDoc, Templafy, TextMine |
| CRM | Clarify, HubSpot, Intercom |
| Data analytics | Amass, ARC Advisory AI, Ask Rystad, AskPolly, Contentsquare, DecisionPoint, Dovetail, EIU, IBISWorld, IDC, Mixpanel, MoSPI, Optiq Bridge US, Polar Analytics, Pulse by PassBy, Resilinc, S&P Global Energy, Statista, Synapse.org, Tastewise, Trellis, Wolfram |
| Site design | Canva, Cloudinary, Excalidraw, Mobbin, Trimble SketchUp, Webflow |
| IT management tools | Apify, Clerk, Context7, Enosix, GoDaddy, GraphOS MCP Tools, Hugging Face, Jam, pg-aiguide |
| Training and tutorial | Article Galaxy, Articulate, Articulate EU, Autodesk Product Help, Learn365, Microsoft Learn, Padlet, QuizFlight, Scite, Siemens |
| Files and documents | Box, Egnyte |
| Health and life sciences | BioRender, CAS Connections, ClinicalTrials.gov, CMS Coverage, CMS Drug Data, CMS NPI Registry, Consensus, Cortellis Regulatory Intelligence, FDA Safety (openFDA), NyquistAI, Open Targets, PopHIVE, SciLeads, Smarts.bio |
| Legal + HR and recruiting | BoardWise, Courtroom5, Descrybe Legal Engine, Dice, DirectCase Legal Search, Everlaw, Gusto, Harvey, Harvey AU, Harvey EU, iManage Work, Lawstronaut, Legal Data Hunter, LegalZoom, Litera, Midpage Legal Research, NetDocuments US, Relativity, SeekOut, Teamtailor, ZipRecruiter |
| IT service management tools | Cloudflare, Malwarebytes |
| Reference | AllTrails, bioRxiv, Blackbaud, ChEMBL, DrugBank, eSIM Copilot, Fibre2Fashion, Granted, ICD-10 Diagnosis Codes, Kindora Funder Discovery, MedlinePlus, Melon, PubMed, RxNorm & Drug Classes (NLM), SiteTrax.io, Stable Baseline, Tavily, Viator |
| Productivity | Airtable, DeepL MCP, Fellow.ai, Fireflies, Gamma, GoLinks, Goodnotes, Google Calendar, Google Contacts, Granola, Mem, Memoket, Notion, SlidesGPT, Taskrabbit Booking Assistance |
| Project management | Asana, awork, Dotted, Flow Studio Cowork, Make, monday.com, Nozbe, Onplana, Quire, Smartsheet, Strety |
| Sales and marketing | Adobe Journey Optimizer, Ahrefs, Bigmind, Crossbeam, Customer.io, Grain, HG Insights, Highspot, Local Falcon, MailerLite, Sprouts.ai |
ISVs use a single connector manifest and single publishing pipeline for all connector types. For more information, see ISV success guidance.
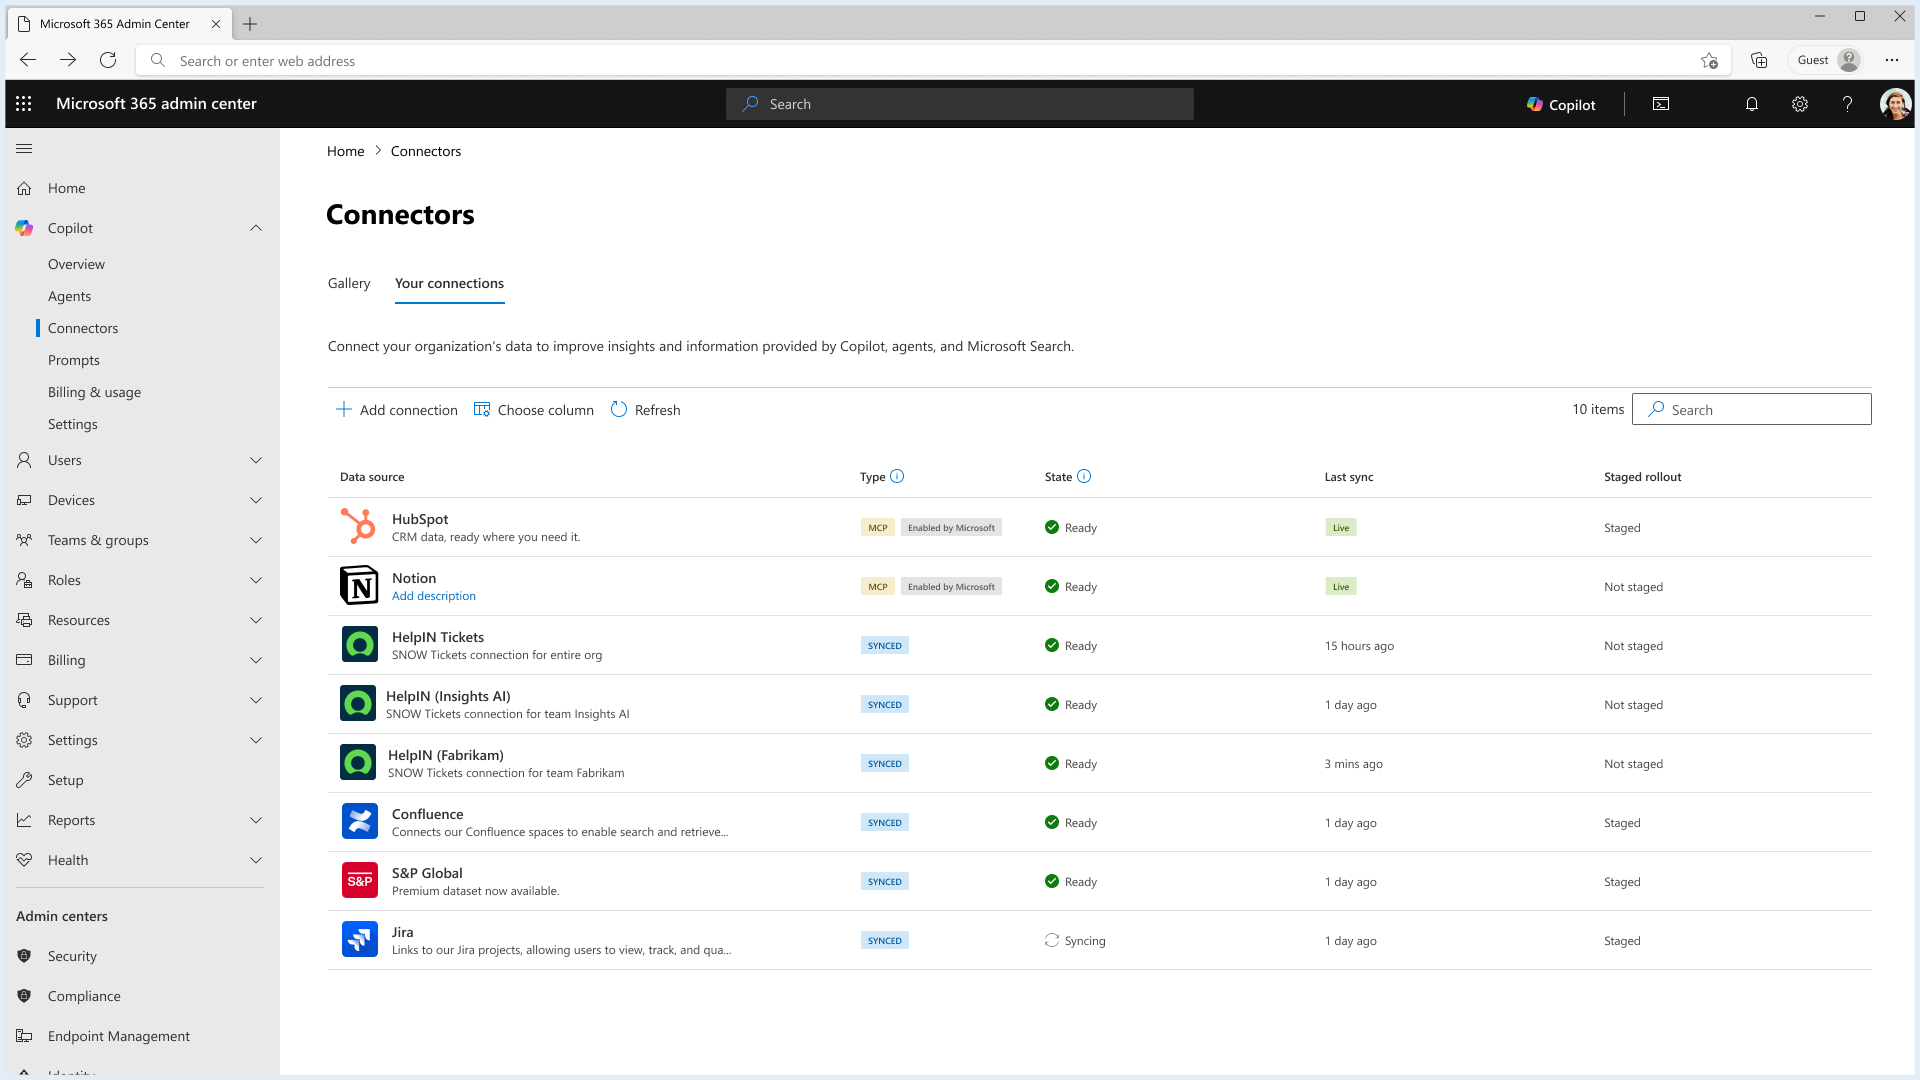
The following image shows federated connectors in the Your connections list in the Microsoft 365 admin center.
Important
Admins control whether default federated connectors are available to their organization from the Settings tab in Agent 365, by using the Allowed agent types. When the Microsoft-published and third-party-published options are deselected, federated connectors aren't enabled by default in the tenant, including connectors released in the future, and the admin enables each connector individually. This setting replaces the tenant-wide PowerShell toggle. Tenants that previously used the cmdlet receive a Message Center post asking them to reapply the choice in the UX within a limited window, after which the cmdlet state is no longer honored. For more information, see Manage federated connectors.
Admin experience and controls
Microsoft-published federated connectors are enabled by default for a tenant unless admins disable them. Admins must approve partner federated connectors before enabling them for the organization. Admins can manage federated Copilot connectors in the Microsoft 365 admin center by choosing Copilot connectors > Your connections.
Administrators can manage Microsoft 365 Copilot connectors, synchronized connectors, federated connectors, and supported Cowork plugins from a single location: Copilot connectors > Your connections.
Admins can:
- View federated connectors that are available in the tenant on the Your connections tab, including Microsoft-published connectors and partner connectors that Microsoft approved and the admin enabled.
- Enable or disable connectors at the tenant level.
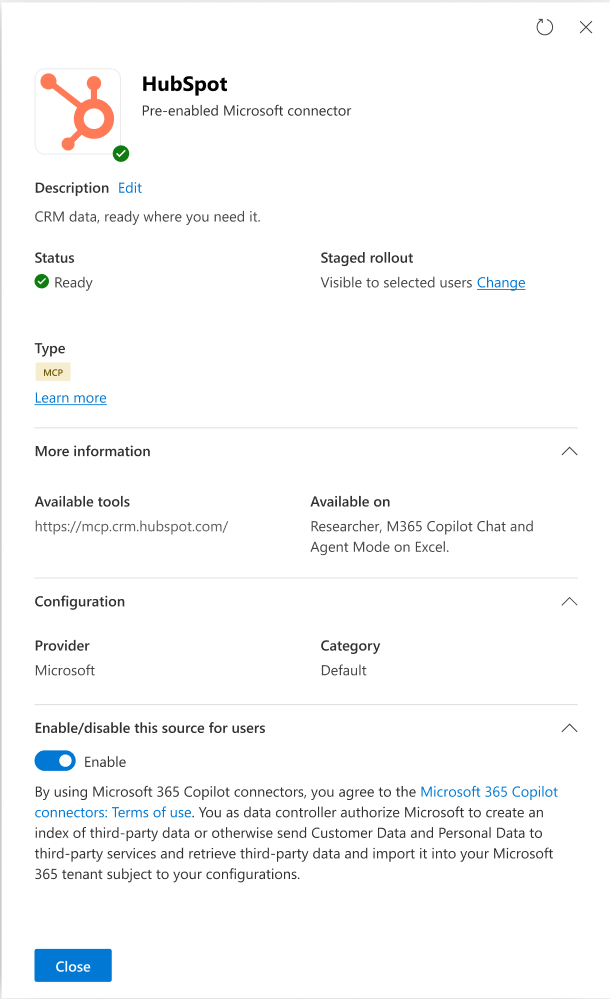
- Limit availability to specific Microsoft Entra ID groups by choosing Add staging in the Staged Rollout column.
- Bulk disable all federated connectors by using Allowed Agent Type, and selectively enable specific federated connectors in the Microsoft 365 admin center based on organizational policies and readiness. For more information, see Manage federated connectors.
- Manage federated connectors from the Agent tab in the Microsoft 365 admin center portal apart from the Copilot connectors > Your connections section.
Write, update, and delete tools are part of the connector and aren't enabled separately.
The following image shows the connector pane for the HubSpot federated connector.
View a connector's tools in the admin center (Coming soon)
For connectors that support this feature, the details page in the Microsoft 365 admin center includes a Tools section that lists the tools available to users in the organization, including tools that can modify or delete data. To view the tools:
In the Microsoft 365 admin center, go to Copilot connectors > Your connections and select the federated connector.
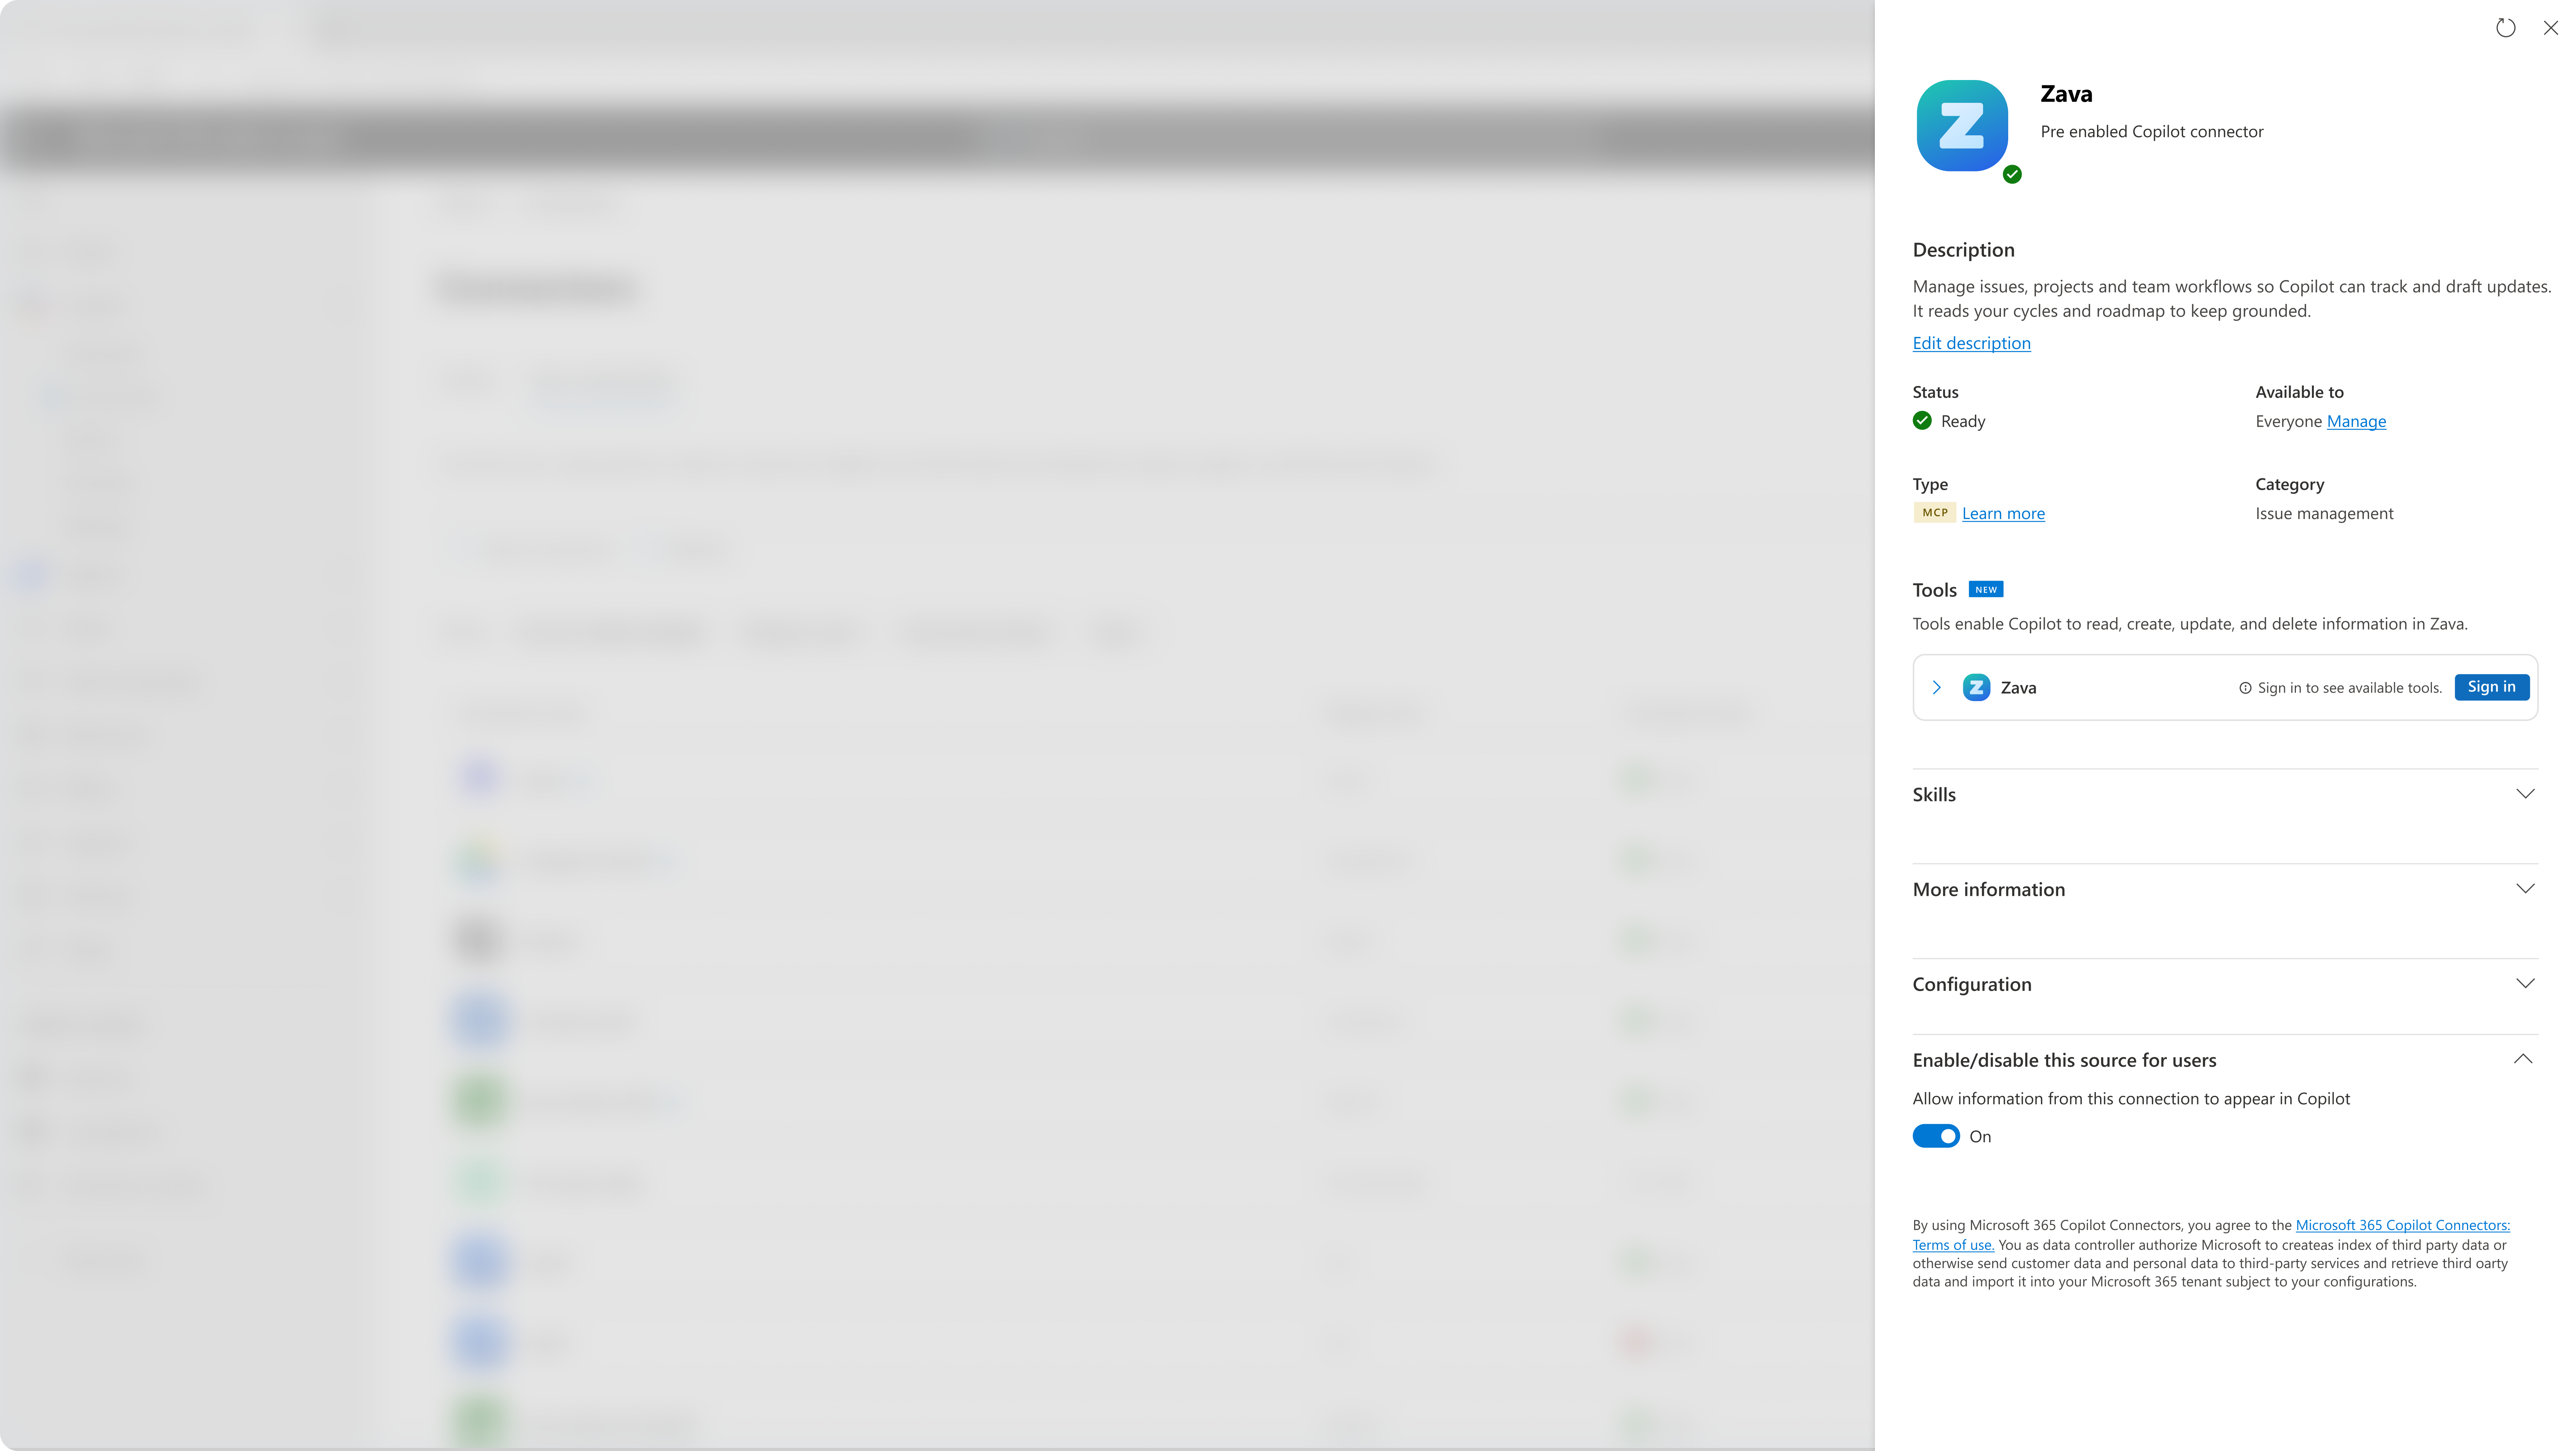
On the connector's details page, go to the Tools section and sign in to the third-party service.
Signing in to view a connector's tools in the Microsoft 365 admin center might also sign you in to that connector in Microsoft 365 Copilot.
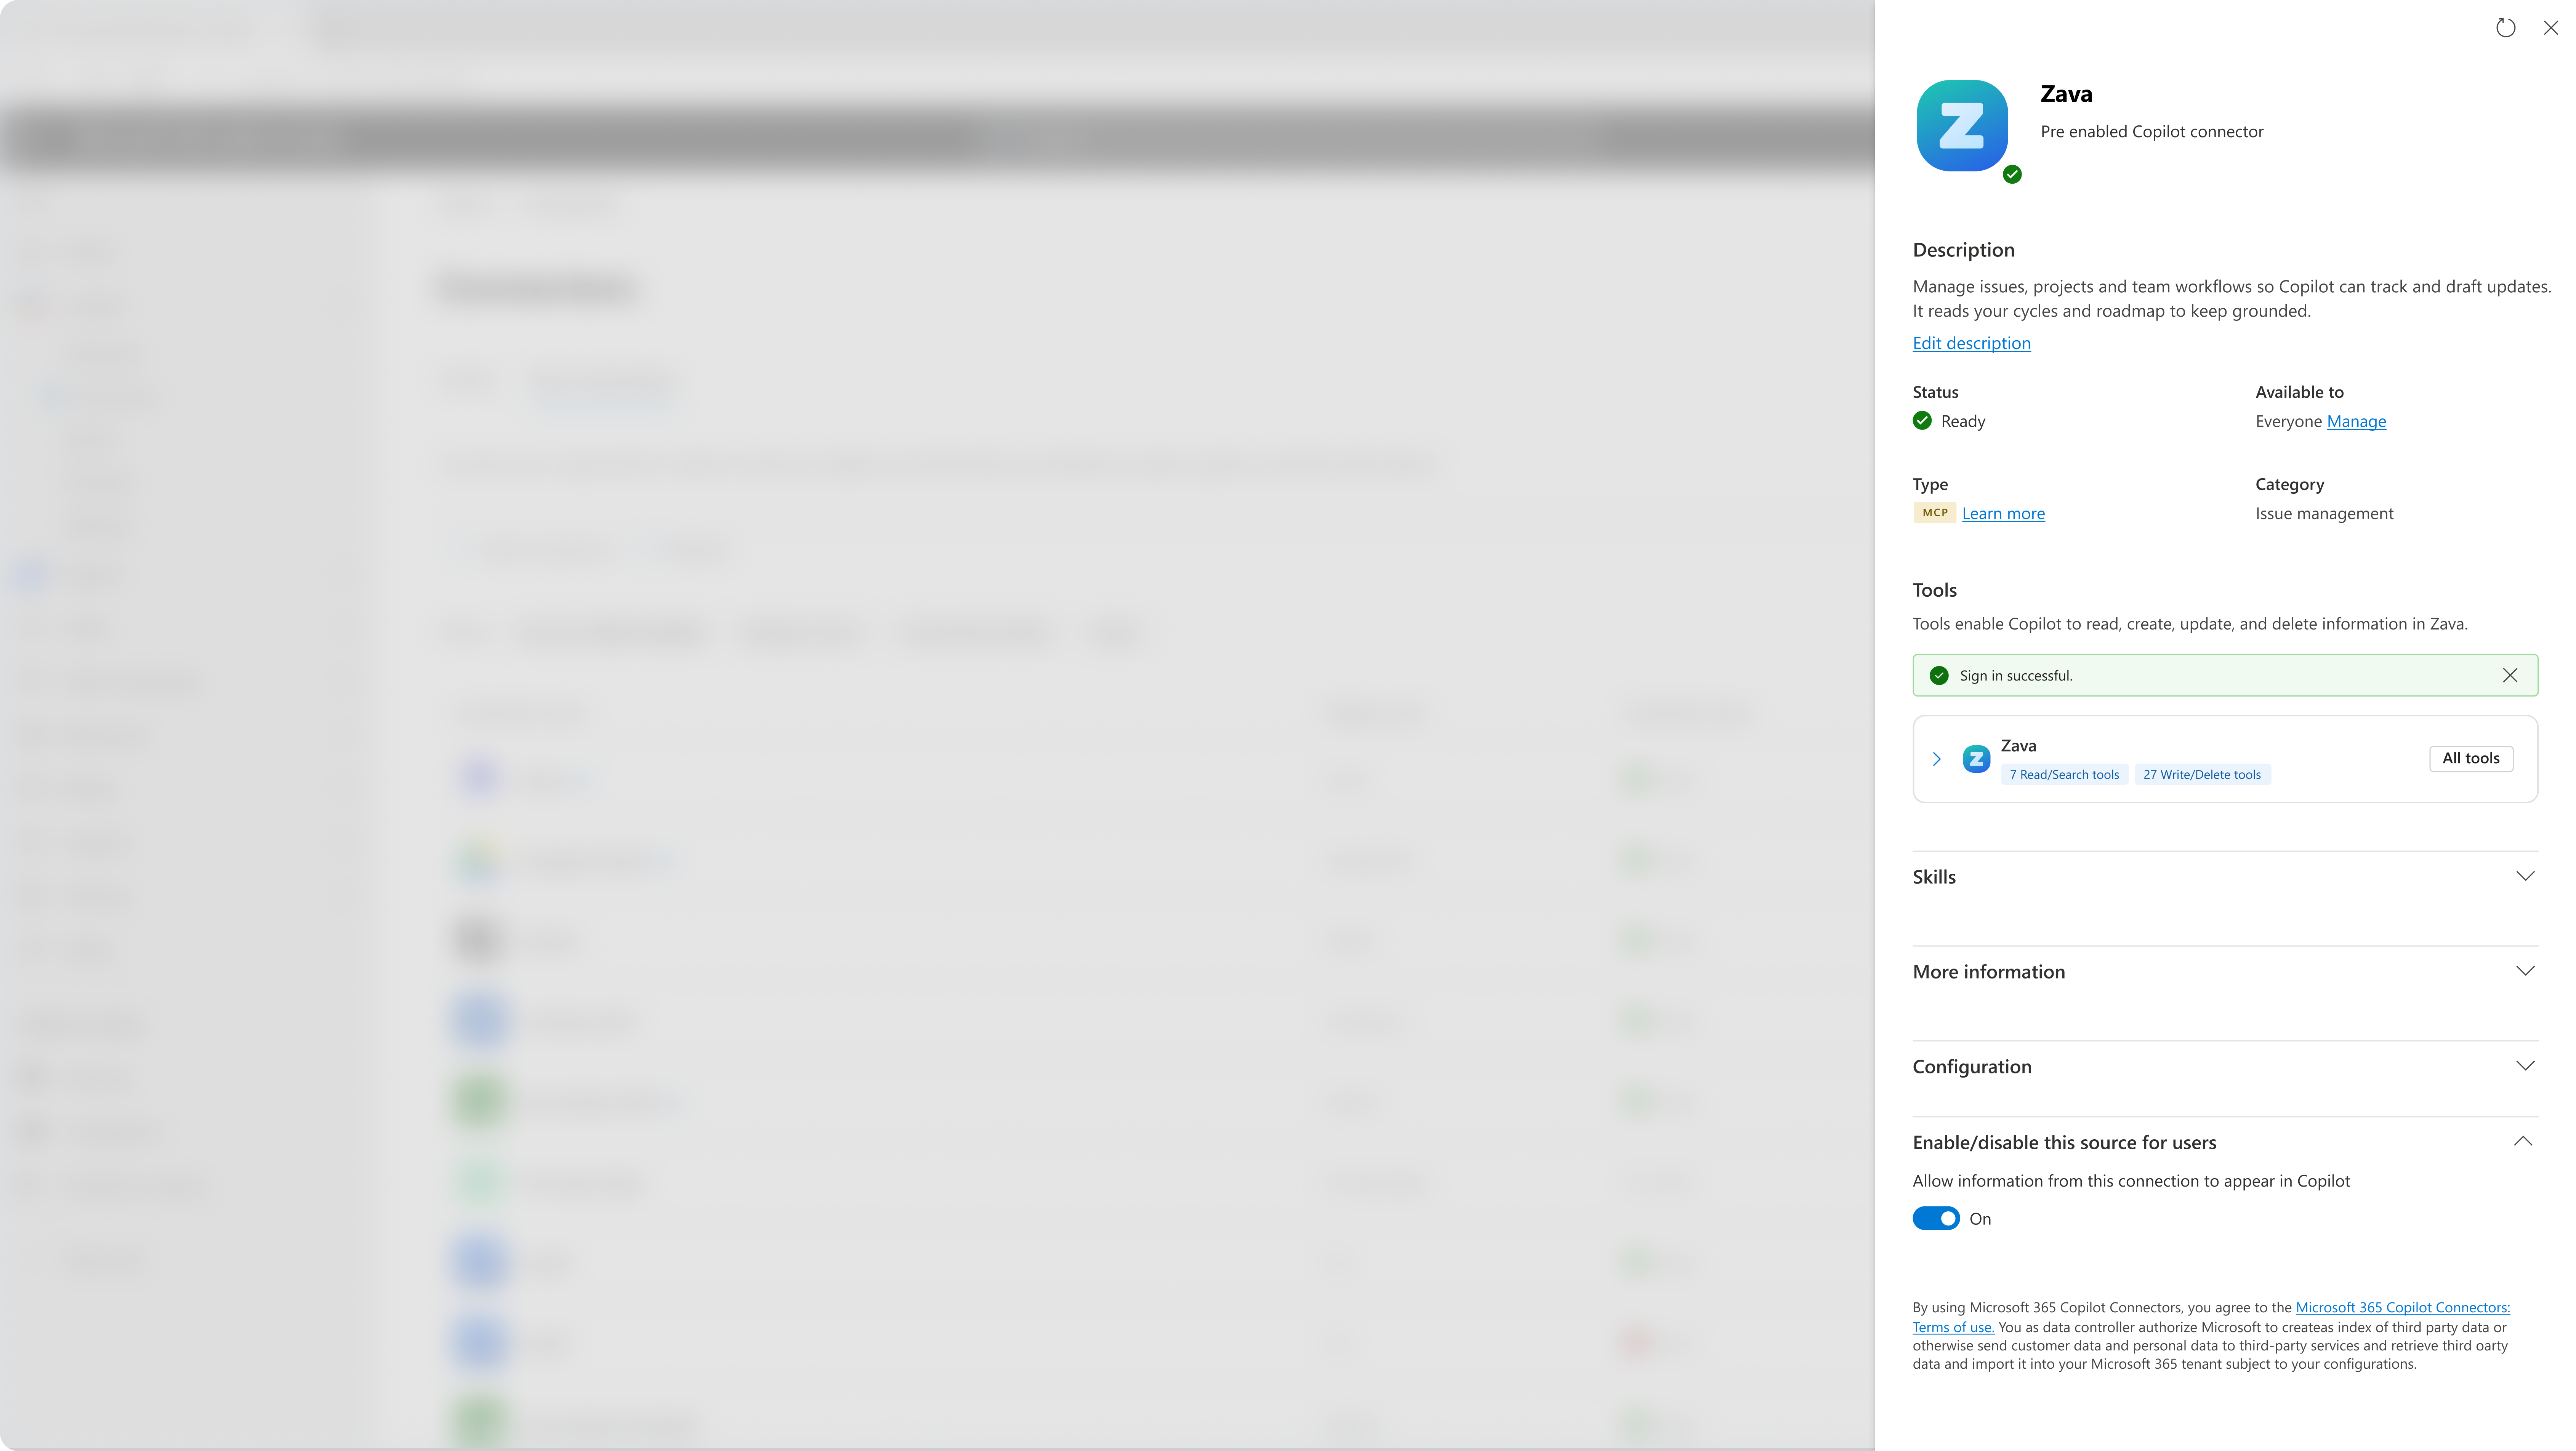
Select All tools, and then review the list to identify tools that can create, update, or delete data.
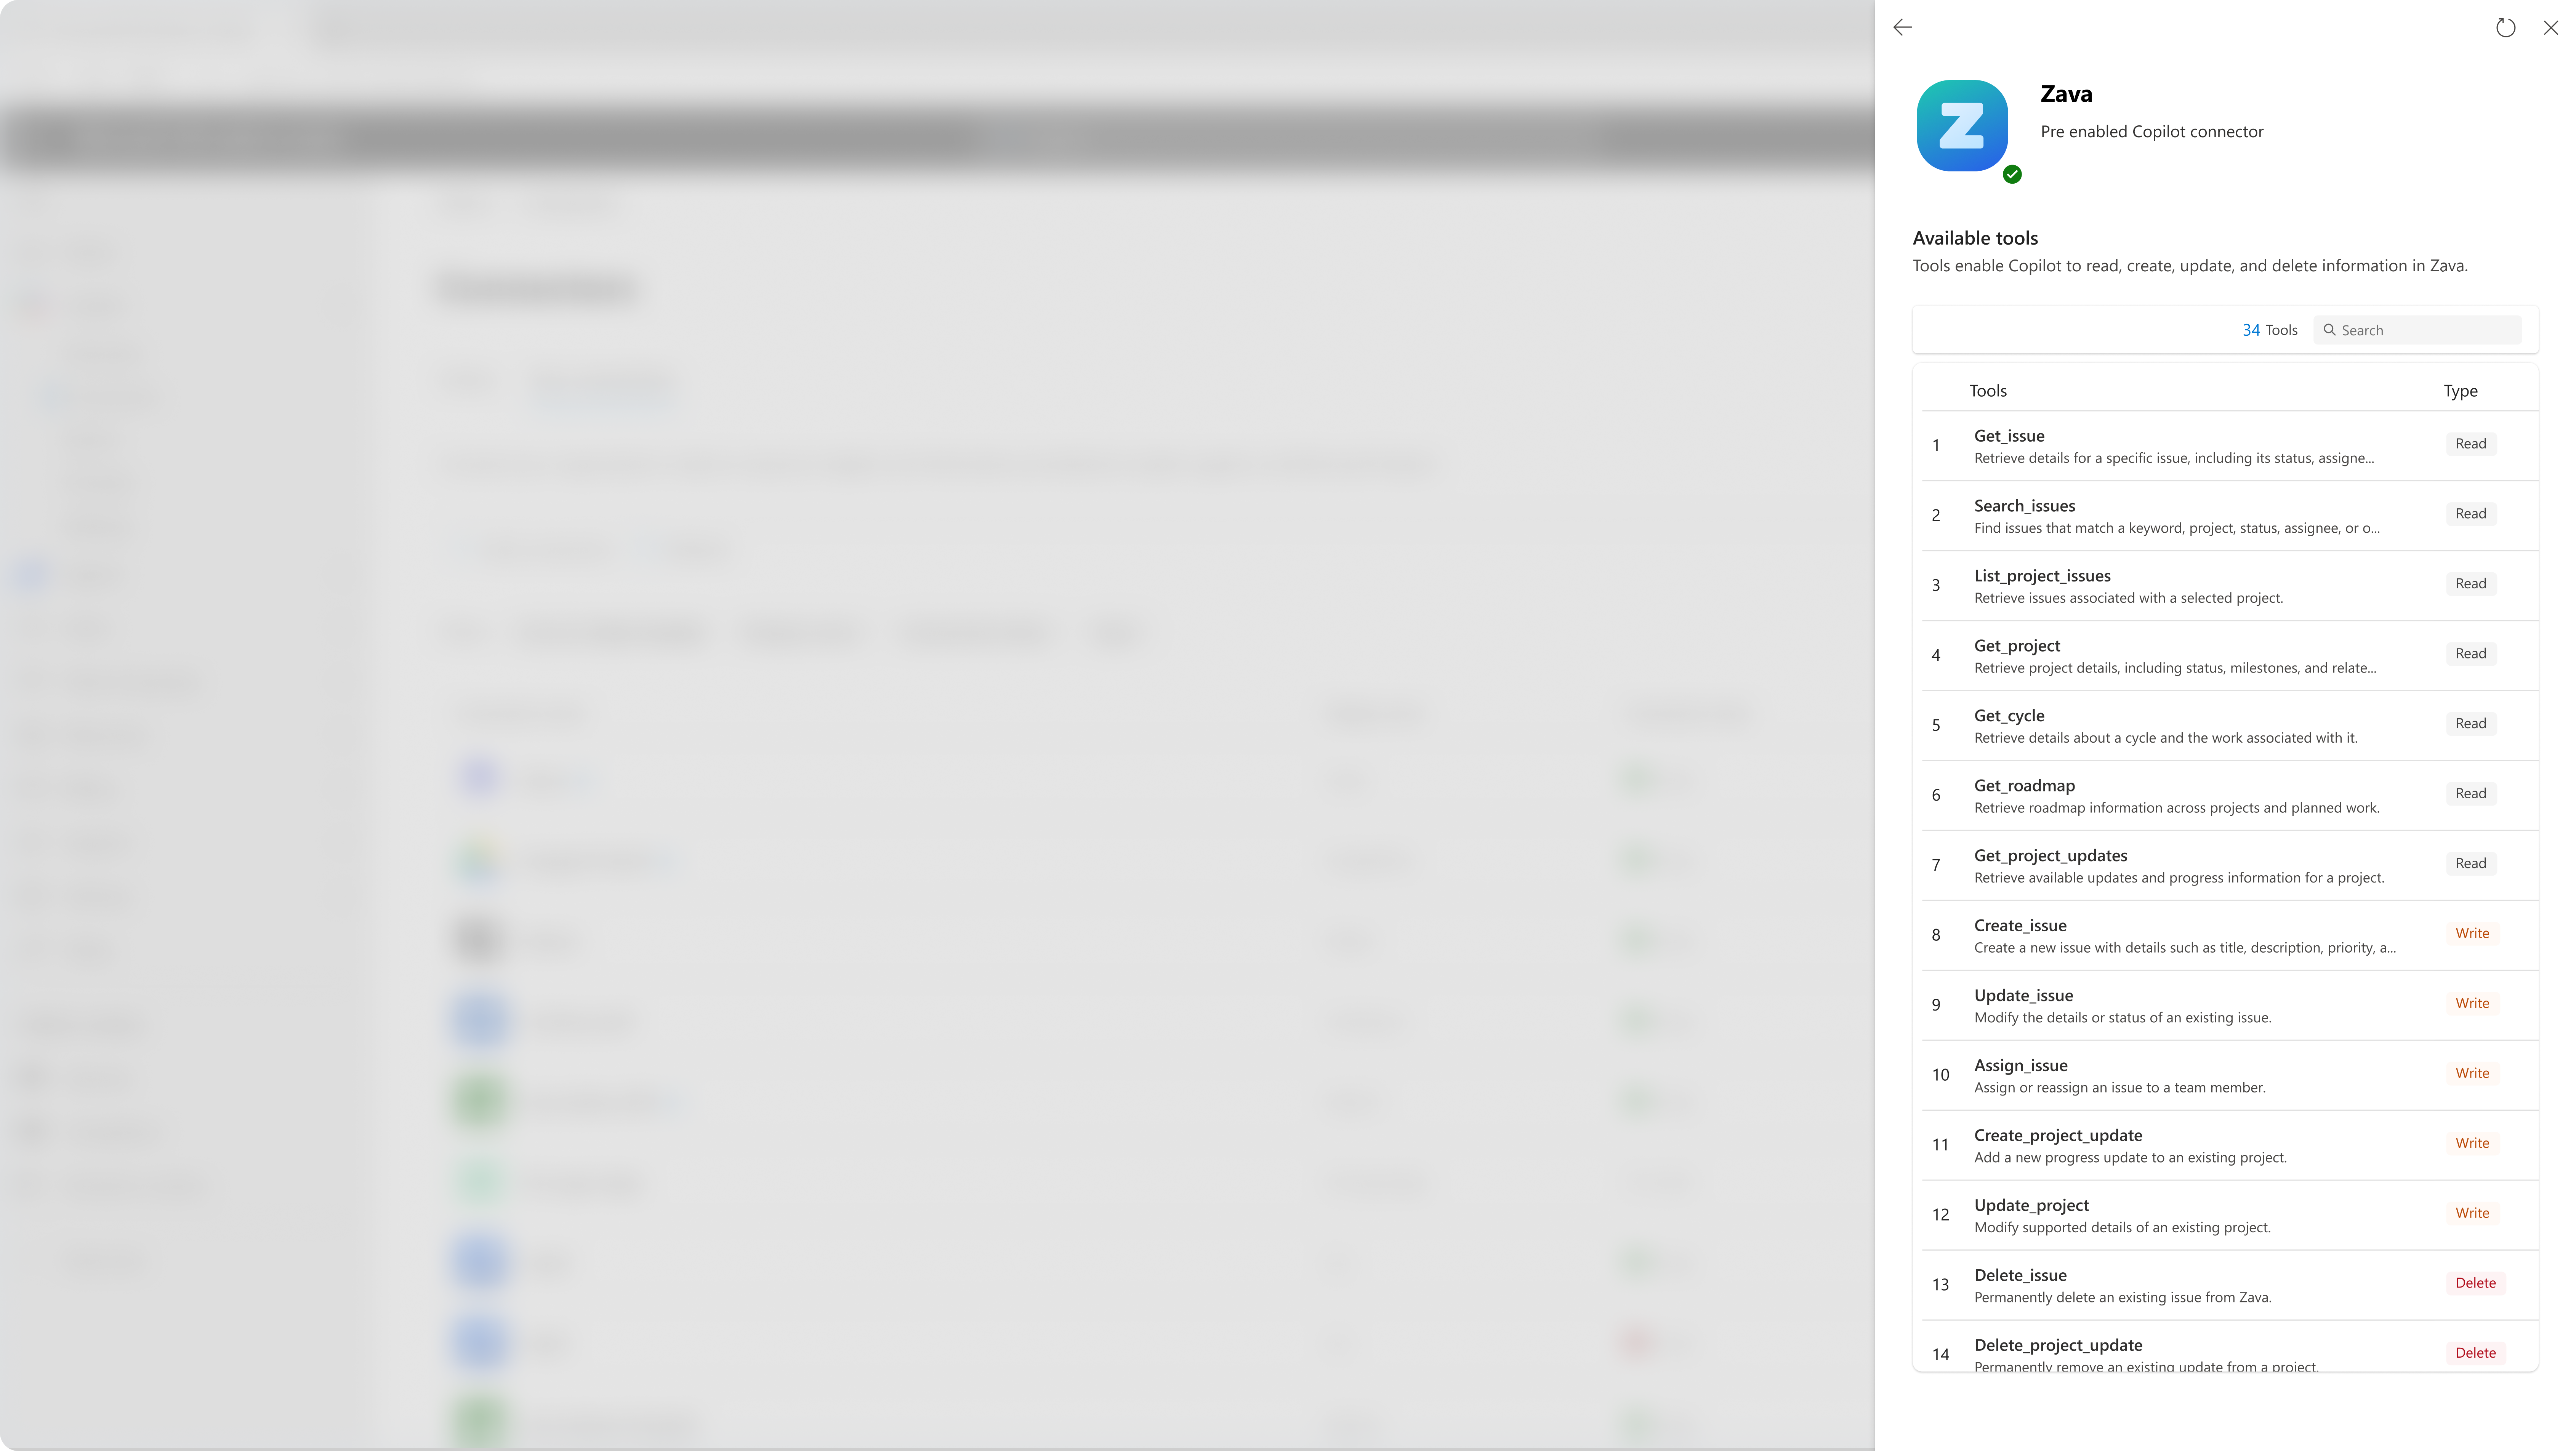
Note
The tool list reflects the permissions of the account used to sign in. Sign in by using an account that has a high level of access to the connector so you see the comprehensive list of tools.
Viewing tools in the admin center isn't available for all connectors. If you encounter issues, sign in to Microsoft 365 Copilot with your user account, go to Settings -> Sources, and select the connector. Then expand Write/Delete tools. For details, see Review individual tool permissions.
Before enabling or continuing to use a connector that exposes write, update, or delete tools, review the connector's capabilities, privacy terms, and third-party agreements against your organization's security, compliance, and acceptable-use requirements. Update user and help-desk guidance so users understand that actions are performed using their own permissions in the third-party service.
How to connect and use federated Copilot connectors
When an admin enables a federated connector:
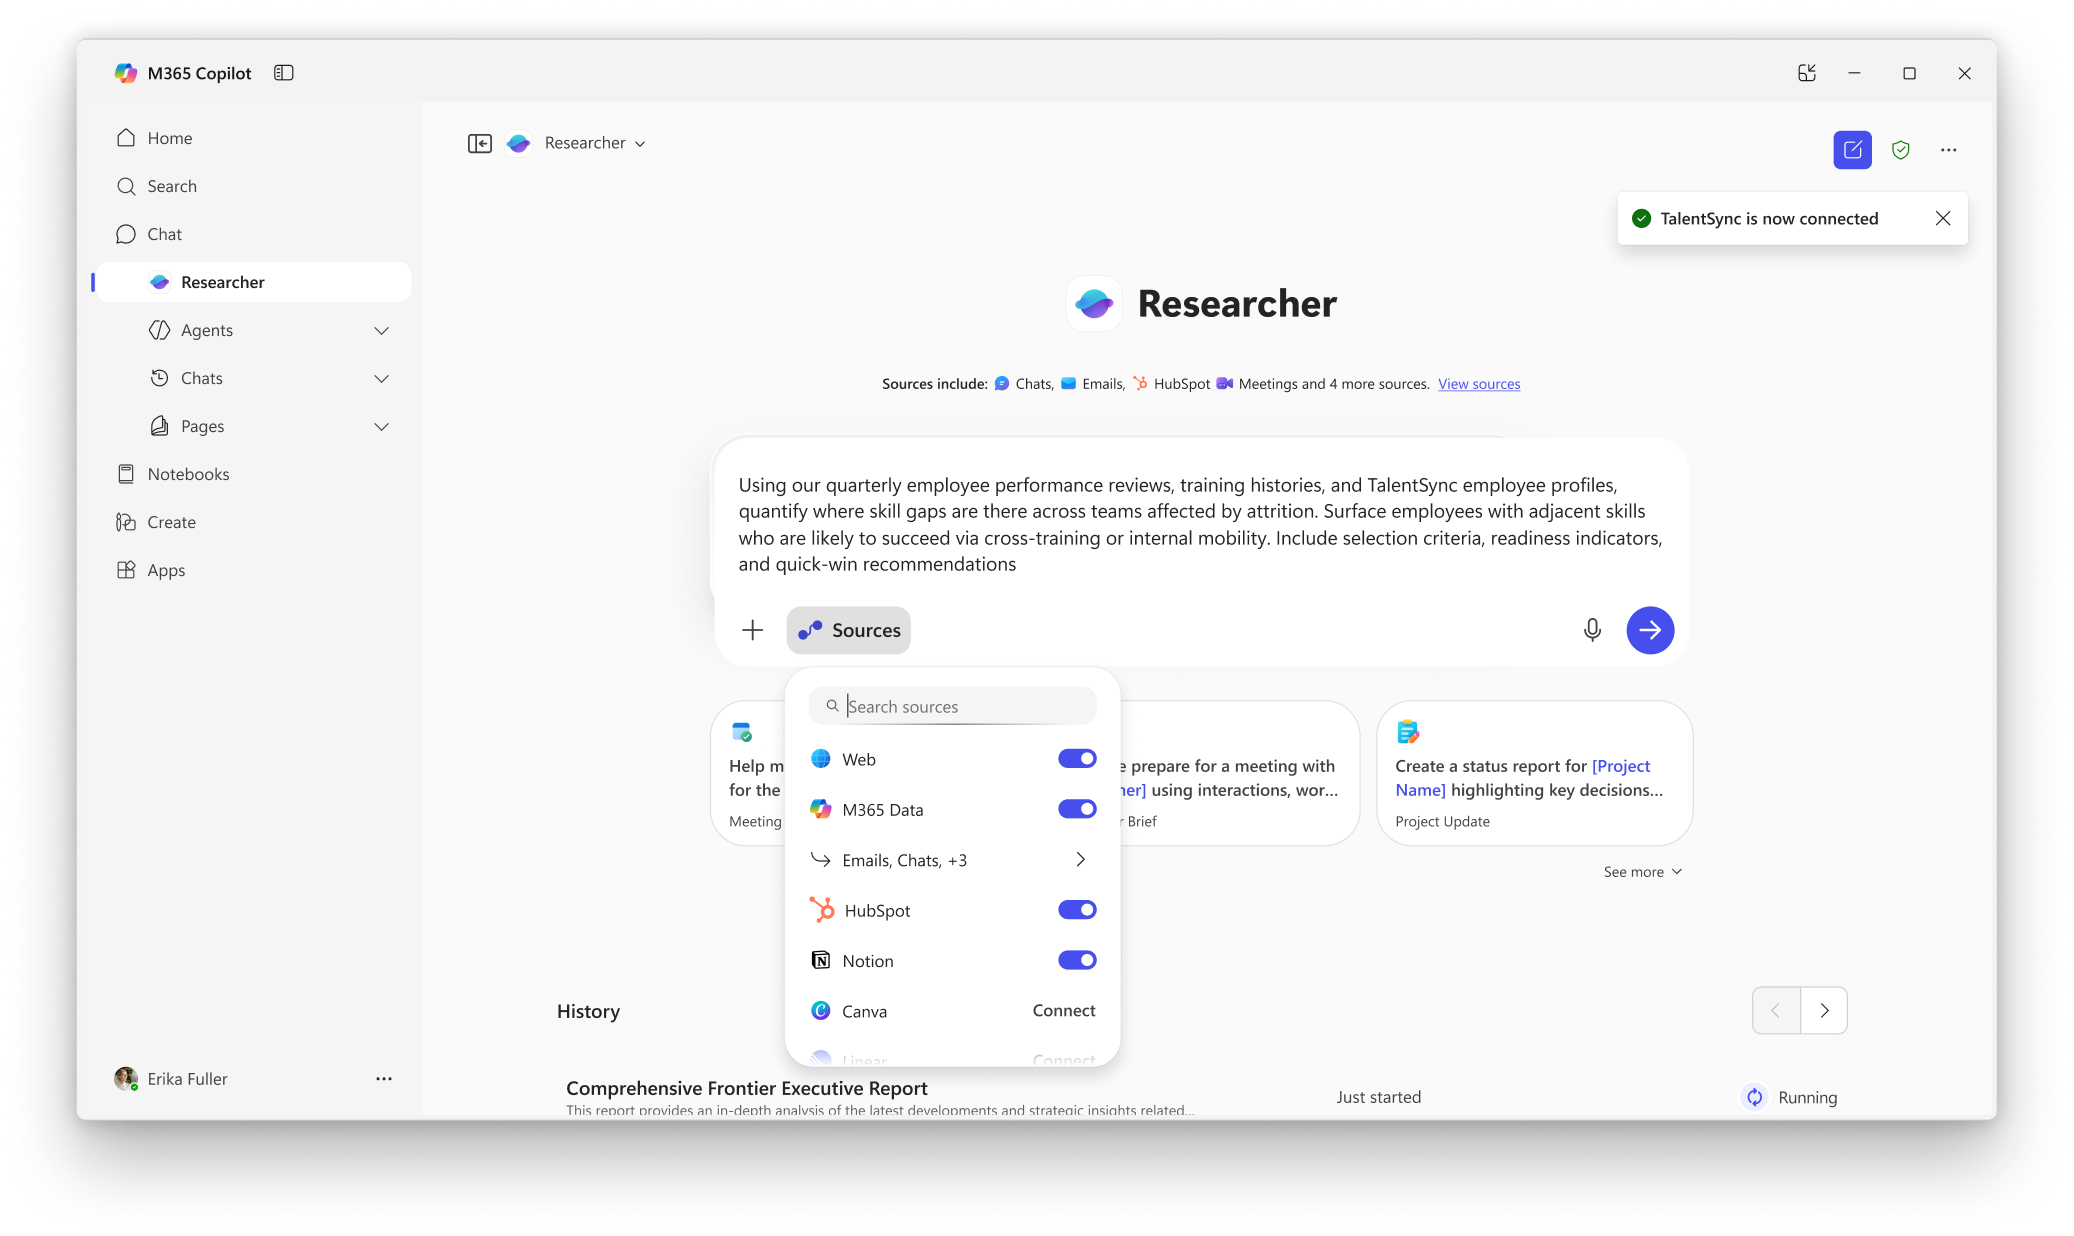
- Users can discover the data source in the Sources menu in the Researcher agent, in deep research mode in Microsoft 365 Copilot chat, and in Copilot Chat where available.
- Users authenticate by using their own credentials when prompted to connect to the data sources.
- Copilot only accesses data the user already has permission to see and makes changes the user is already permitted to make.
- Users can disable the data source at any time by turning off the source in Researcher or by managing the source in Copilot Chat settings.
Connect to federated connectors in Copilot Chat
Where Copilot Chat is available for users, they can connect federated data sources directly from chat settings:
- Open Microsoft 365 Copilot Chat.
- Select the ellipsis (...) menu, and then select Settings.
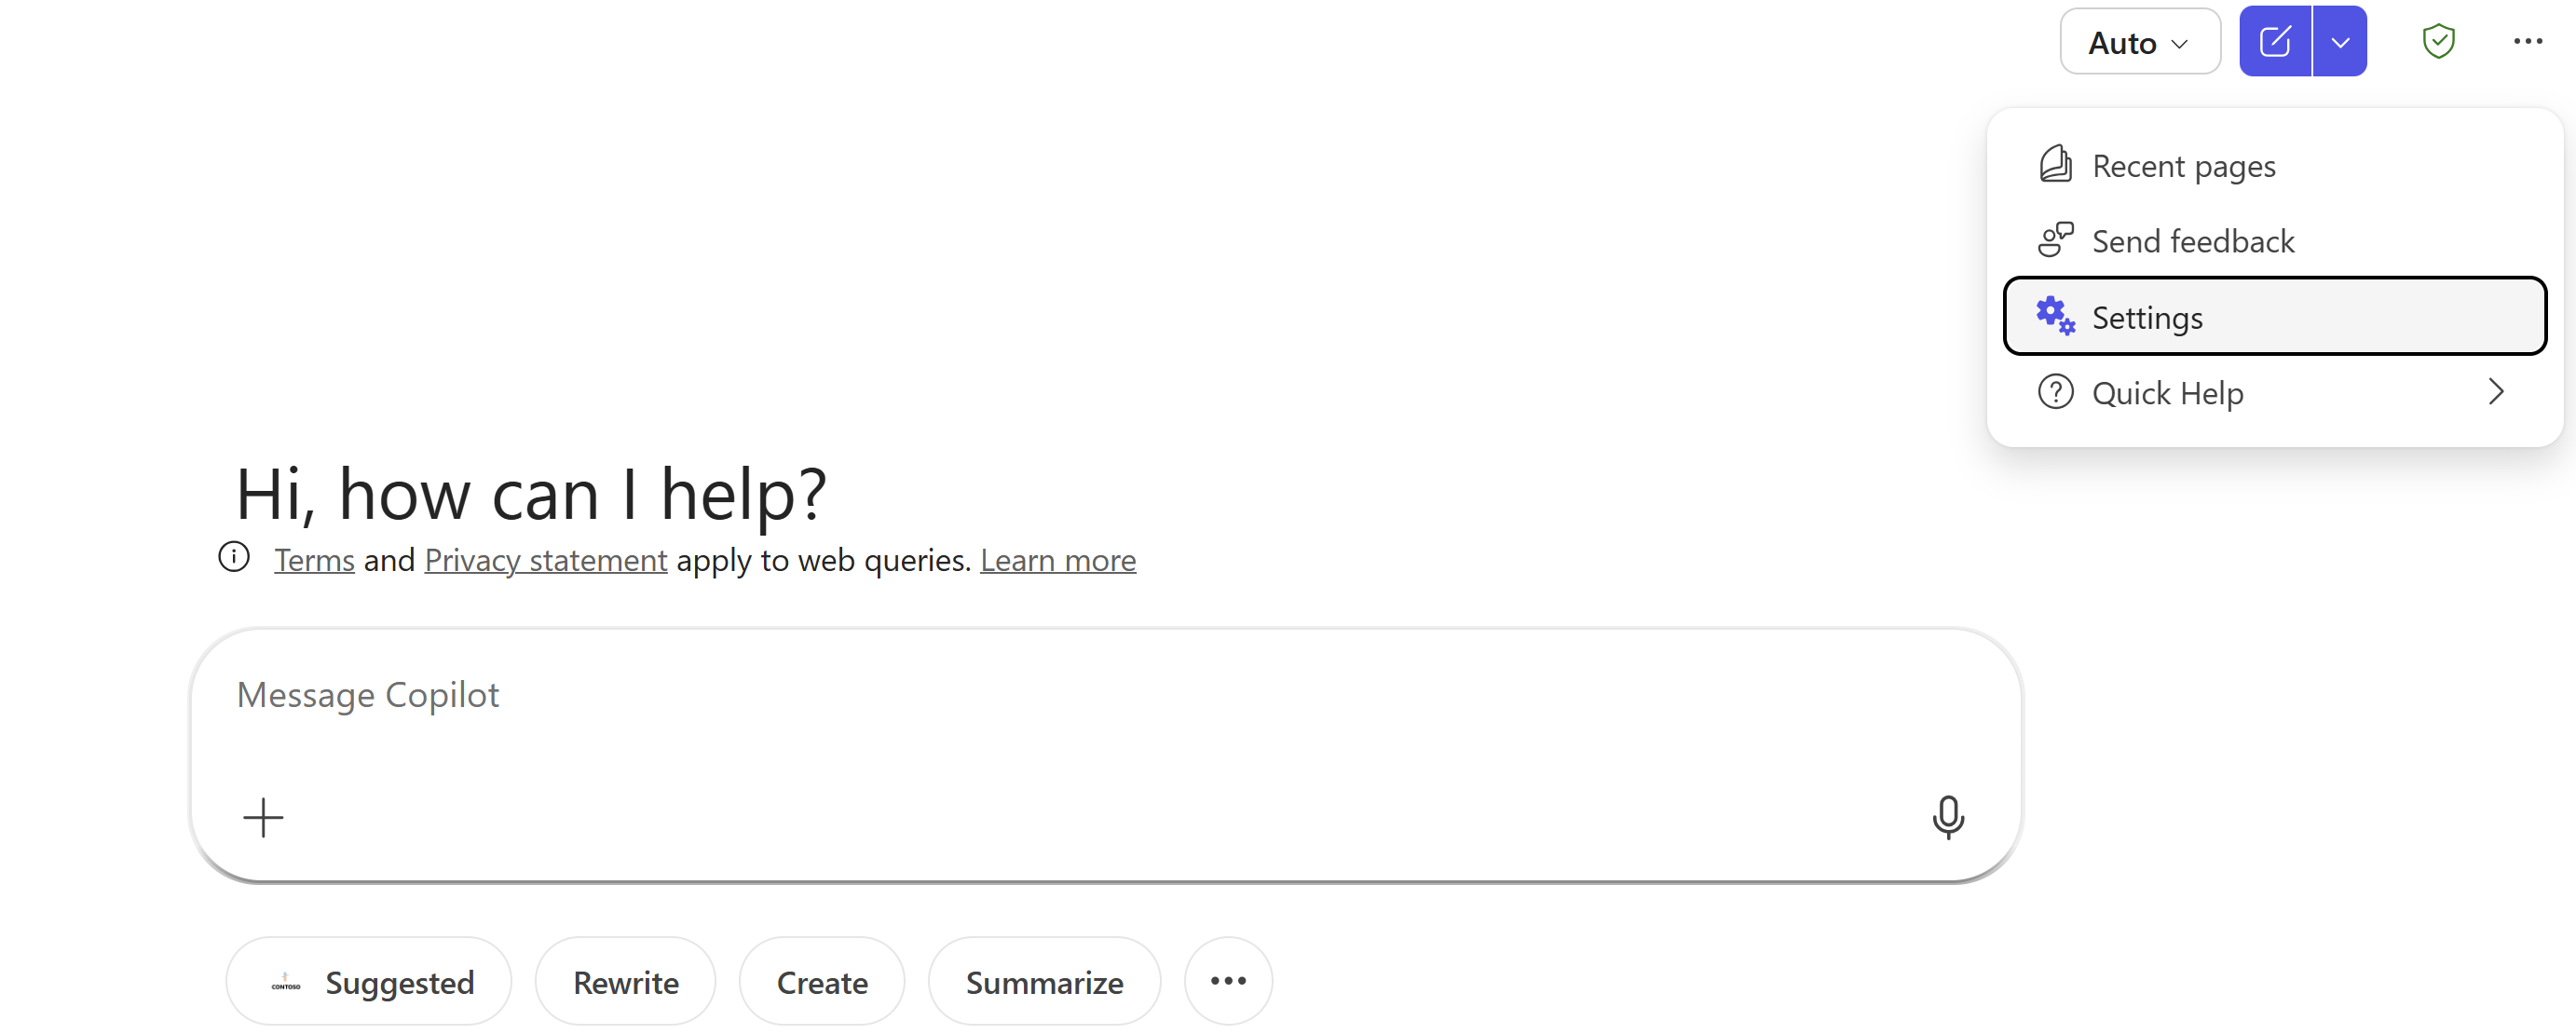
- In the settings dialog, select Sources in the left pane.
- Find the external data source you want to use, select Connect, and complete authentication.
- Enter your prompt directly in Copilot Chat.
Note
No data is indexed into Microsoft 365. Responses are fetched dynamically from the data source via MCP.
The following image shows how the user accesses federated connector data sources in Researcher.
Dynamic tooling through MCP
Dynamic tooling enables Microsoft 365 Copilot to retrieve information from connected systems and take actions in them at runtime based on a user's request.
The MCP server associated with the federated connector determines tool availability. When appropriate, Microsoft 365 Copilot dynamically selects relevant tools to retrieve information or perform an action.
The authenticated user's identity and permissions in the source system govern tool access. Users can only access information they're authorized to view and change data they're authorized to modify.
Tools that create, update, or delete data require user approval. For confirmation options and tool permissions, see Write, update, and delete actions.
Examples of read operations through dynamic tooling include:
- Searching knowledge repositories
- Looking up records in line-of-business applications
- Retrieving project or operational status
- Querying customer, product, or support information
- Accessing specialized search capabilities exposed by a source system
Dynamic tooling doesn't index external data into Microsoft 365.
Write, update, and delete actions (Coming soon)
With federated connectors, users can do more than retrieve information. When a connector provides the appropriate tools, users can ask Microsoft 365 Copilot to create, update, or delete information in a connected third-party system on their behalf. Users can complete work without leaving Copilot. For example, a user can turn an escalation email into an issue in a project-tracking tool, update a record in a customer relationship management (CRM) system, or add a comment to a ticket directly from Copilot Chat.
Write, update, and delete actions follow the same federated connector model as read tools:
- Actions run in the third-party service on behalf of the user and are limited by that user's permissions. Copilot can change only what the user is already permitted to change in the source system.
- No data is indexed into Microsoft 365. Copilot sends the connector the information it needs to complete the action and returns the outcome to the user.
- Tools that create, update, or delete data initially require the user's explicit approval. Users can choose whether Copilot asks again for that tool, as described in Confirm an action. Actions that the user declines aren't performed.
- The actions available through a connector depend on the tools exposed by the connector publisher. Publishers can add or change tools over time.
Confirm an action
Users must be connected to the third-party service before Copilot can use any authenticated capabilities that the connector provides, including tools that create, update, or delete data.
These actions export Customer Data to the connected system to create, update, delete, or otherwise modify data. While an action is awaiting confirmation, nothing is sent to the connected system until the user responds. Read tools don't require confirmation and continue to run as they do today.
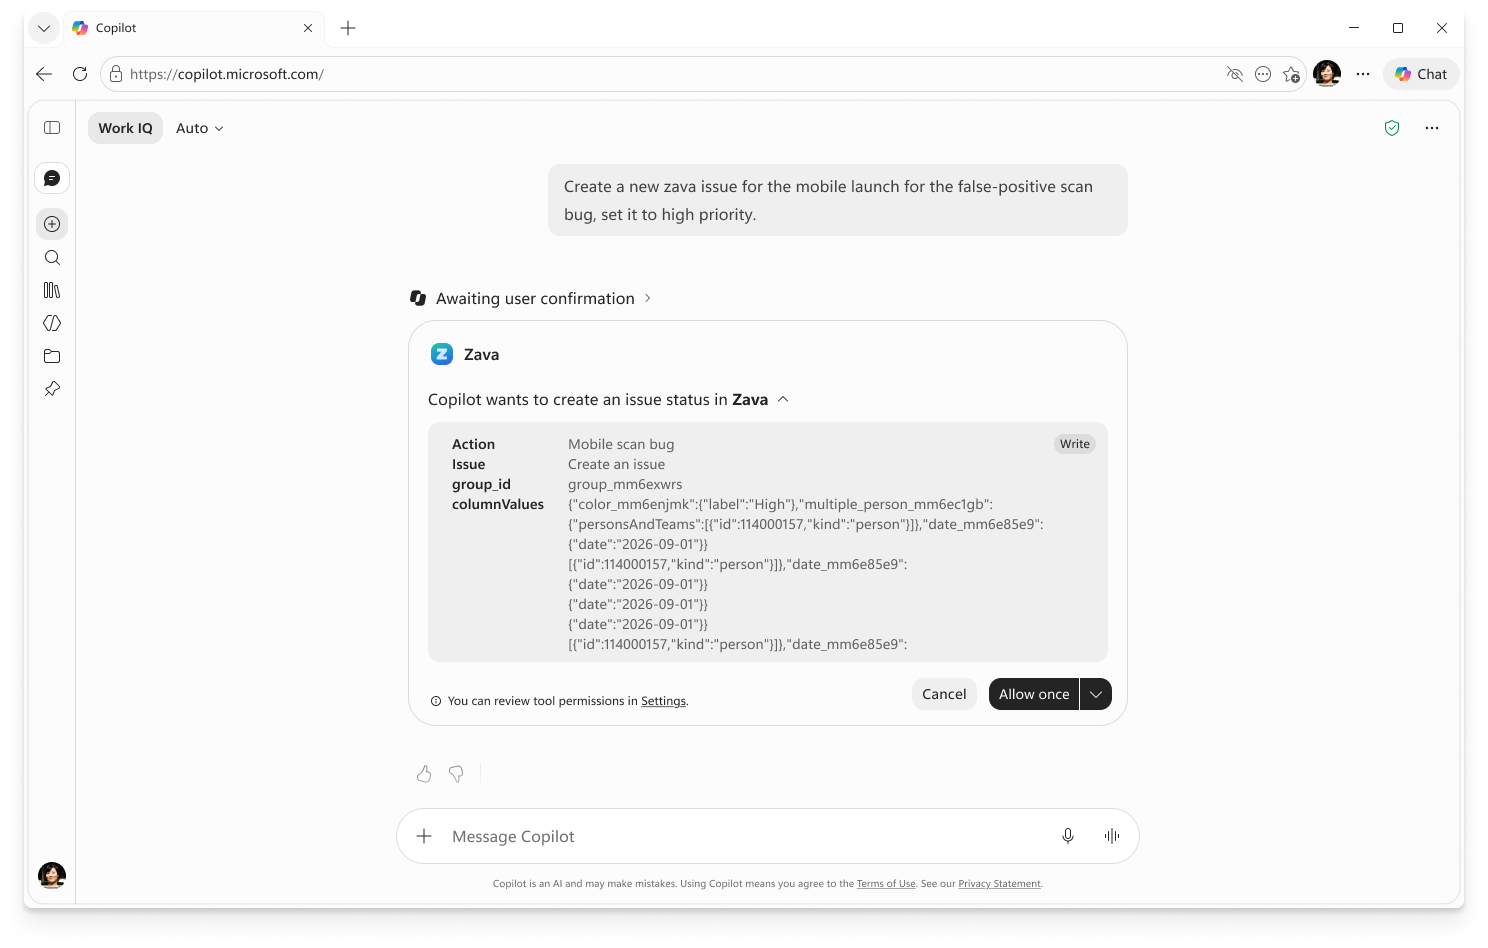
The following image shows a collapsed confirmation card for a write action.
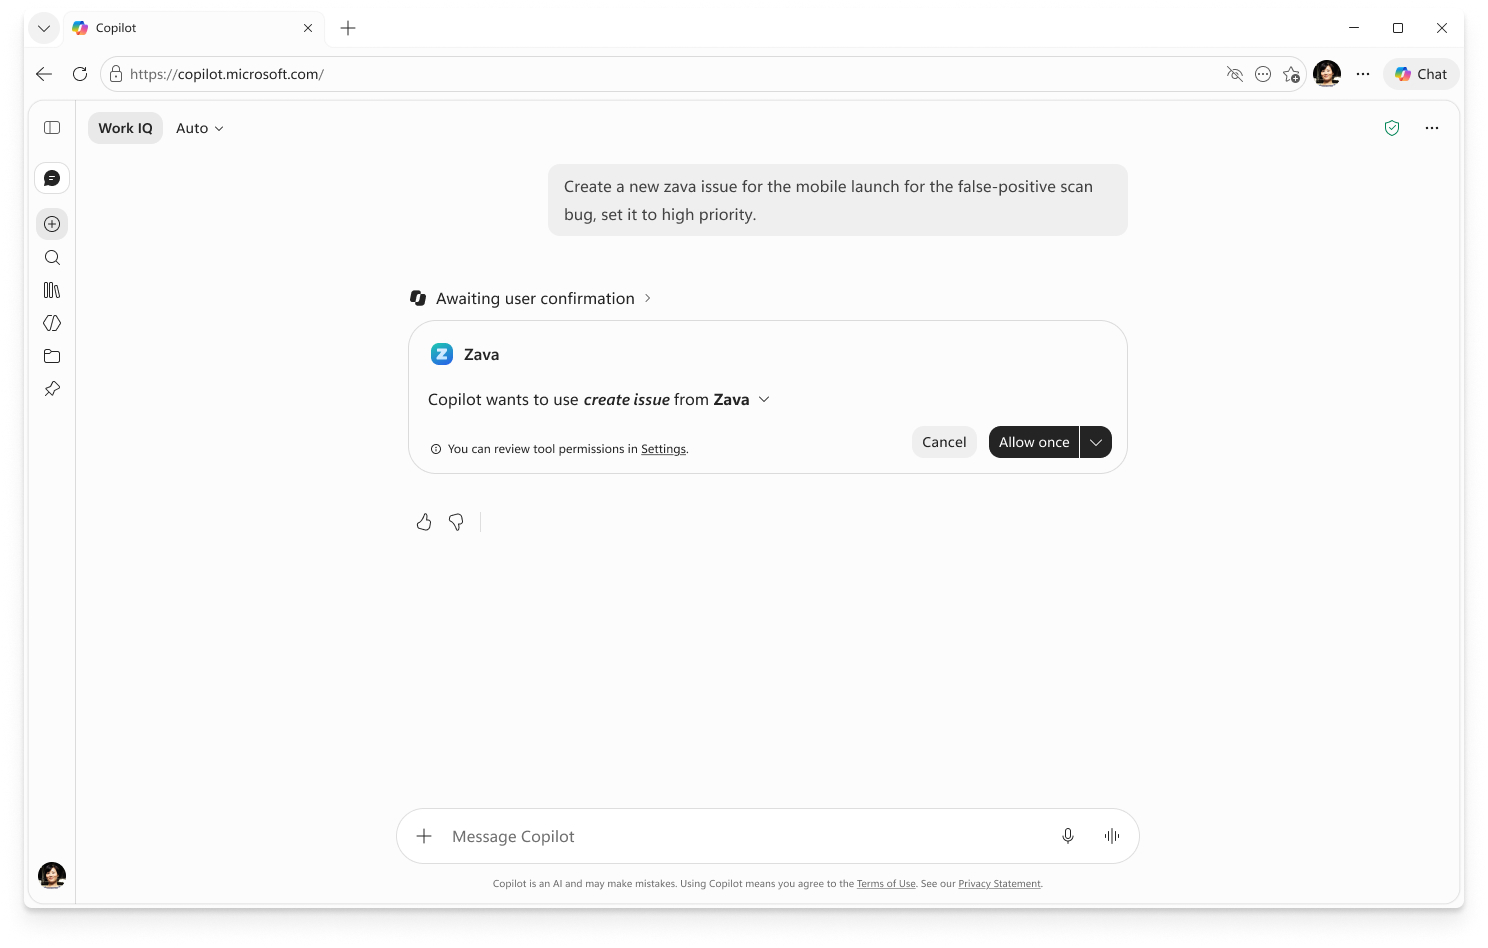
Users can expand the card to review the action parameters before approving it.
Open the menu next to Allow once to choose Allow for conversation or Always allow.
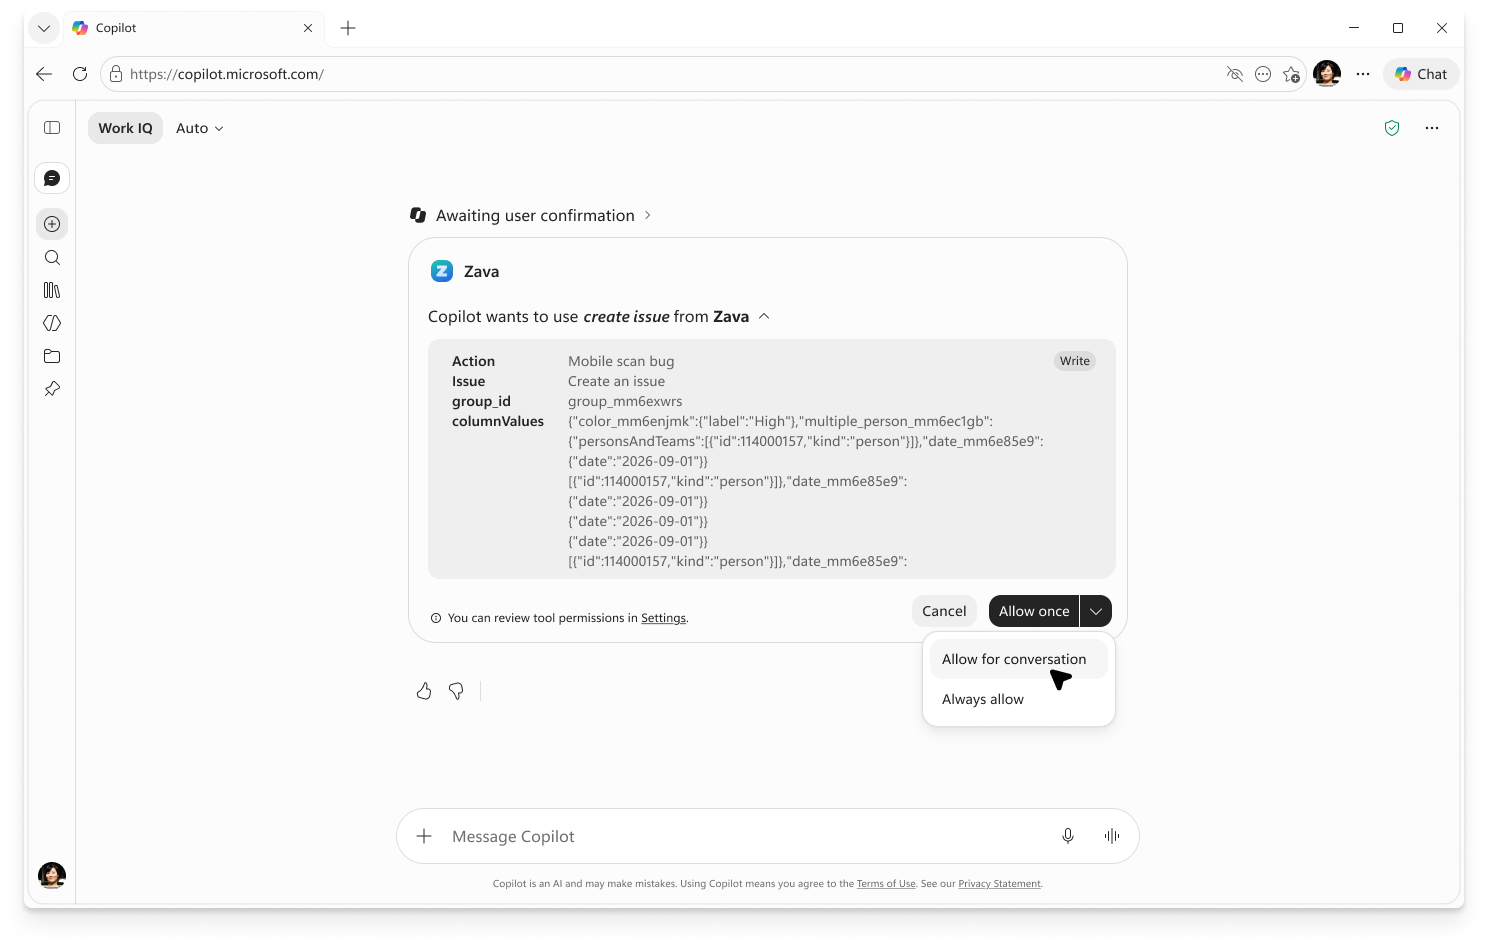
The user chooses one of the following options:
| Option | What happens |
|---|---|
| Allow once | Runs the action now. Copilot asks again the next time it wants to use the tool. |
| Allow for conversation | Runs the action and doesn't ask again for this tool for the rest of the current conversation. |
| Always allow | Runs the action and doesn't ask again for this tool until the user changes the setting or the publisher changes the tool. |
| Cancel | Declines the action. Nothing is changed in the connected system. |
Always allow and Allow for conversation apply to the individual tool, not to the whole connector. Users can decide which tools to allow.
Manage tool permissions for write, update, and delete
Users can review or reset tool permissions in Copilot by going to Settings > Sources and selecting the connector. The Tools section groups the connector's Write/Delete tools separately from its Read tools.
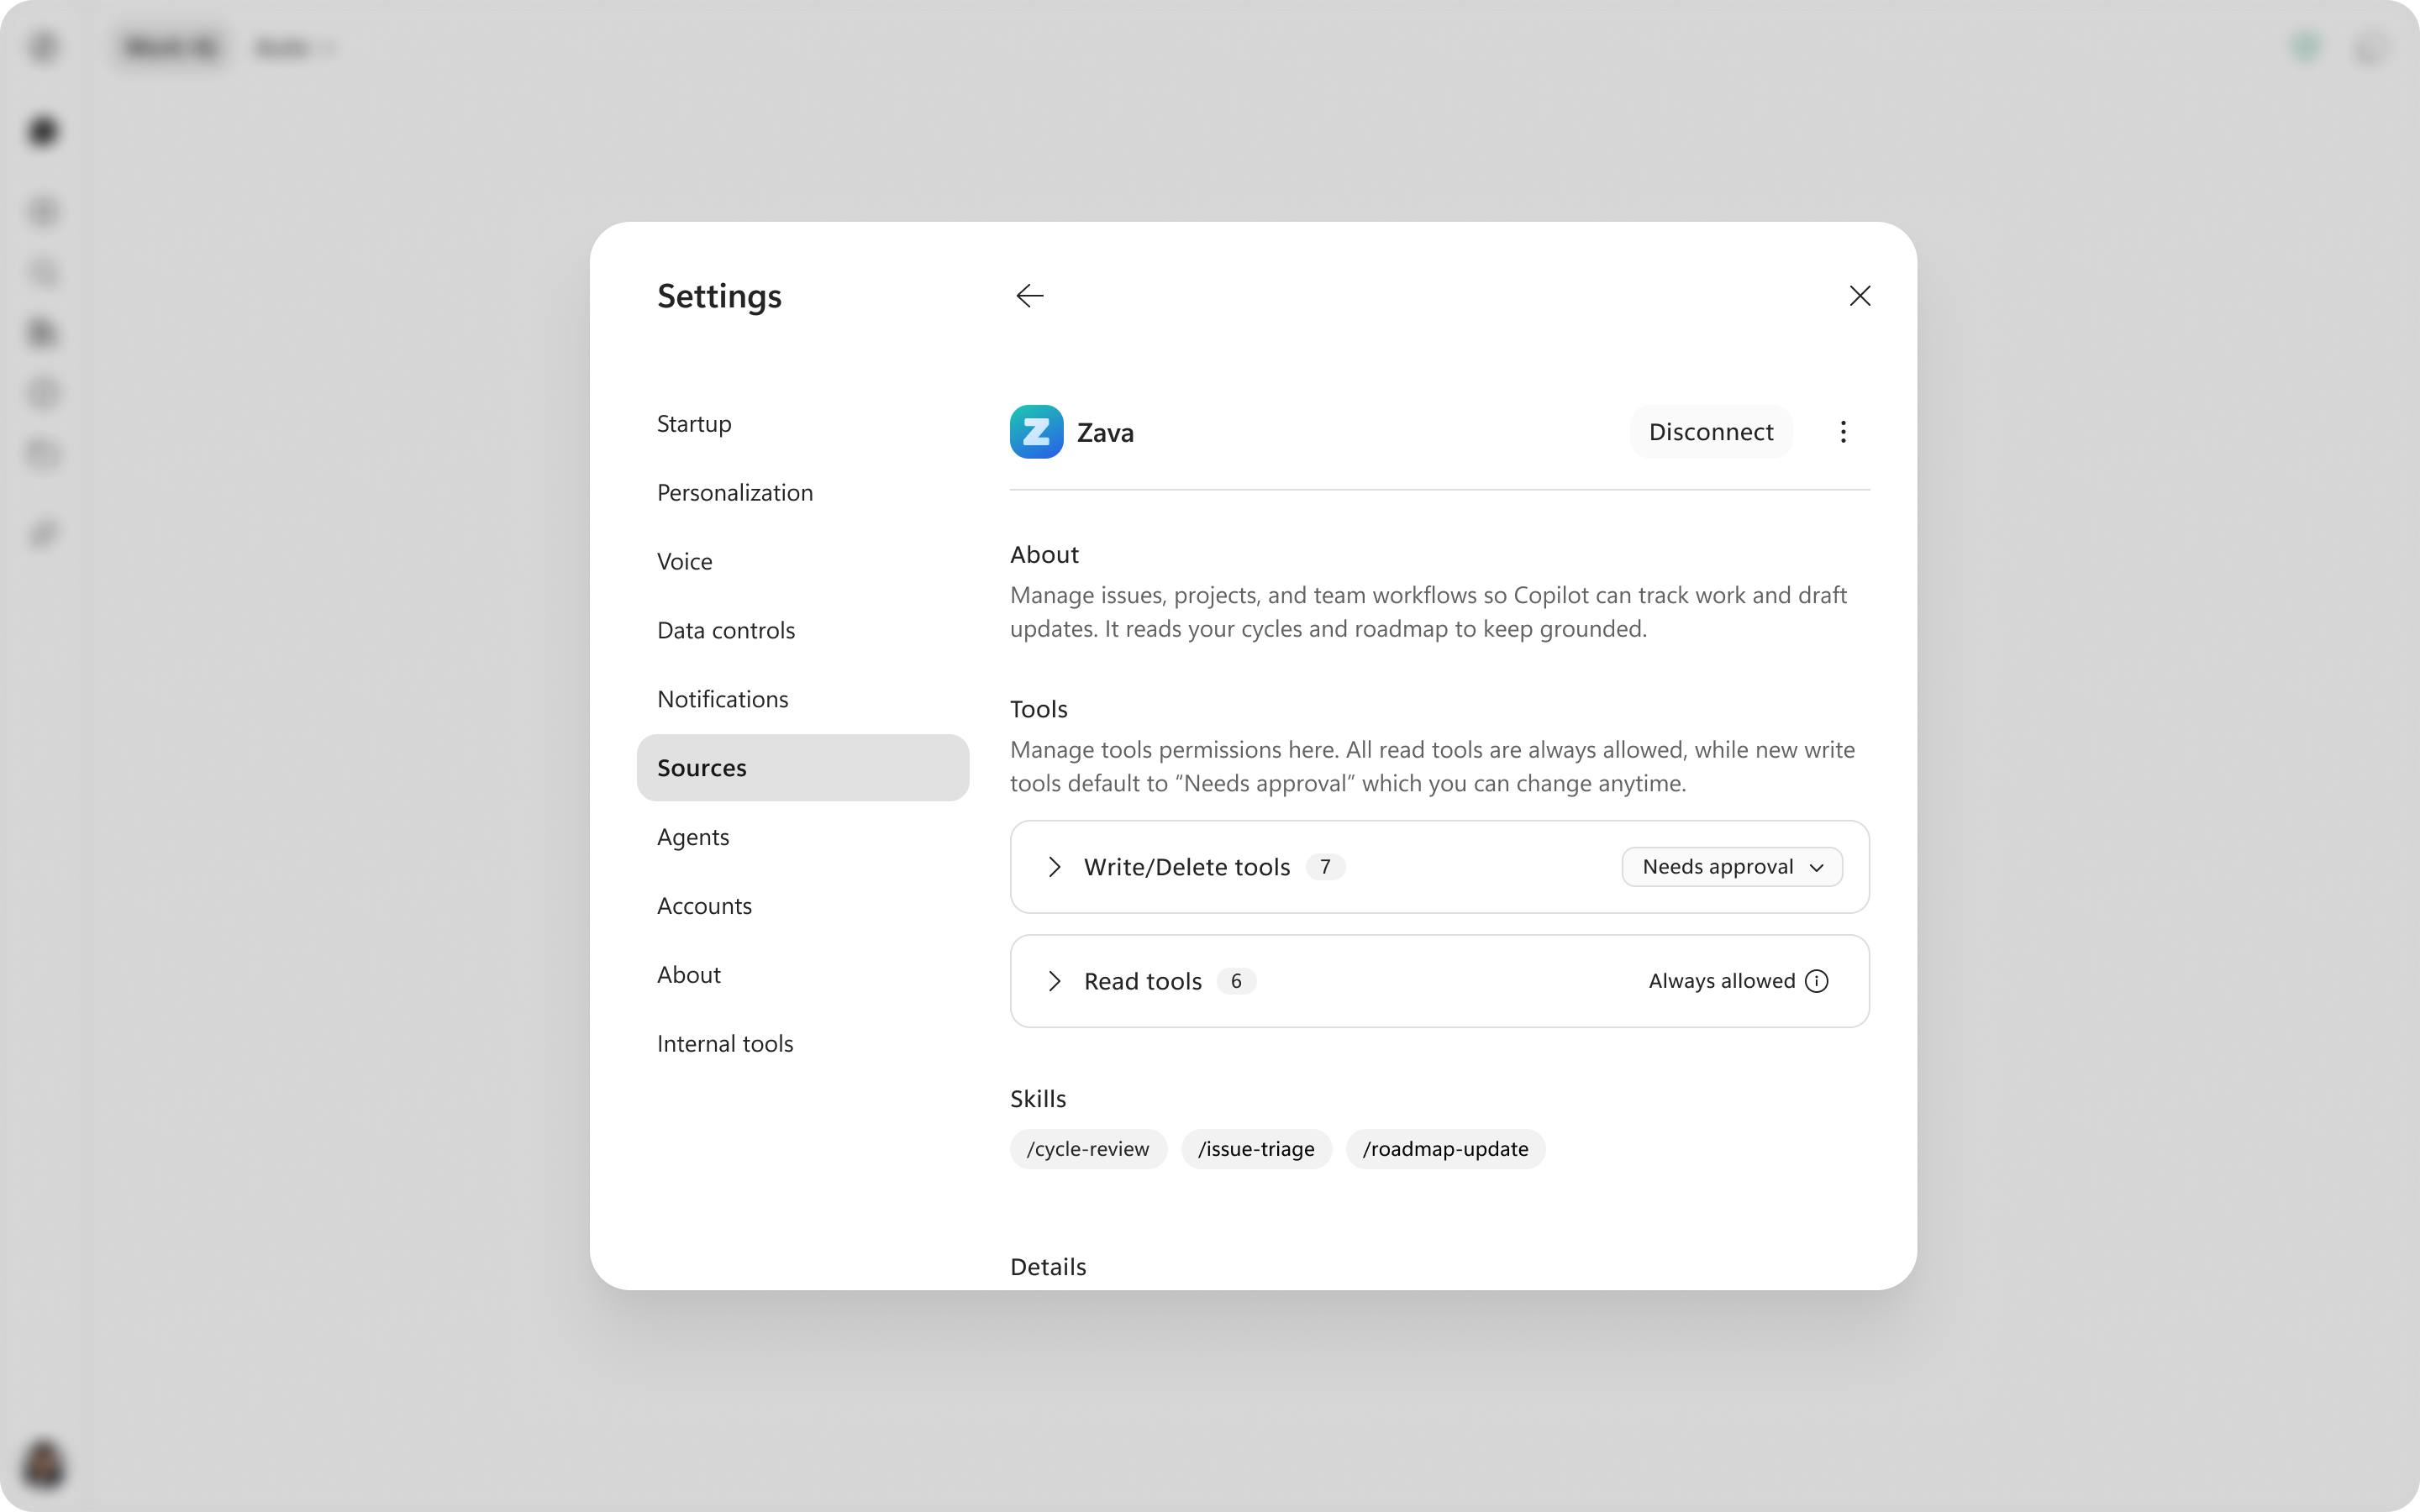
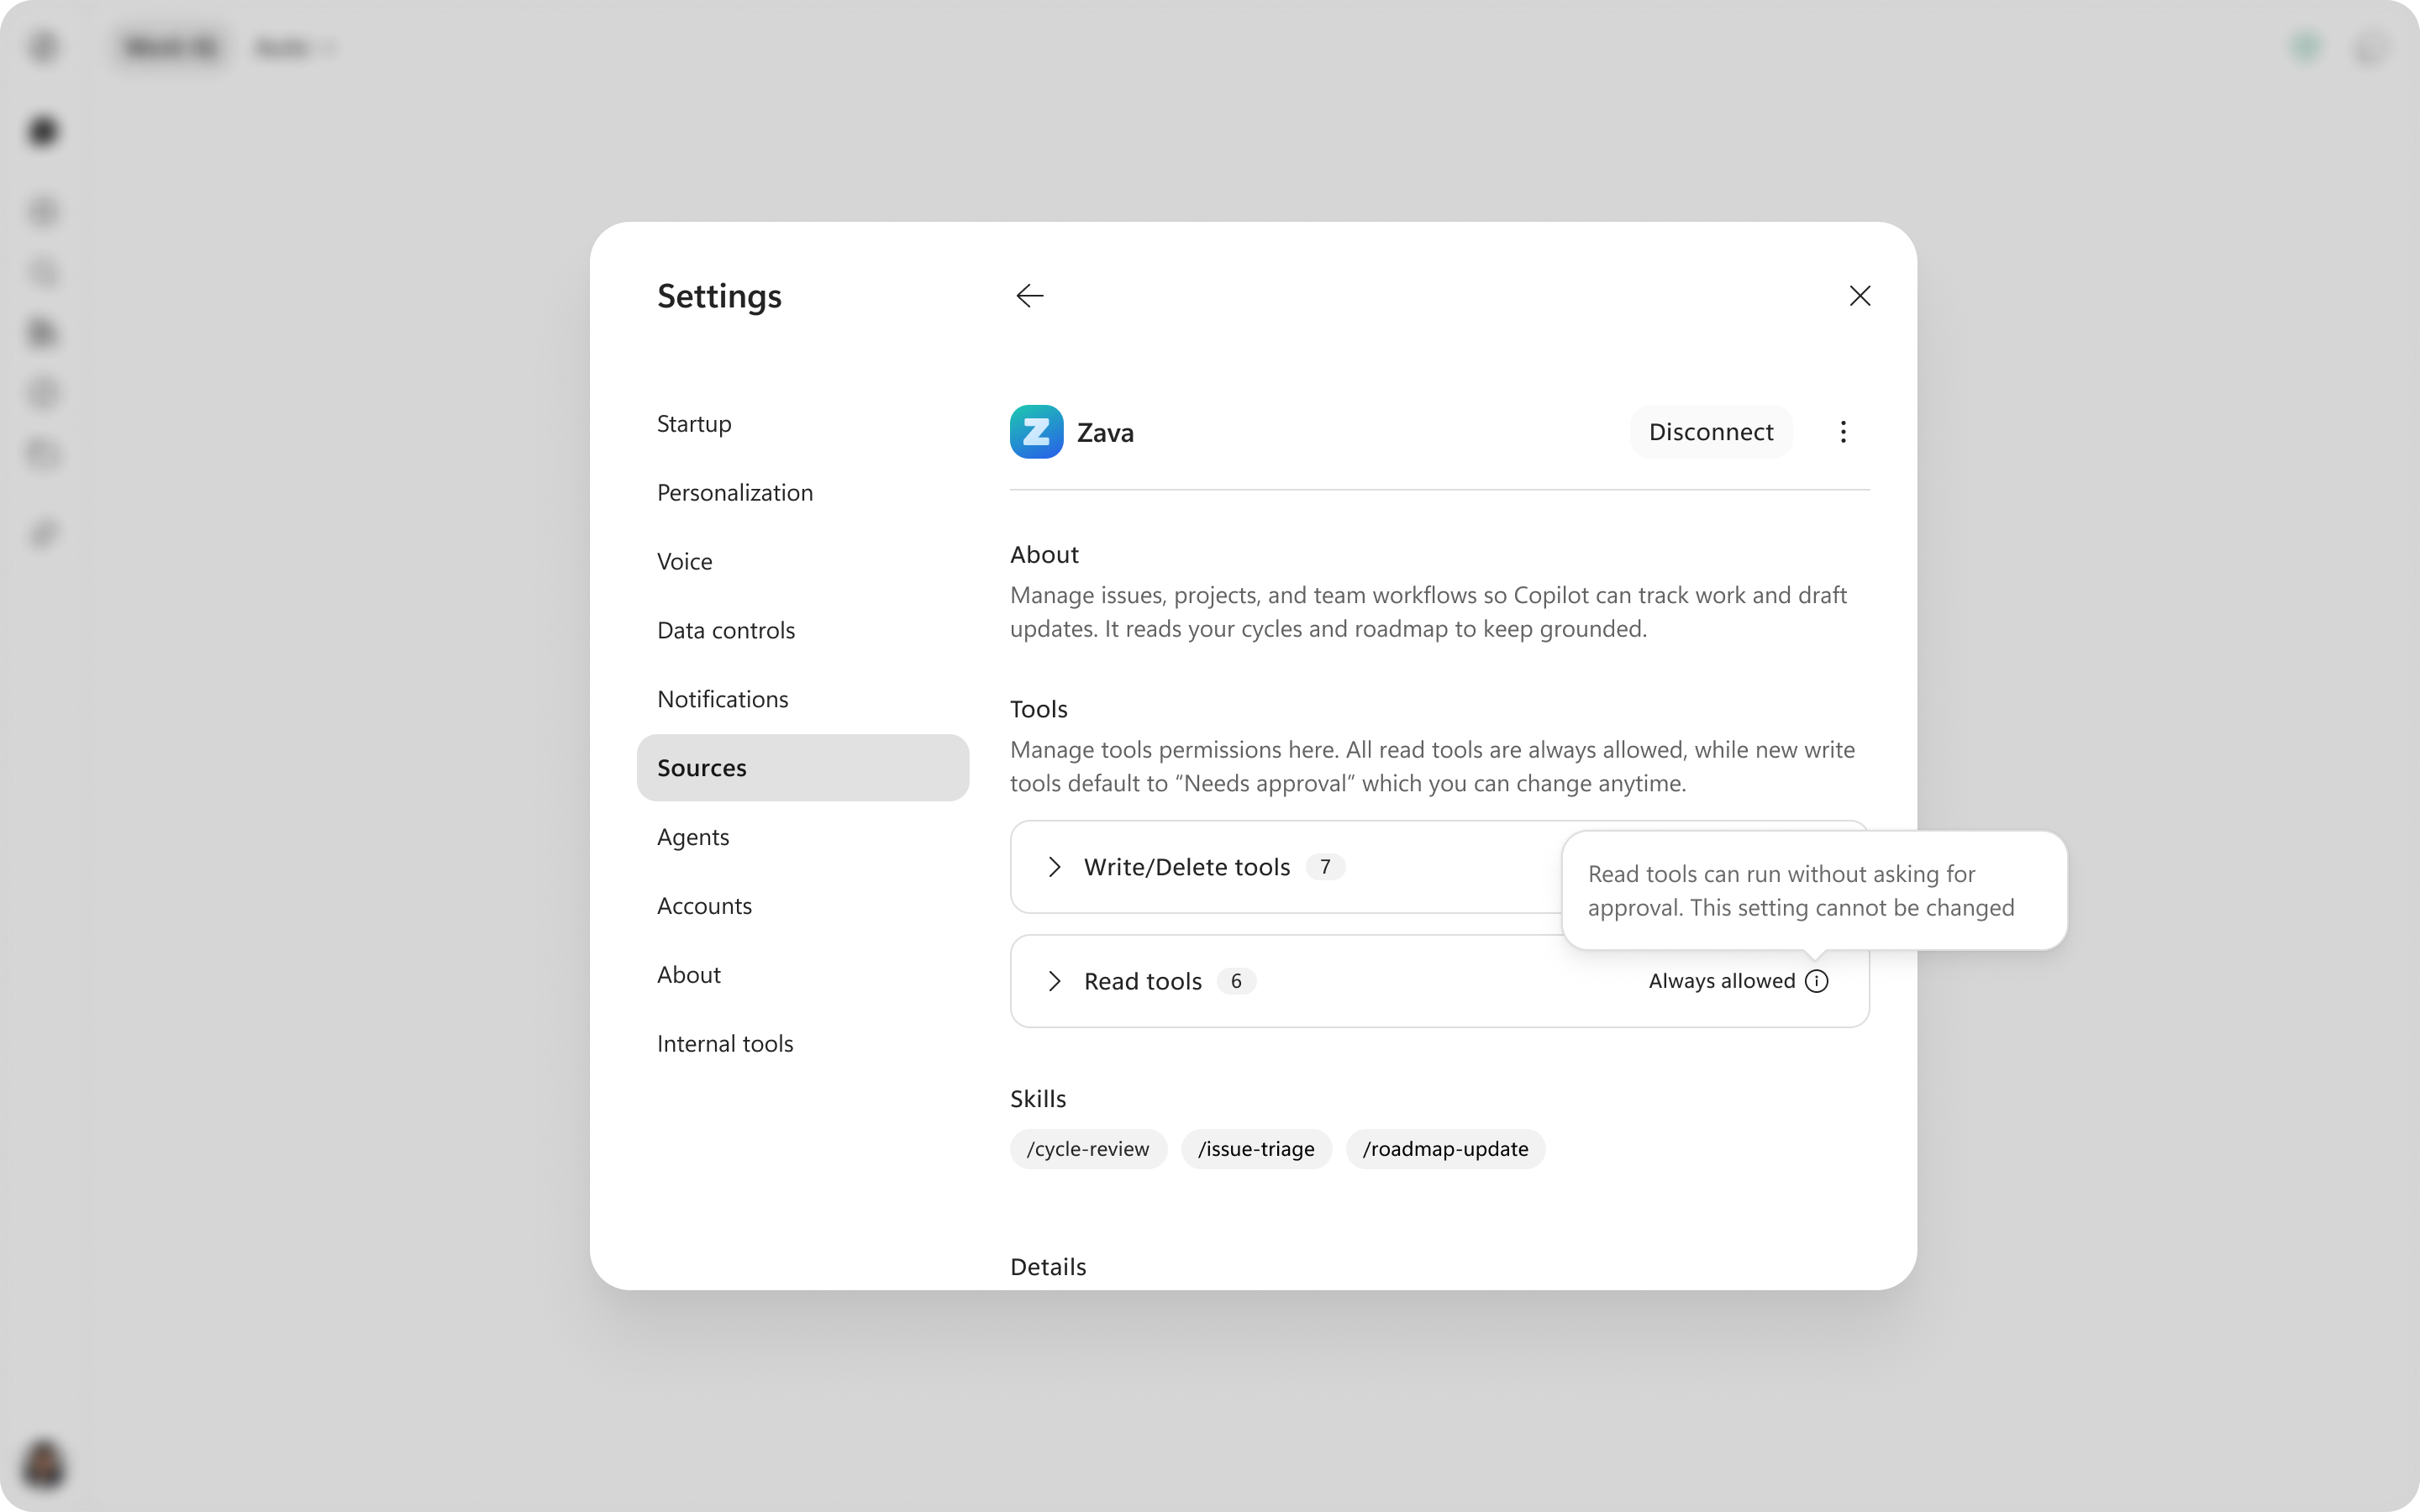
Read tools are always allowed and don't require approval.
Write, update, and delete tools default to Needs approval, which means Copilot asks for confirmation each time. A user who selected Always allow can switch back to Needs approval for the entire Write/Delete tools group.
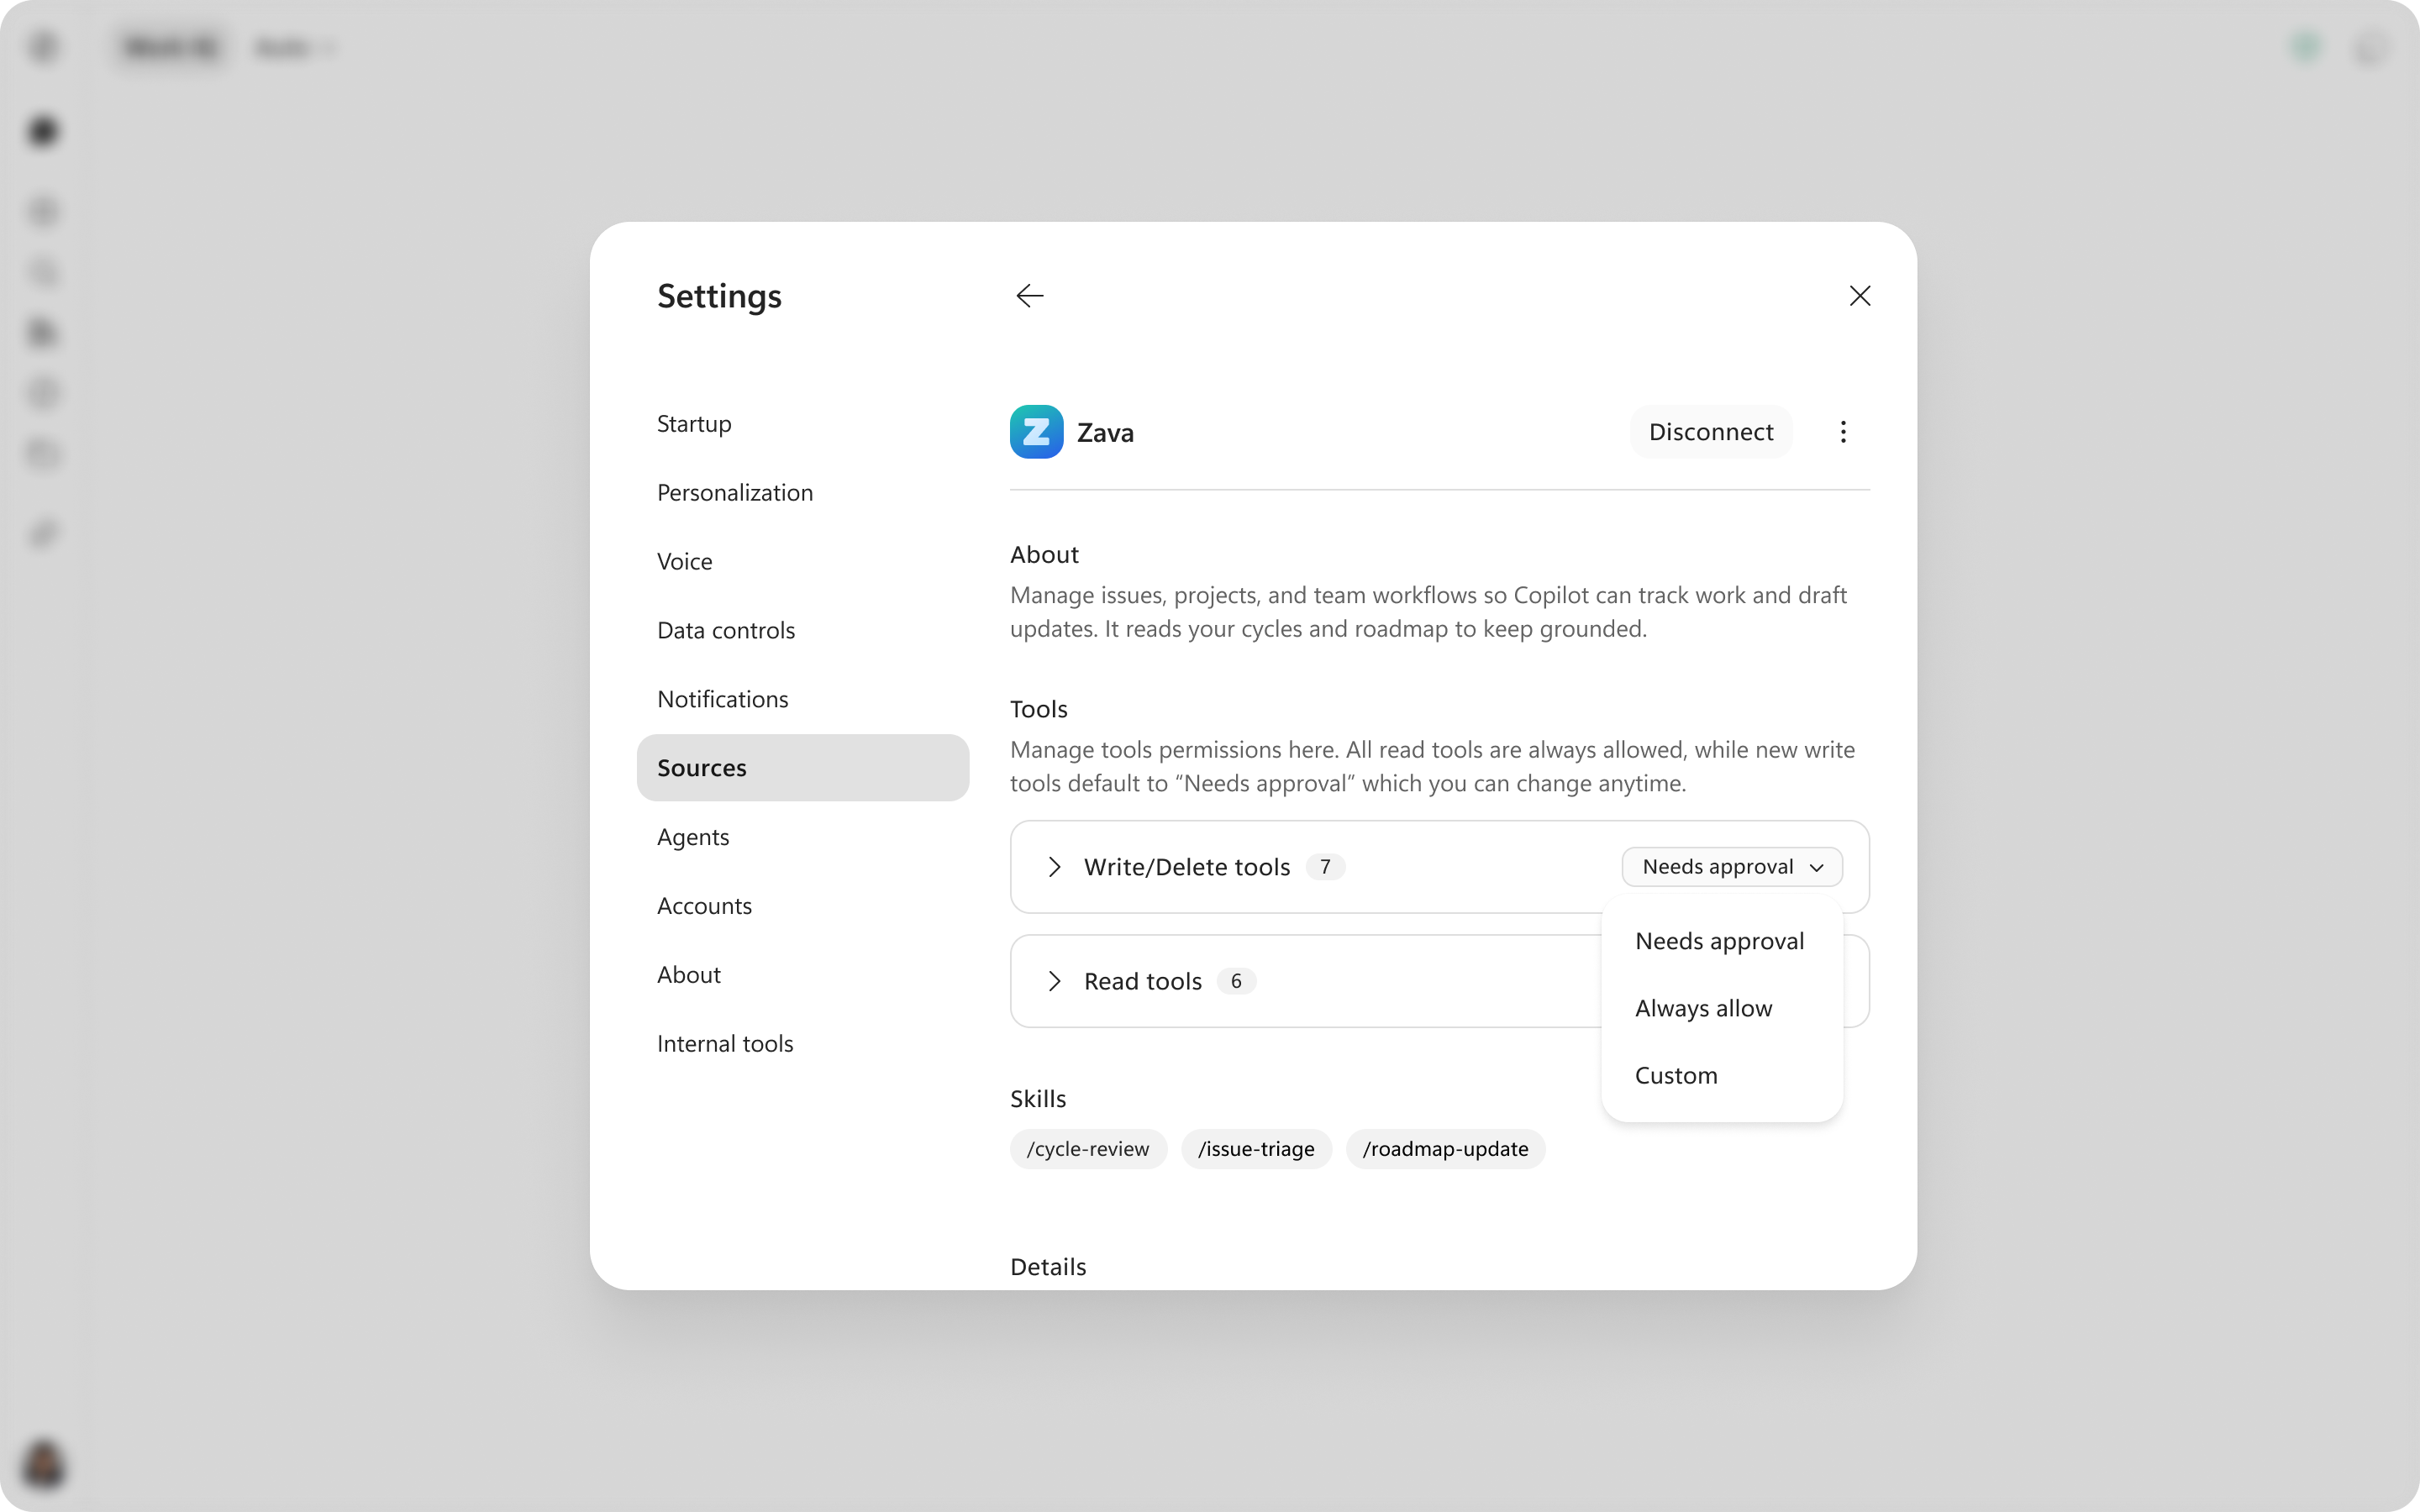
Review individual tool permissions
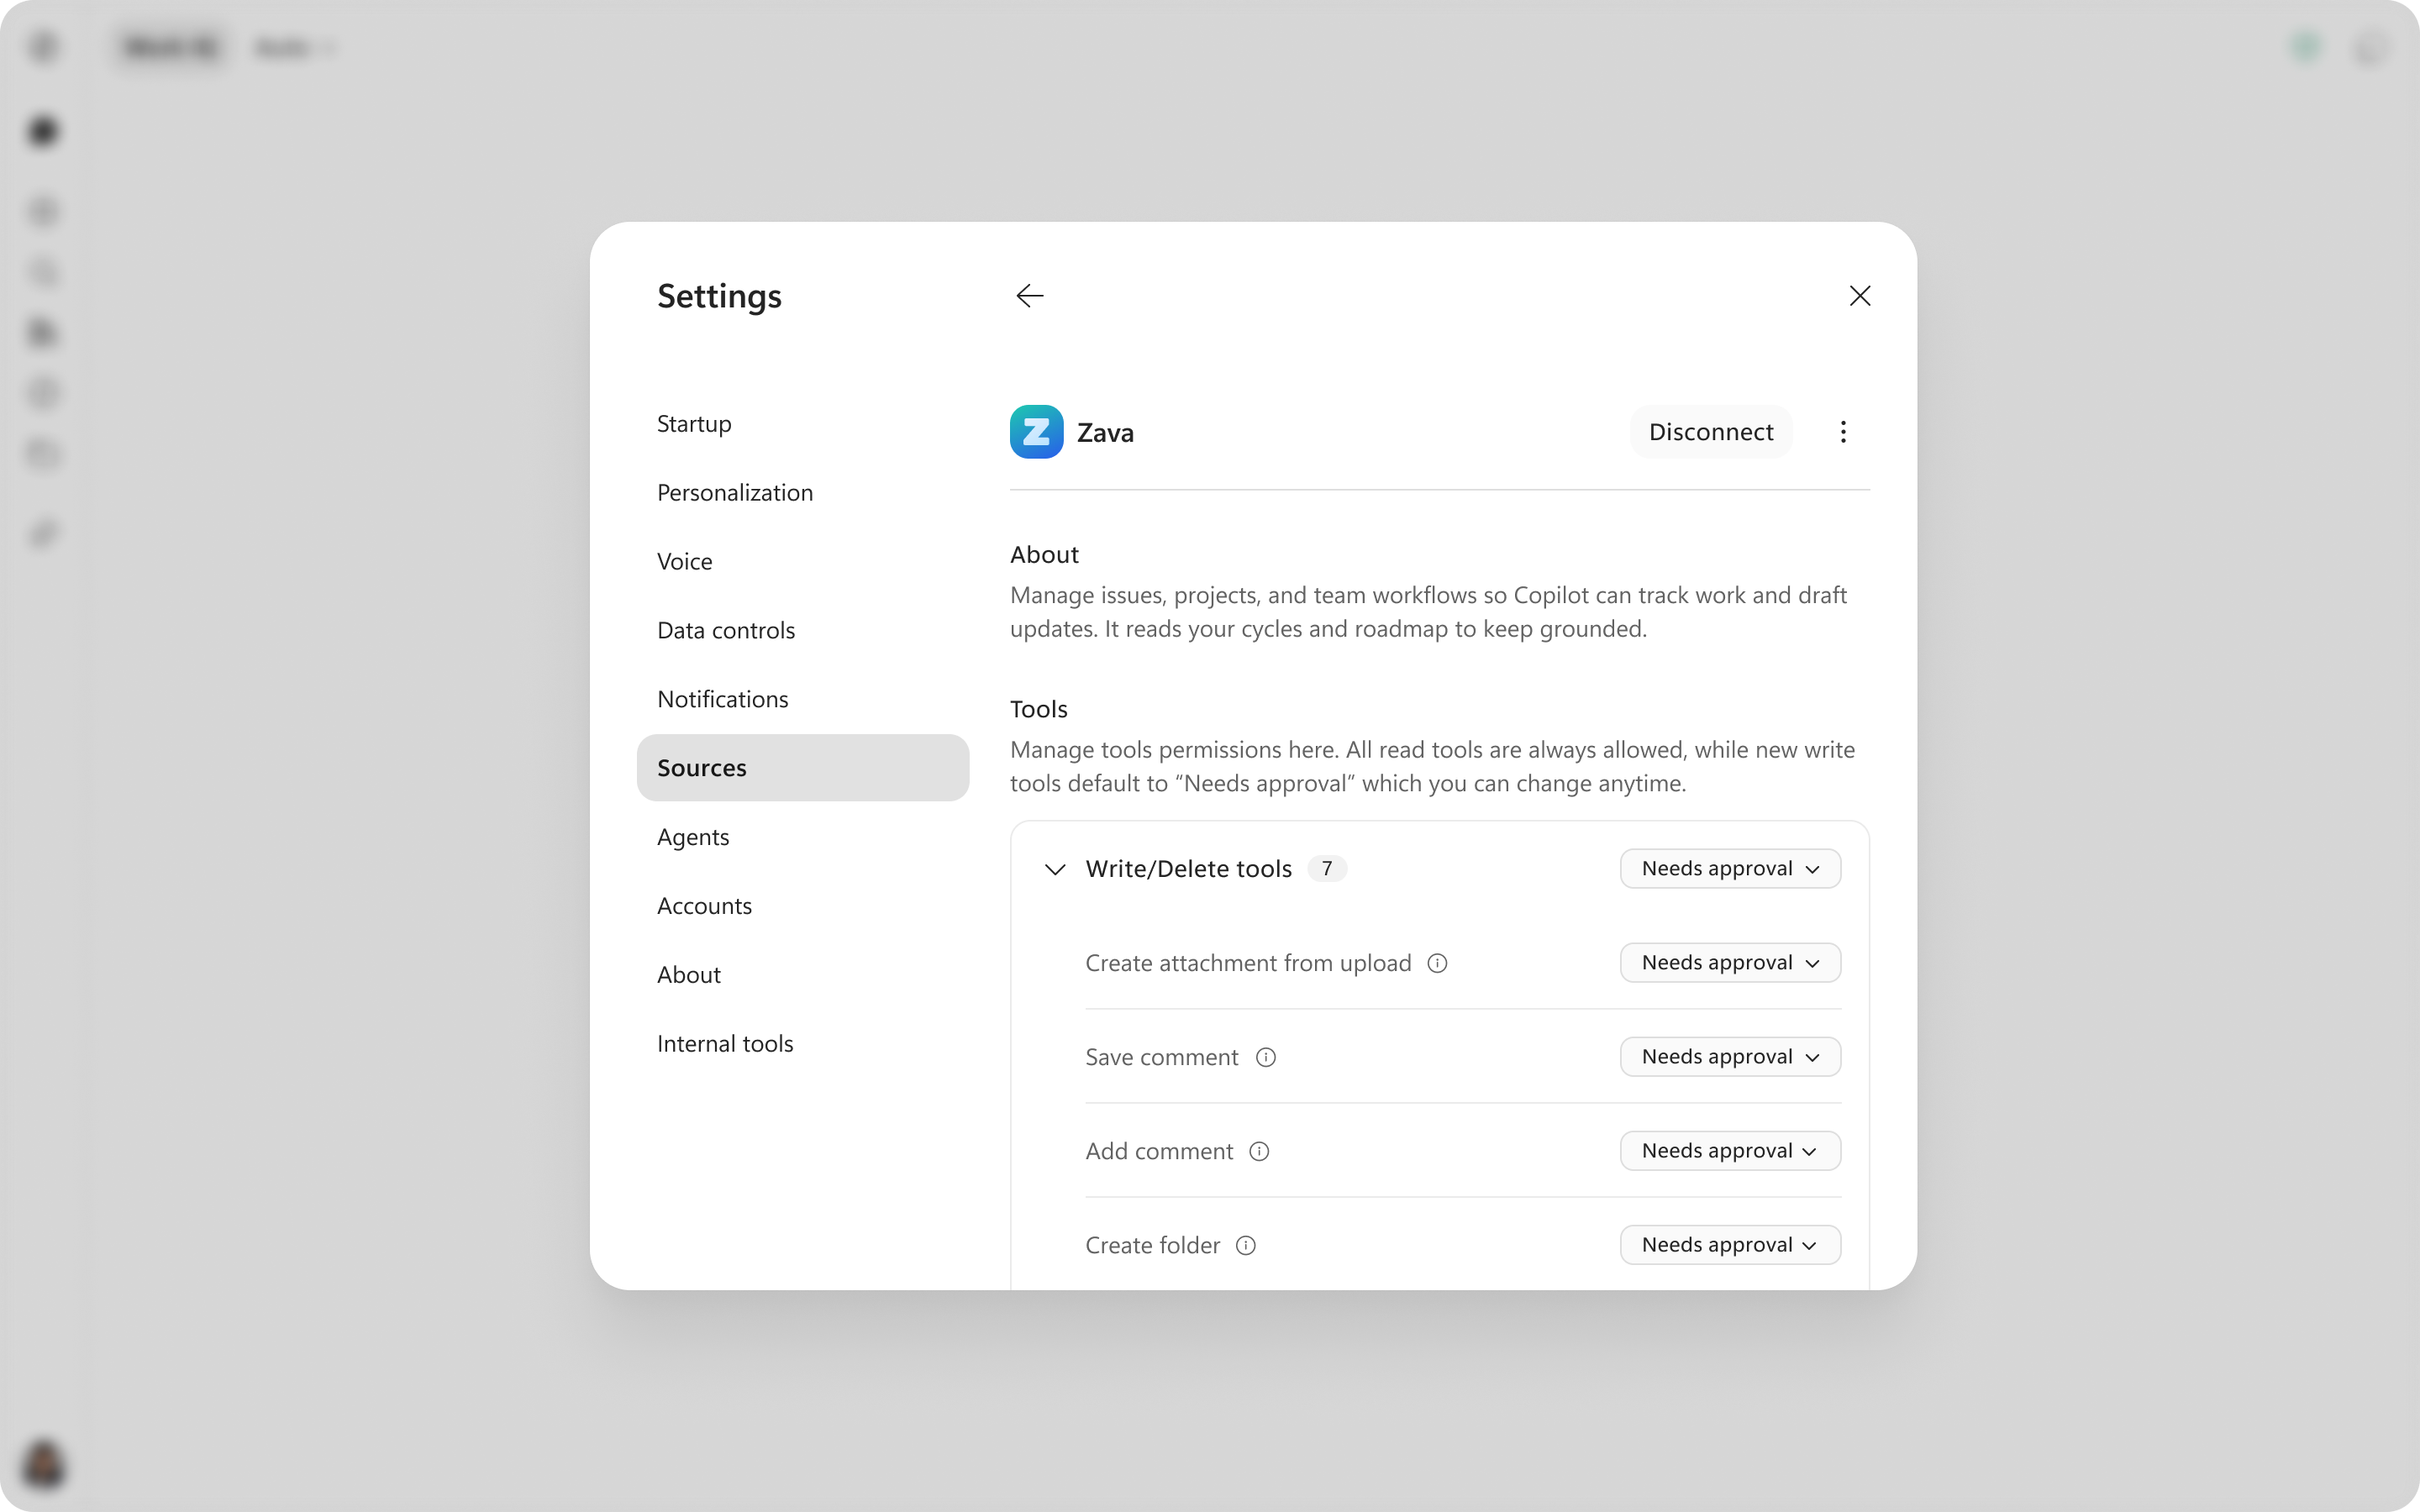
Expand Write/Delete tools to review individual tools and their approval settings.
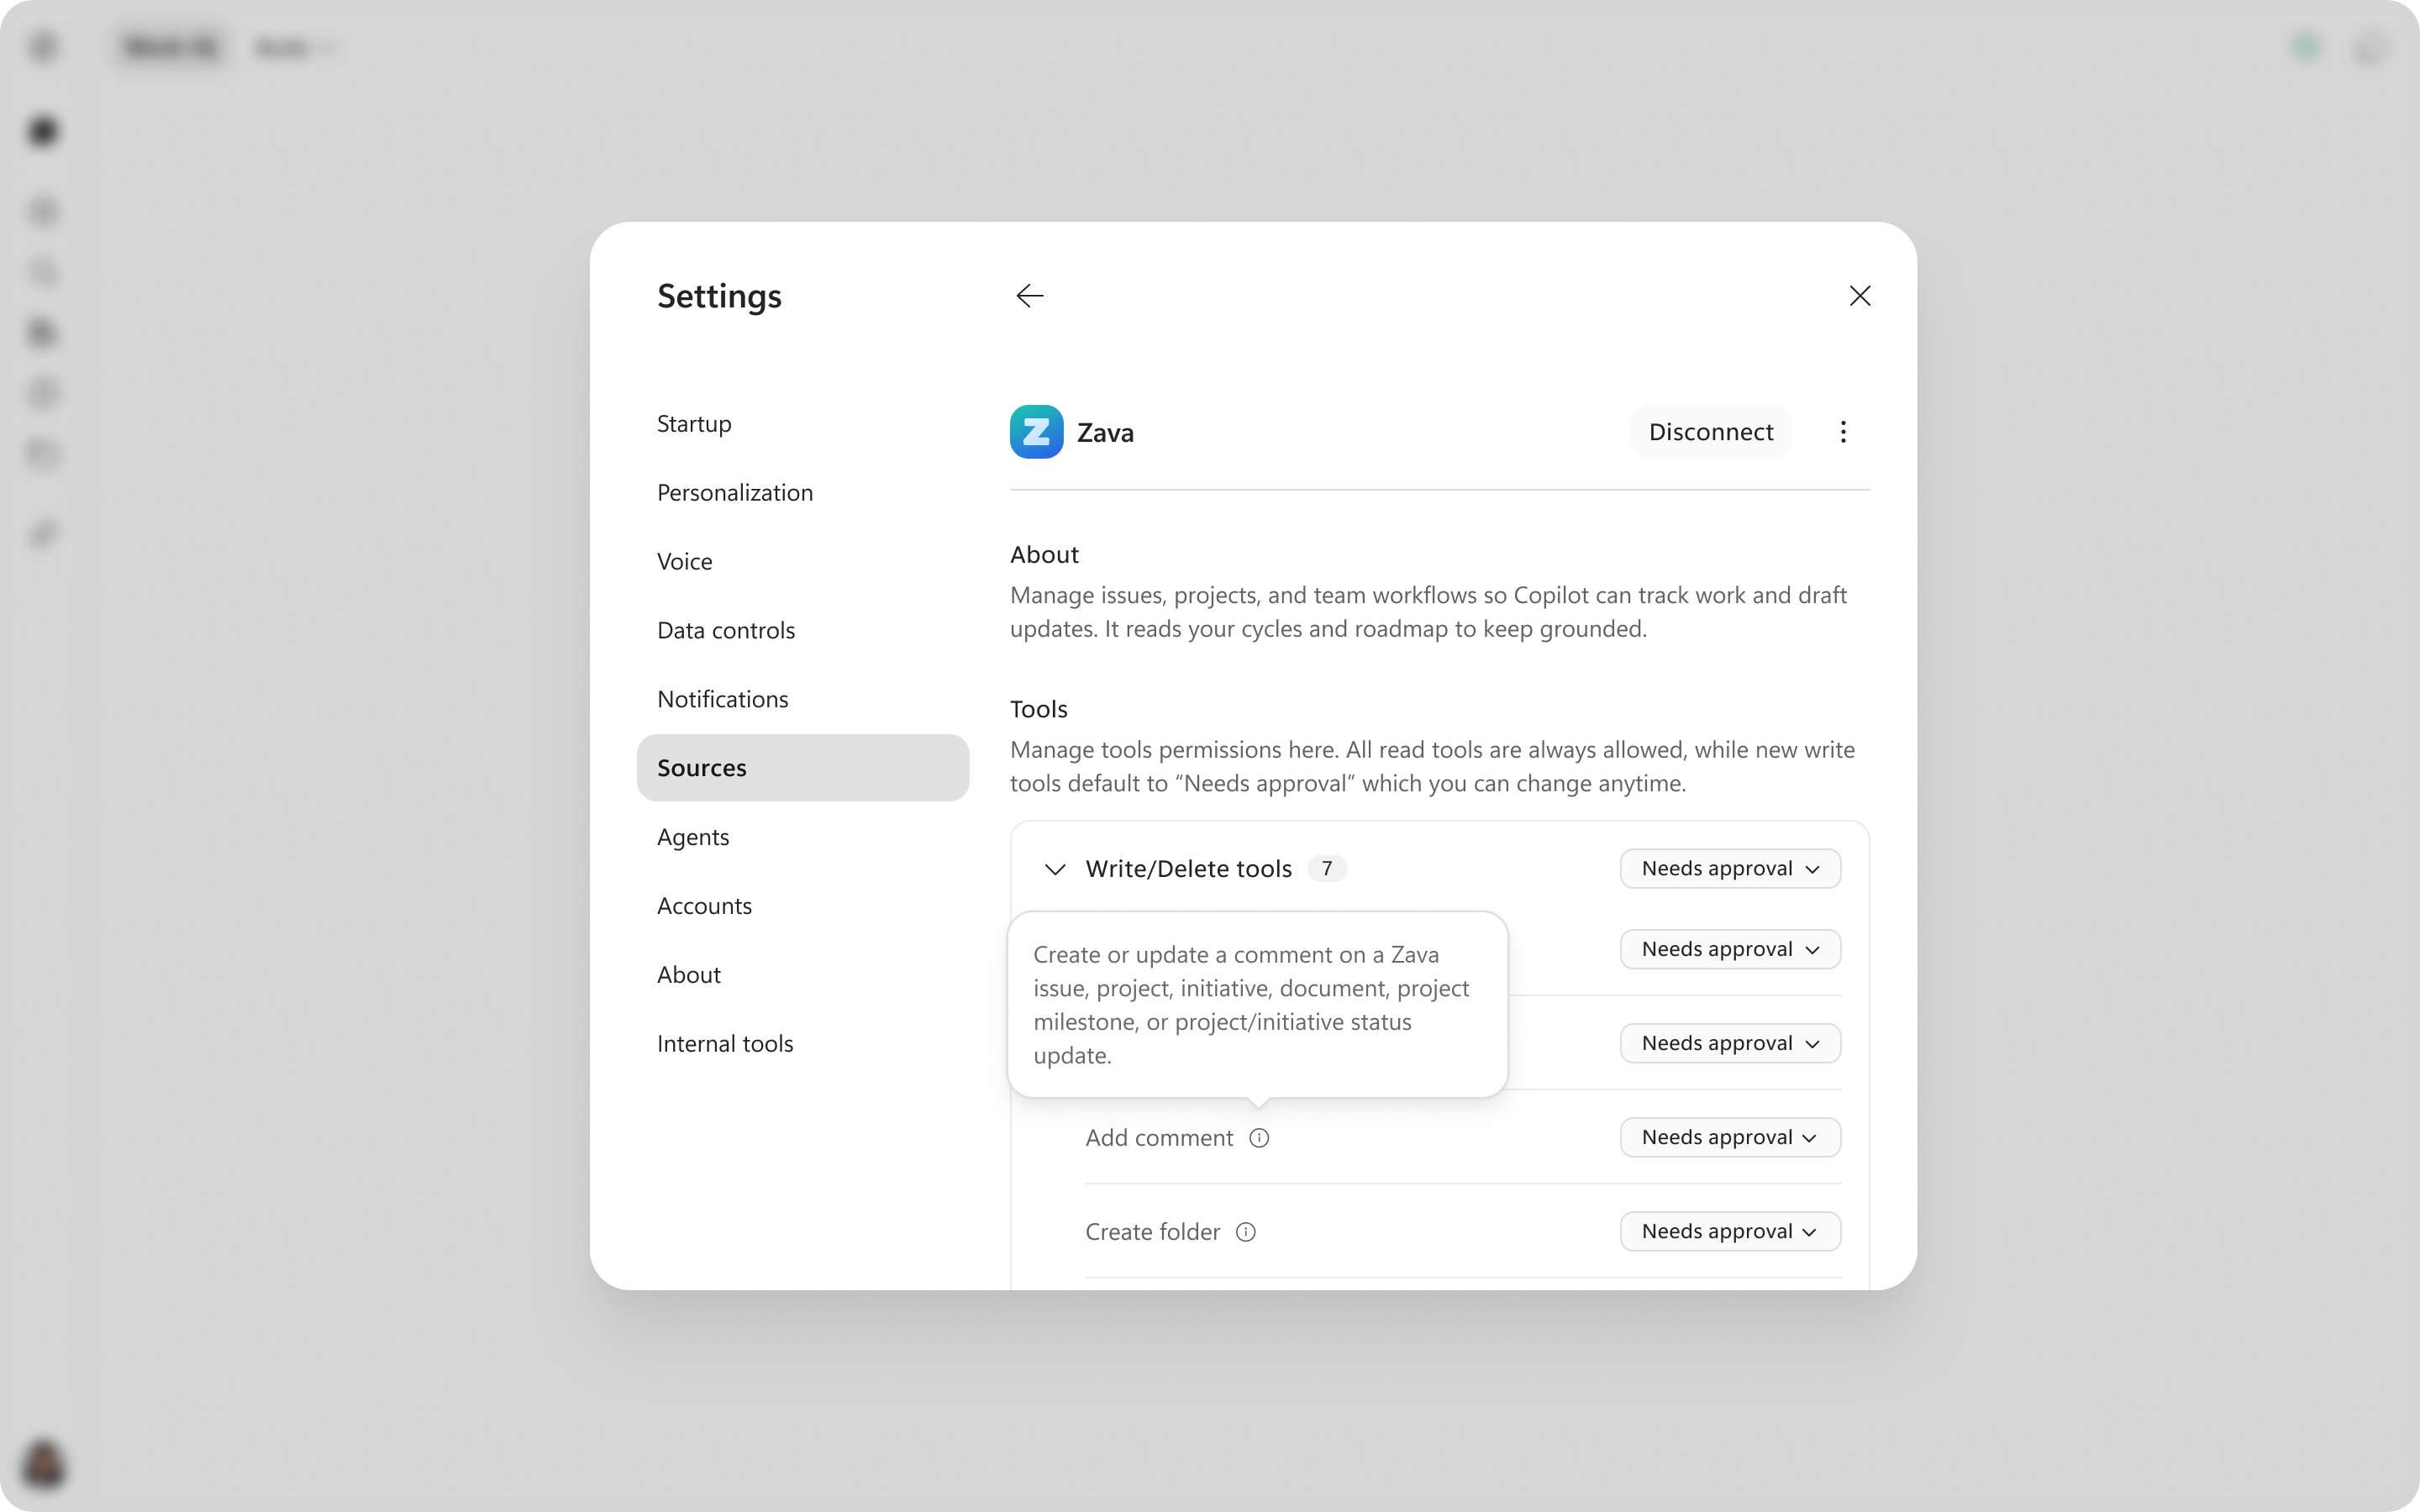
The following image shows a tool description in the expanded list.
Users can also change approval settings for an individual tool.
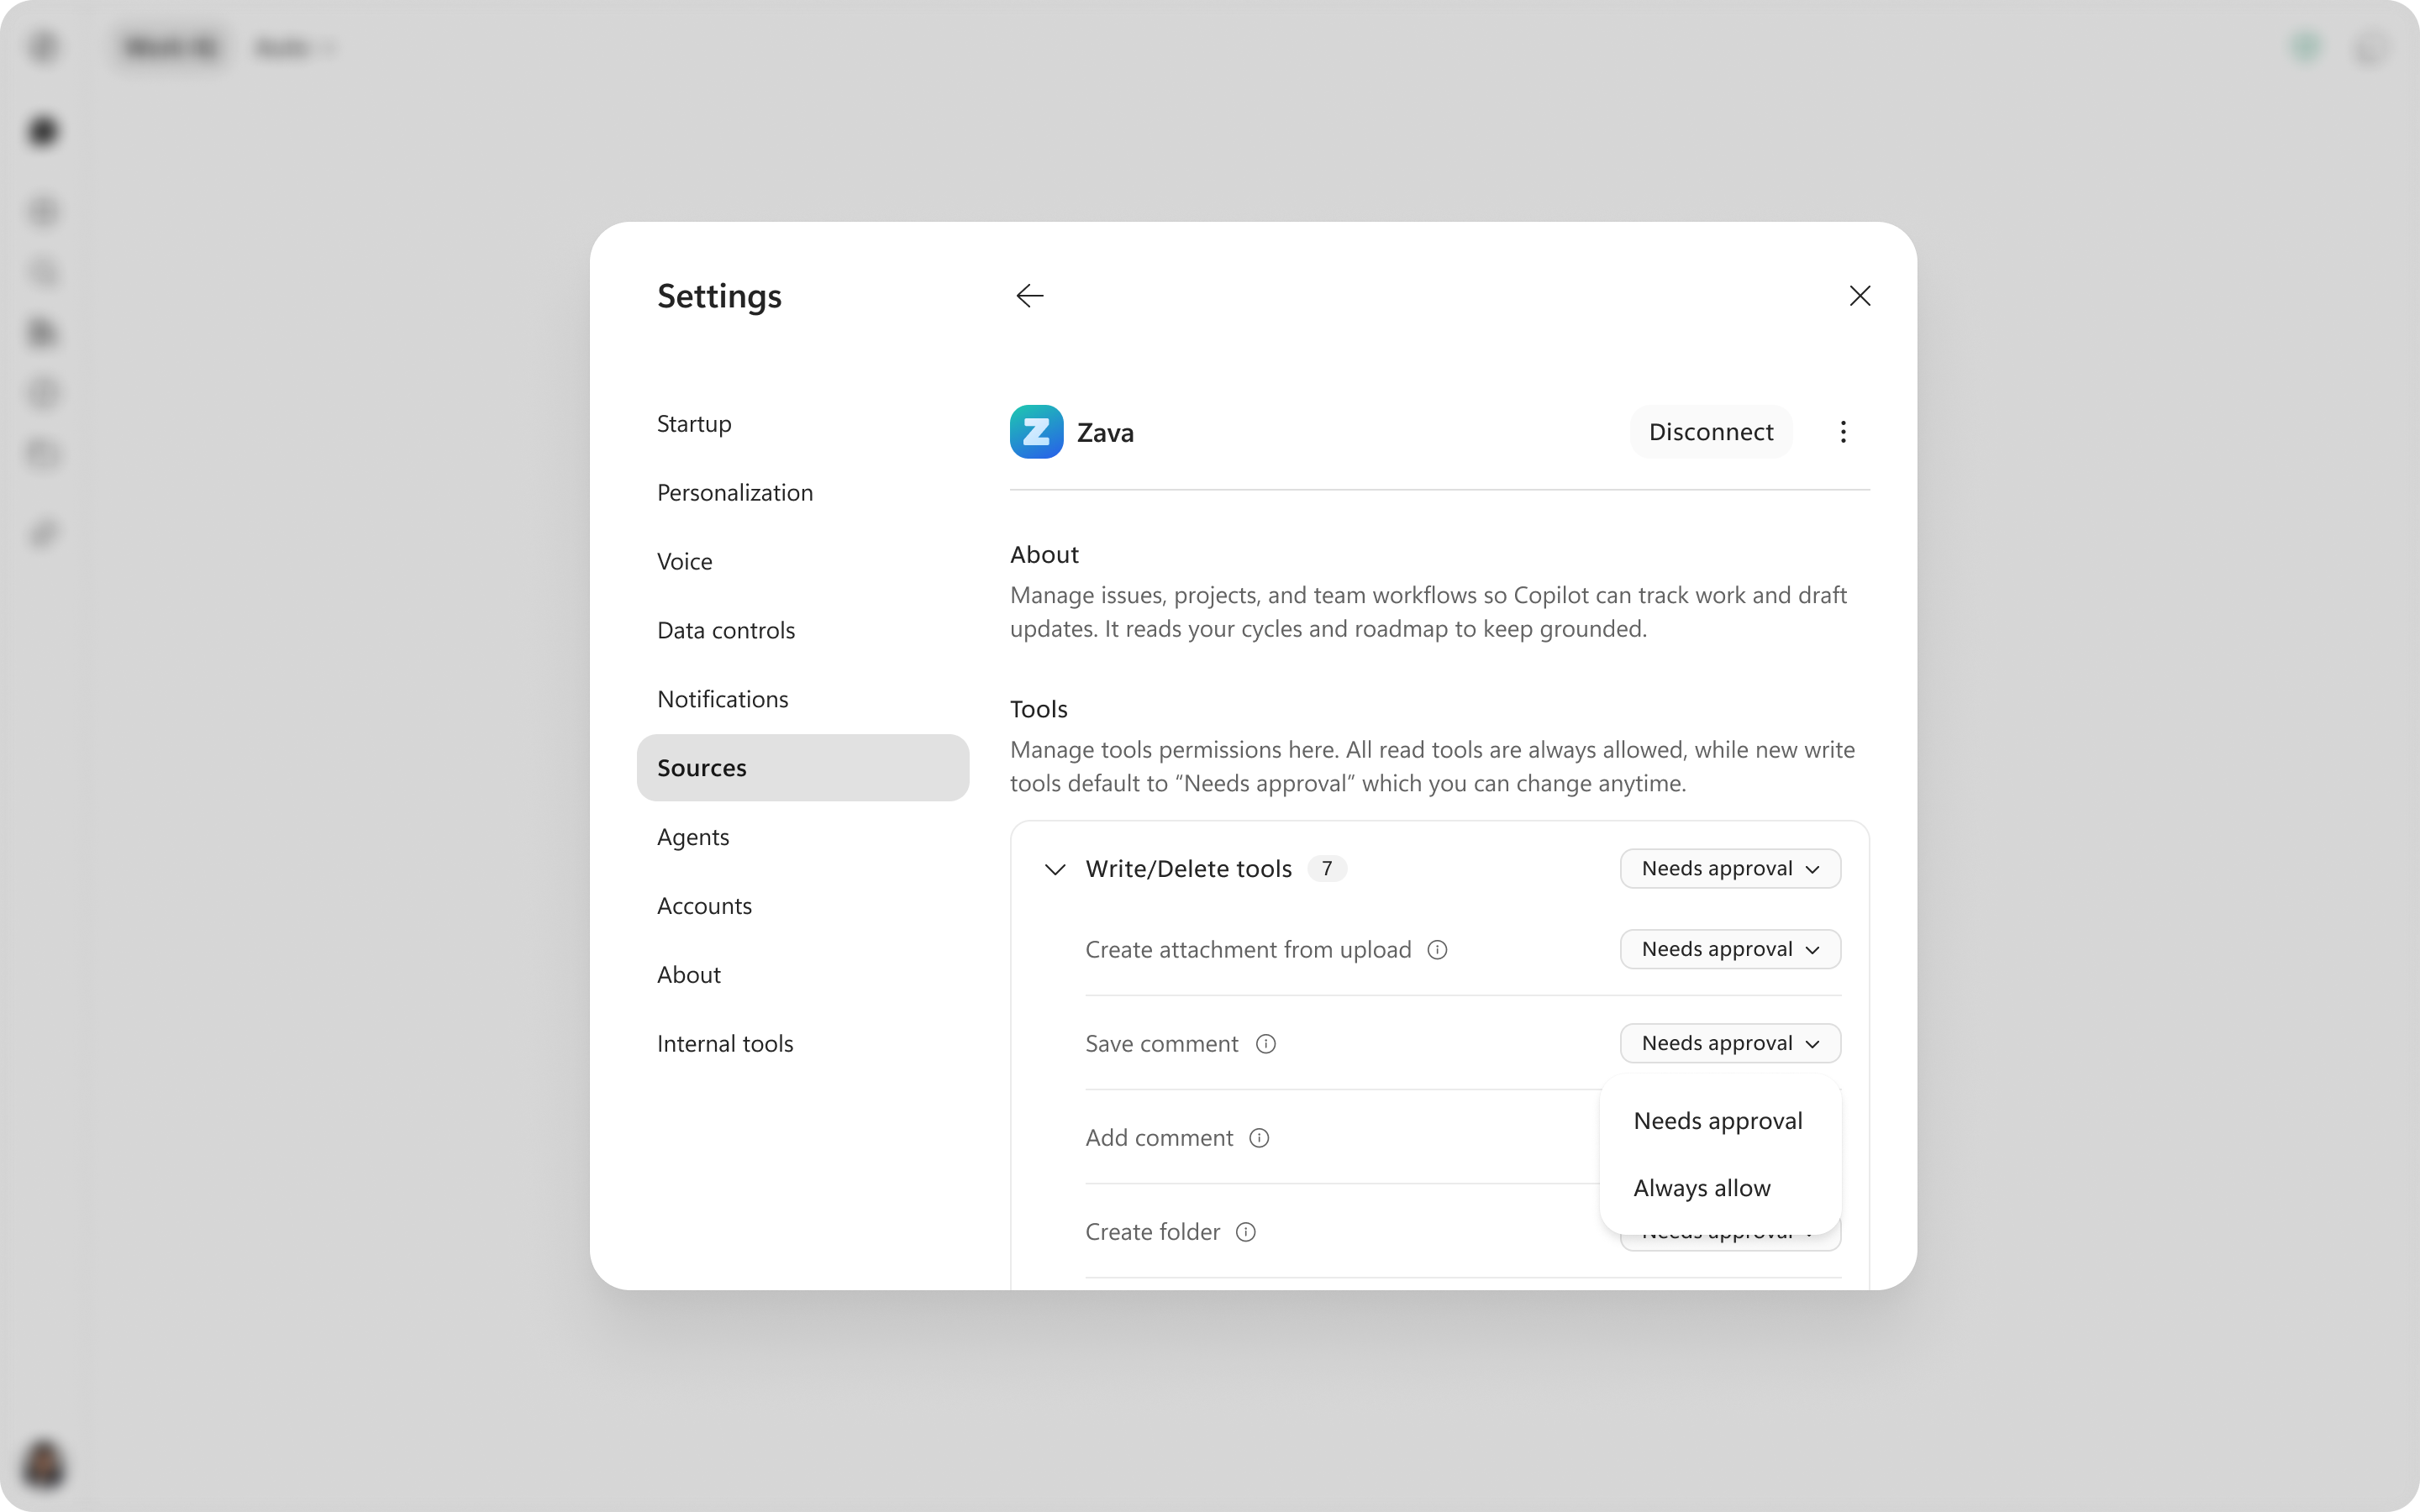
If a connector publisher adds a new write-capable tool or changes an existing one, the tool is set to Needs approval by default. Thus, Copilot will ask for confirmation the next time it wants to use that tool.
Security and compliance
The following security and compliance features apply to federated connectors:
- Federated connectors don't copy or store data in Microsoft 365.
- The source system enforces all permissions. Users can only access content they're authorized to view and make changes they're authorized to make in the original data source.
- OAuth 2.0 and encrypted communication ensure secure access and authentication.
FAQs
How are federated Copilot connectors different from synced Copilot connectors?
Synced Copilot connectors index data into Microsoft Graph. Federated Copilot connectors fetch content live; no indexing takes place.
Synced connectors are supported at an organization level; federated connectors are federated at the user level. User credentials, rather than admin credentials, are required to connect to any data source.
Can I use both federated and synced connectors in my tenant?
Both federated and synced connectors can coexist in your tenant and appear together in your connector list.
Does the Allowed plugins type setting apply to federated connectors released in the future?
Yes. The setting applies to connectors released after you configure it. If you deselect the Microsoft-published and third-party-published options, users can't access new connectors until an admin enables them. If you select those options, new connectors follow the default rollout behavior.
How do ISVs publish connectors?
ISVs use a single connector manifest and single publishing pipeline for all connector types.