Note
Access to this page requires authorization. You can try signing in or changing directories.
Access to this page requires authorization. You can try changing directories.
Features
- Secret asset metadata generally available via API
- Code scanning now supports Rust
- Expanded CodeQL buildless scanning for C/C++
Secret asset metadata generally available via API
This feature adds richer context and classification to detected secrets, helping teams more quickly understand risk and prioritize remediation. Additional metadata is available via the Alerts API, with upcoming UI enhancements planned to surface this information directly in the product experience.
Code scanning now supports Rust
With GitHub Advanced Security, you can now scan Rust code using CodeQL. Rust is supported with CodeQL version 2.21.1+ when managing your own CodeQL toolchain, or with Advanced Security task version 1.1.137+, enabling security scanning for Rust projects. Buildless scanning (buildtype: none) for Rust is also available with CodeQL 2.23.3+, streamlining the analysis process for Rust codebases.
For more details, see the Rust is now generally available blog.
Expanded CodeQL buildless scanning for C/C++
CodeQL now supports buildless scanning (buildtype: none) for C/C++ projects, allowing teams to analyze code without requiring a full build. This is available with CodeQL version 2.21.4+ (when managing your own CodeQL toolchain) or Advanced Security task version 1.1.137+. Buildless scanning reduces setup complexity and shortens scan times while maintaining analysis coverage. For setup details, see Configure code scanning.
Next steps
Note
These features will roll out over the next two to three weeks.
Head over to Azure DevOps and take a look.
How to provide feedback
We would love to hear what you think about these features. Use the help menu to report a problem or provide a suggestion.
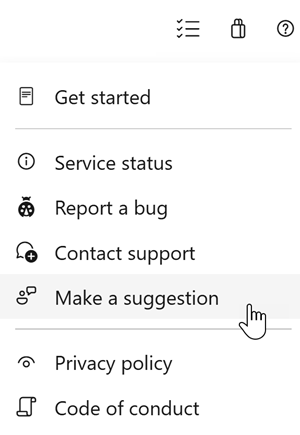
You can also get advice and your questions answered by the community on Stack Overflow.