Note
Access to this page requires authorization. You can try signing in or changing directories.
Access to this page requires authorization. You can try changing directories.
Copilot Autofix is an AI-powered feature of GitHub Advanced Security for Azure DevOps that generates suggested fixes for code scanning alerts. When CodeQL identifies a vulnerability or coding error, you can generate a fix for the alert directly from the Advanced Security tab. Copilot Autofix uses the Copilot coding agent to produce the fix and opens a pull request with the proposed change, so you can review, edit, and merge it through your normal pull request workflow.
Note
This feature is in limited public preview. Microsoft isn't currently accepting additional users for the preview.
Functionality might change or be removed without notice. Preview features have no Service Level Agreement (SLA) and limited support.
GitHub Advanced Security for Azure DevOps works with Azure Repos. To use GitHub Advanced Security with GitHub repositories, see GitHub Advanced Security.
Prerequisites
| Category | Requirements |
|---|---|
| Permissions | - To view a summary of all alerts for a repository: Contributor permissions for the repository. - To dismiss alerts in Advanced Security: Project administrator permissions. - To manage permissions in Advanced Security: Member of the Project Collection Administrators group or Advanced Security: manage settings permission set to Allow. |
For more information about Advanced Security permissions, see Manage Advanced Security permissions.
- Code scanning configured for your repository, using either default setup or advanced setup.
- At least one CodeQL code scanning alert.
- The Advanced Security: view alerts repository permission for the user who selects Generate fix.
- Access to the Azure Pipelines agent pool. Copilot Autofix queues a Microsoft-hosted pipeline job to generate and publish the fix. The run requires an available parallel job. If all parallel jobs are in use, the fix remains queued until capacity becomes available.
Copilot Autofix performs repository operations by using a dedicated identity named GitHub Copilot ({organization}), not a project or collection Build Service account. The service automatically grants the identity the following permissions:
| Operation | Permission |
|---|---|
| Access the project | View project-level information |
| Clone the repository | Read |
| Create and push the fix branch | Contribute and Create branch |
| Create and update the pull request | Contribute to pull requests |
| Read the code scanning alert | Advanced Security: view alerts |
| Add pull request discussions | Read and contribute to pull request discussions |
| Update the pipeline run | Update build information |
| Label the pull request | Create the Copilot Autofix label |
You don't need to grant these permissions to a Build Service account. If your organization uses explicit deny permissions, verify that they don't block the GitHub Copilot ({organization}) identity.
About Copilot Autofix
Copilot Autofix combines the analysis power of CodeQL with the large language model that powers the Copilot coding agent. When you generate a fix for a supported code scanning alert, Copilot Autofix analyzes the alert and the surrounding code, then opens a pull request that contains:
- A suggested code change that addresses the underlying vulnerability.
- A description of the alert being fixed, including the alert ID, severity, and a summary of the change.
Because the suggested fix considers the broader context of your code base, the change can span more than the single line where the alert was raised, and can include changes to other files where needed.
Note
Data handled by Copilot Autofix isn't used to train large language models (LLMs).
Important
Copilot Autofix suggestions are generated by an AI model and aren't guaranteed to be correct, complete, or secure. Always review the pull request carefully, validate that it resolves the alert without introducing new issues, and test your changes before you merge them.
Supported languages
Copilot Autofix supports the same languages that CodeQL analyzes for code scanning, including C/C++, C#, Go, Java/Kotlin, JavaScript/TypeScript, Python, Ruby, and Swift. For the current list of CodeQL-supported languages, see Language and query support.
Billing
Copilot Autofix is included with your GitHub Advanced Security for Azure DevOps license. Generating a fix consumes AI credits from your organization's Azure billing meter.
Each fix generation consumes tokens, which include input tokens for the code context sent to the model, output tokens for the suggested change, and cached tokens that reuse existing context.
To keep billing simple, these tokens are converted into a standard unit called a GitHub AI credit, where 1 credit equals $0.01 USD. The charges are billed to the Azure subscription linked to your Azure DevOps organization and appear as a separate meter in Azure Cost Management.
The cost of each fix varies with the size of the surrounding code context and the complexity of the change.
To monitor your daily charges, go to Subscription > Cost Management > Cost analysis in the Azure portal.
Enable Copilot Autofix
You can enable Copilot Autofix at the organization, project, or repository level. When you enable Autofix at a broader scope, the setting applies to all repositories within that scope. Choose where to configure Autofix based on the repositories you want the setting to apply to:
| Scope | Where to configure Autofix |
|---|---|
| Organization | Select Organization settings > Repositories to enable Autofix for all repositories in the organization. |
| Project | Select Project settings > Repositories > All Repositories to enable Autofix for all repositories in the project. |
| Repository | Select Project settings > Repositories, and then select a repository to enable Autofix for only that repository. |
To enable Copilot Autofix:
- Sign in to your Azure DevOps organization (
https://dev.azure.com/{yourorganization}). - Go to the settings page for the organization, project, or repository scope that you want to configure.
- In the Advanced Security section, open the Code Security features panel.
- Select the Autofix for code scanning alerts checkbox to create automatic fixes for code scanning alerts, generated by the Copilot coding agent.
- Select Apply to save your changes.
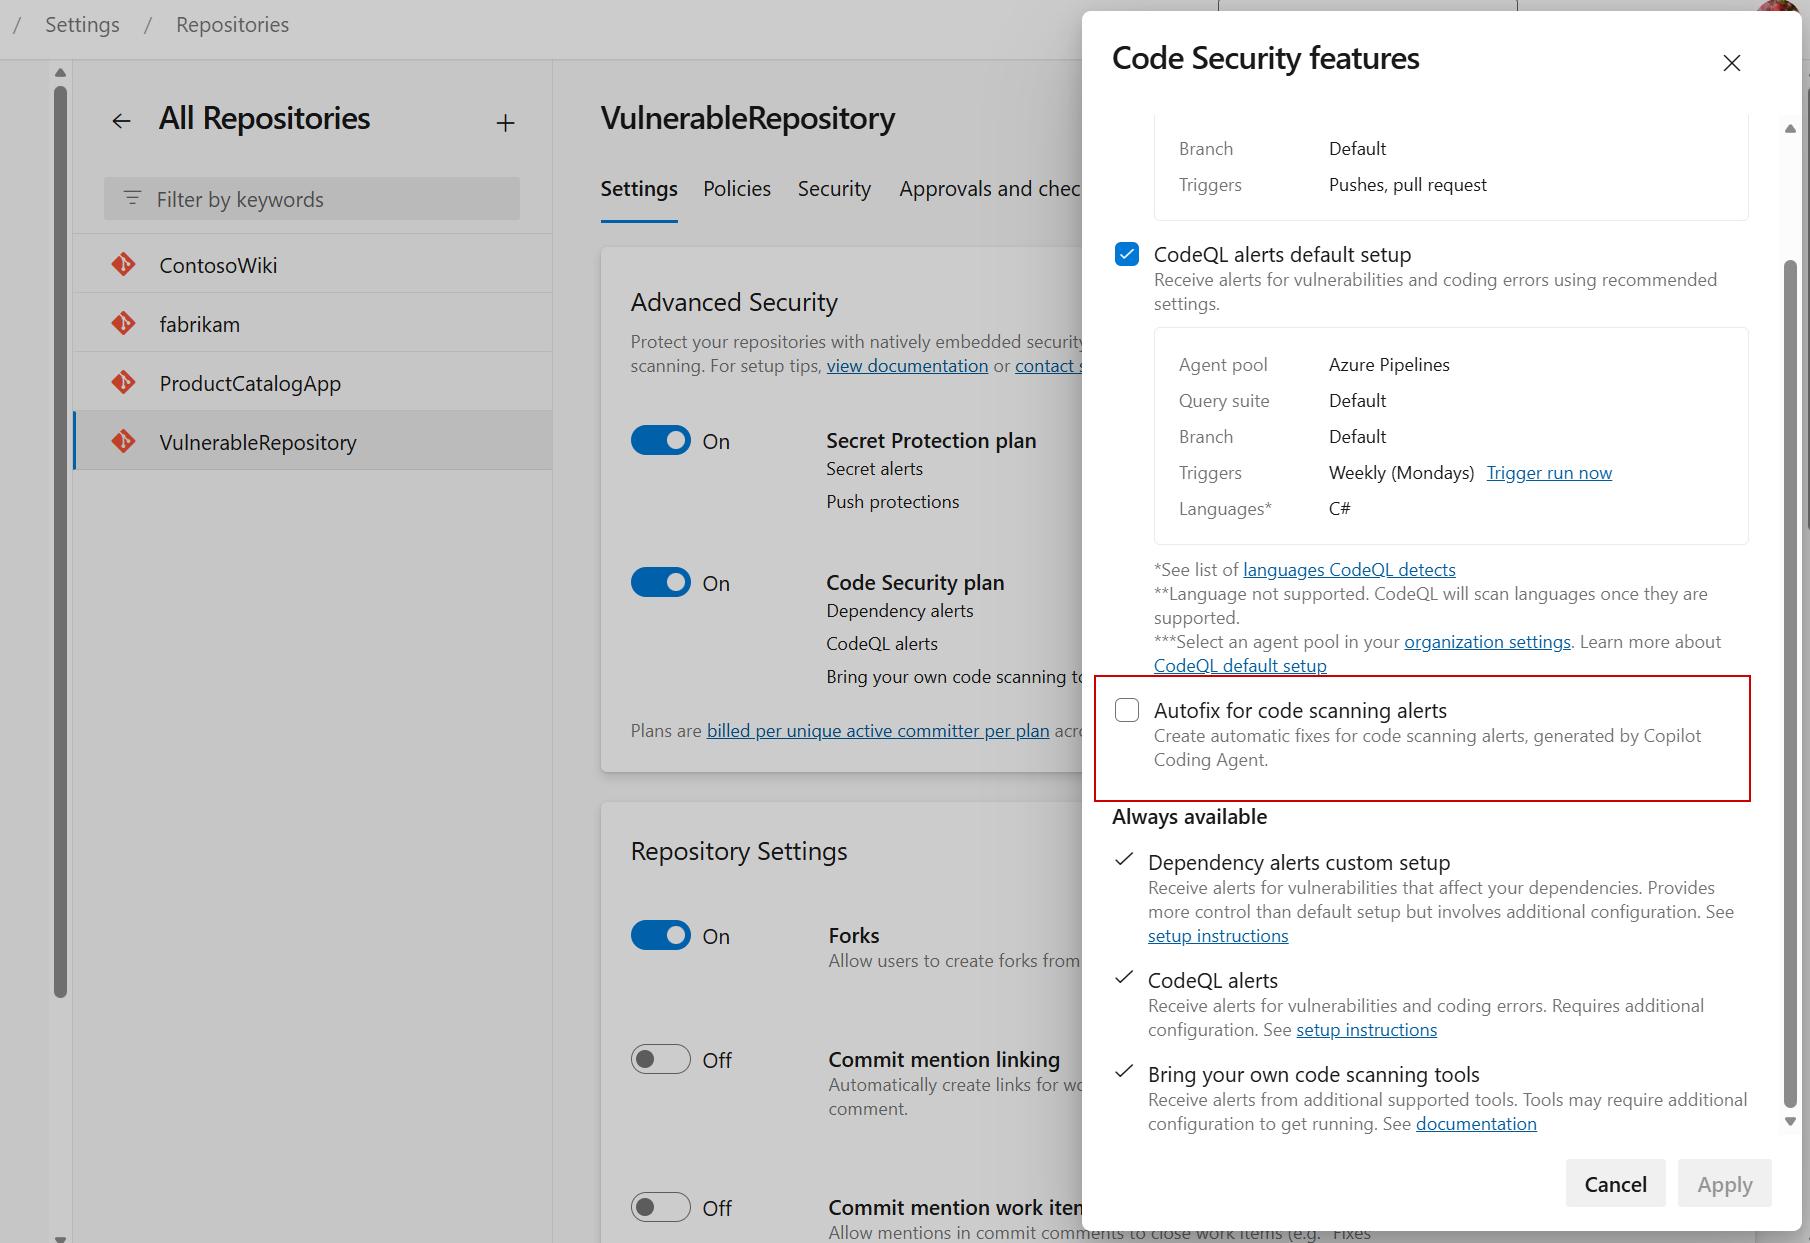
CodeQL must already be running and generating alerts for the repository. For more information, see Set up code scanning and Configure GitHub Advanced Security features.
Generate a fix for an alert
After you enable Copilot Autofix, you can generate a fix from any supported code scanning alert.
- Select Repos > Advanced Security.
- Select the Code scanning tab, and then select an alert to open its detail view.
- Review the alert's Location, Description, and Recommendation to understand the finding.
- Select Generate fix.
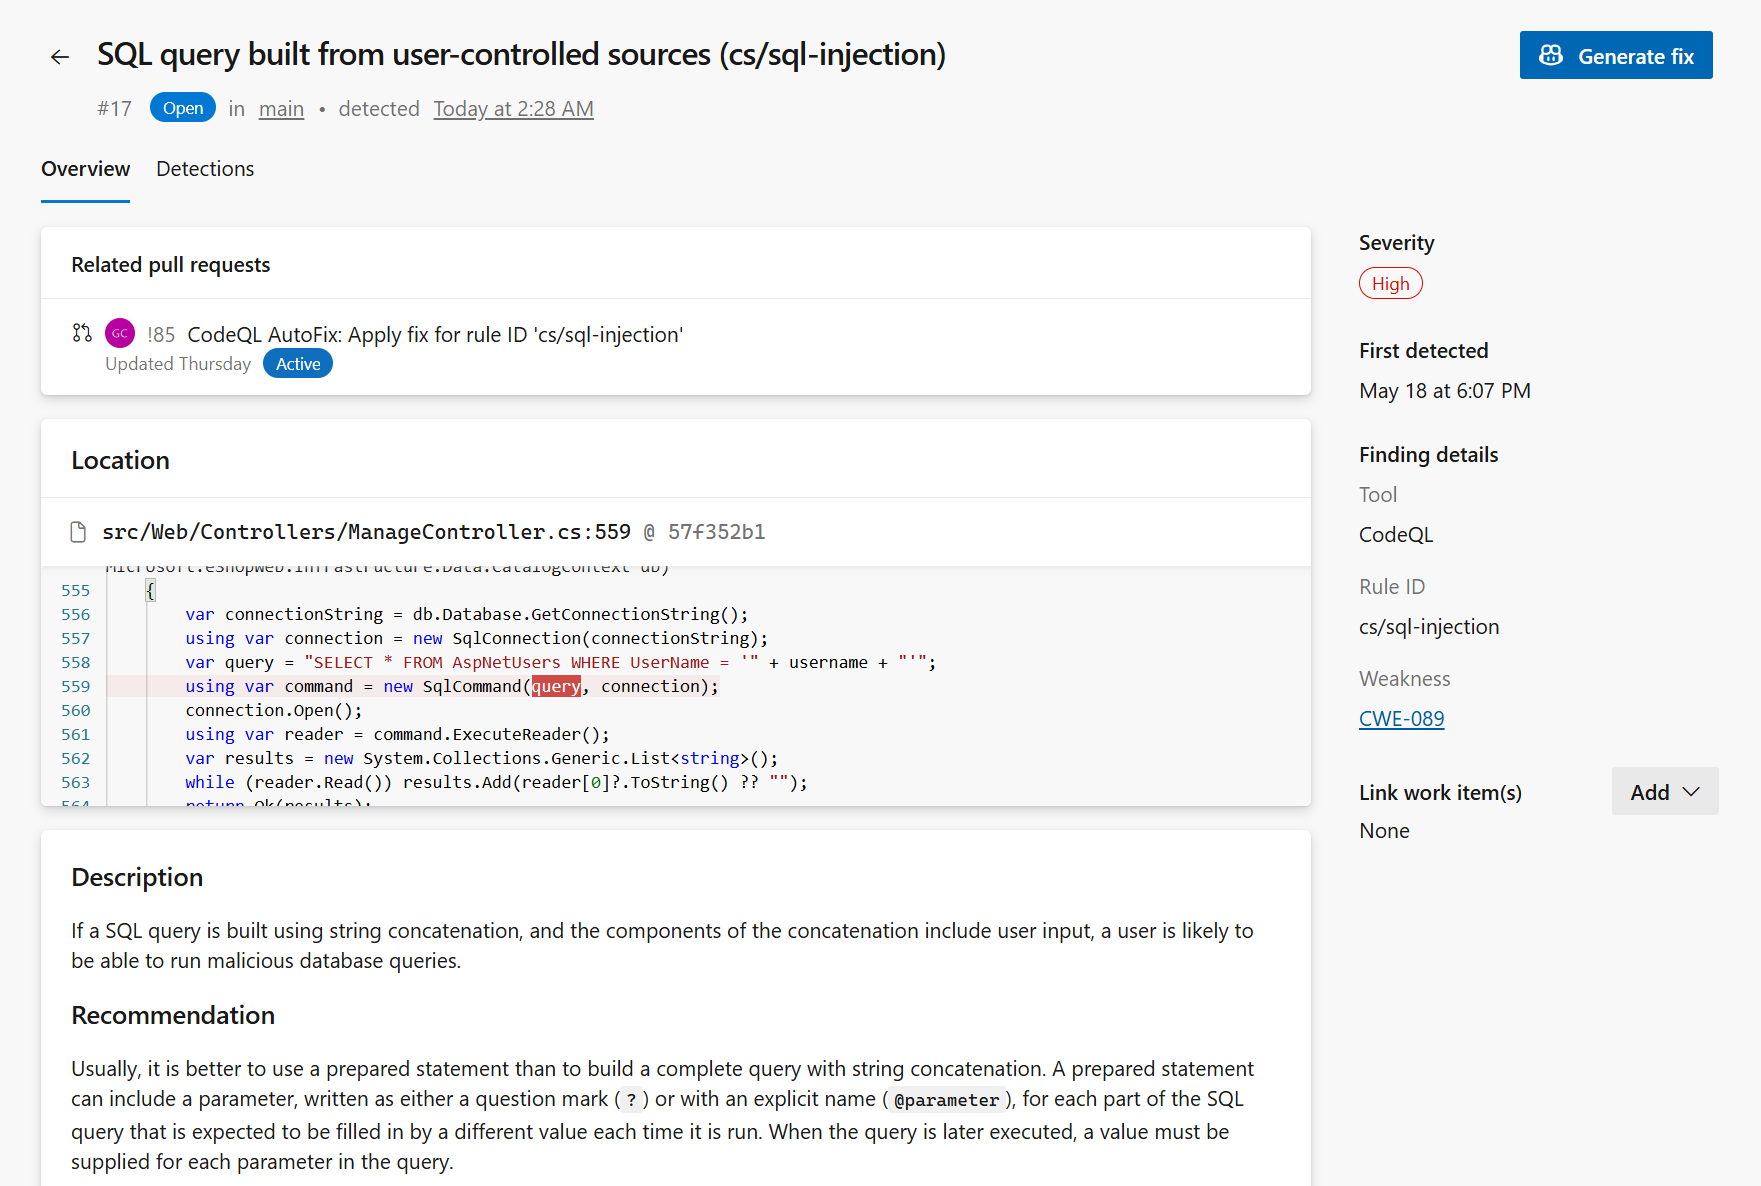
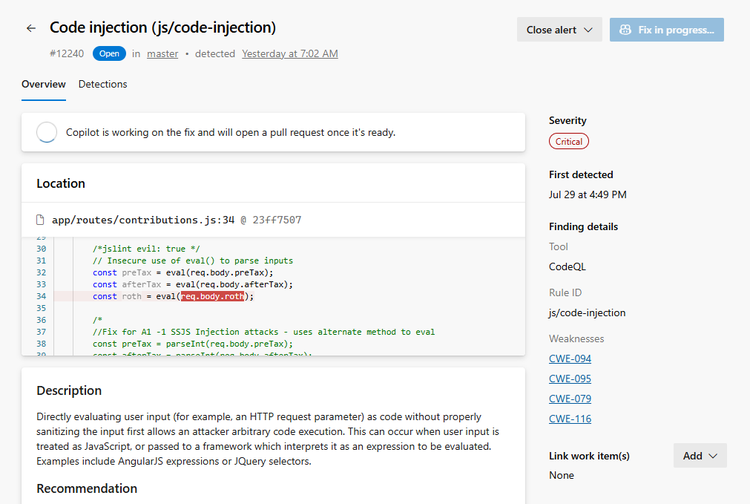
While Copilot Autofix works on the fix, the alert detail view shows that the fix is in progress. Copilot Autofix opens a pull request when the fix is ready.
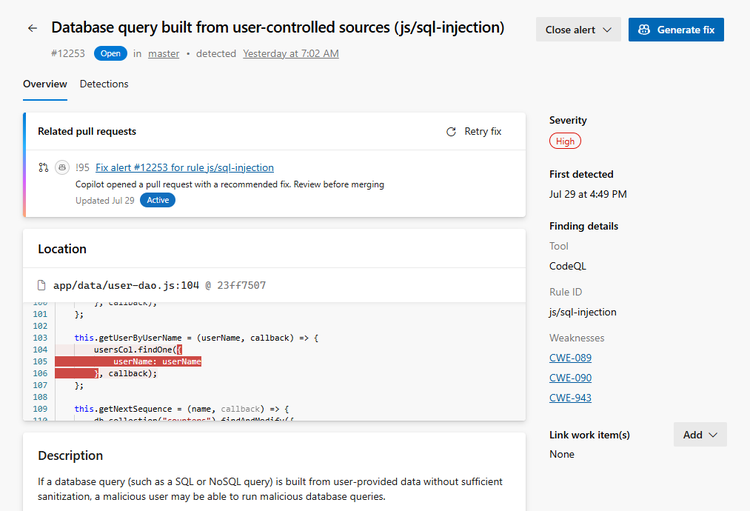
Copilot Autofix generates the fix and opens a pull request from a branch named copilot-autofix/.... The pull request is labeled with a Copilot Autofix tag, which you can use to identify Autofix pull requests in the pull requests list.
Only one fix can be active for the same alert and branch. While a request is pending or its pipeline is running, Generate fix is unavailable. If another request is submitted at the same time, the alert shows that a fix is already being generated. You can generate another fix after the active request succeeds or fails.
For CodeQL alerts, the pull request appears automatically under Related pull requests on the alert detail view and continues to update as generation and completion progress, so you don't need to refresh the page.
If Copilot Autofix doesn't produce any code changes for the alert, it doesn't create a branch or a pull request, and it doesn't link a pull request on the alert detail view. In this case, remediate the alert manually. For more information, see Fix isn't available.
Review and merge the fix
The pull request that Copilot Autofix opens behaves like any other Azure Repos pull request. Its description summarizes the alert that the fix addresses.
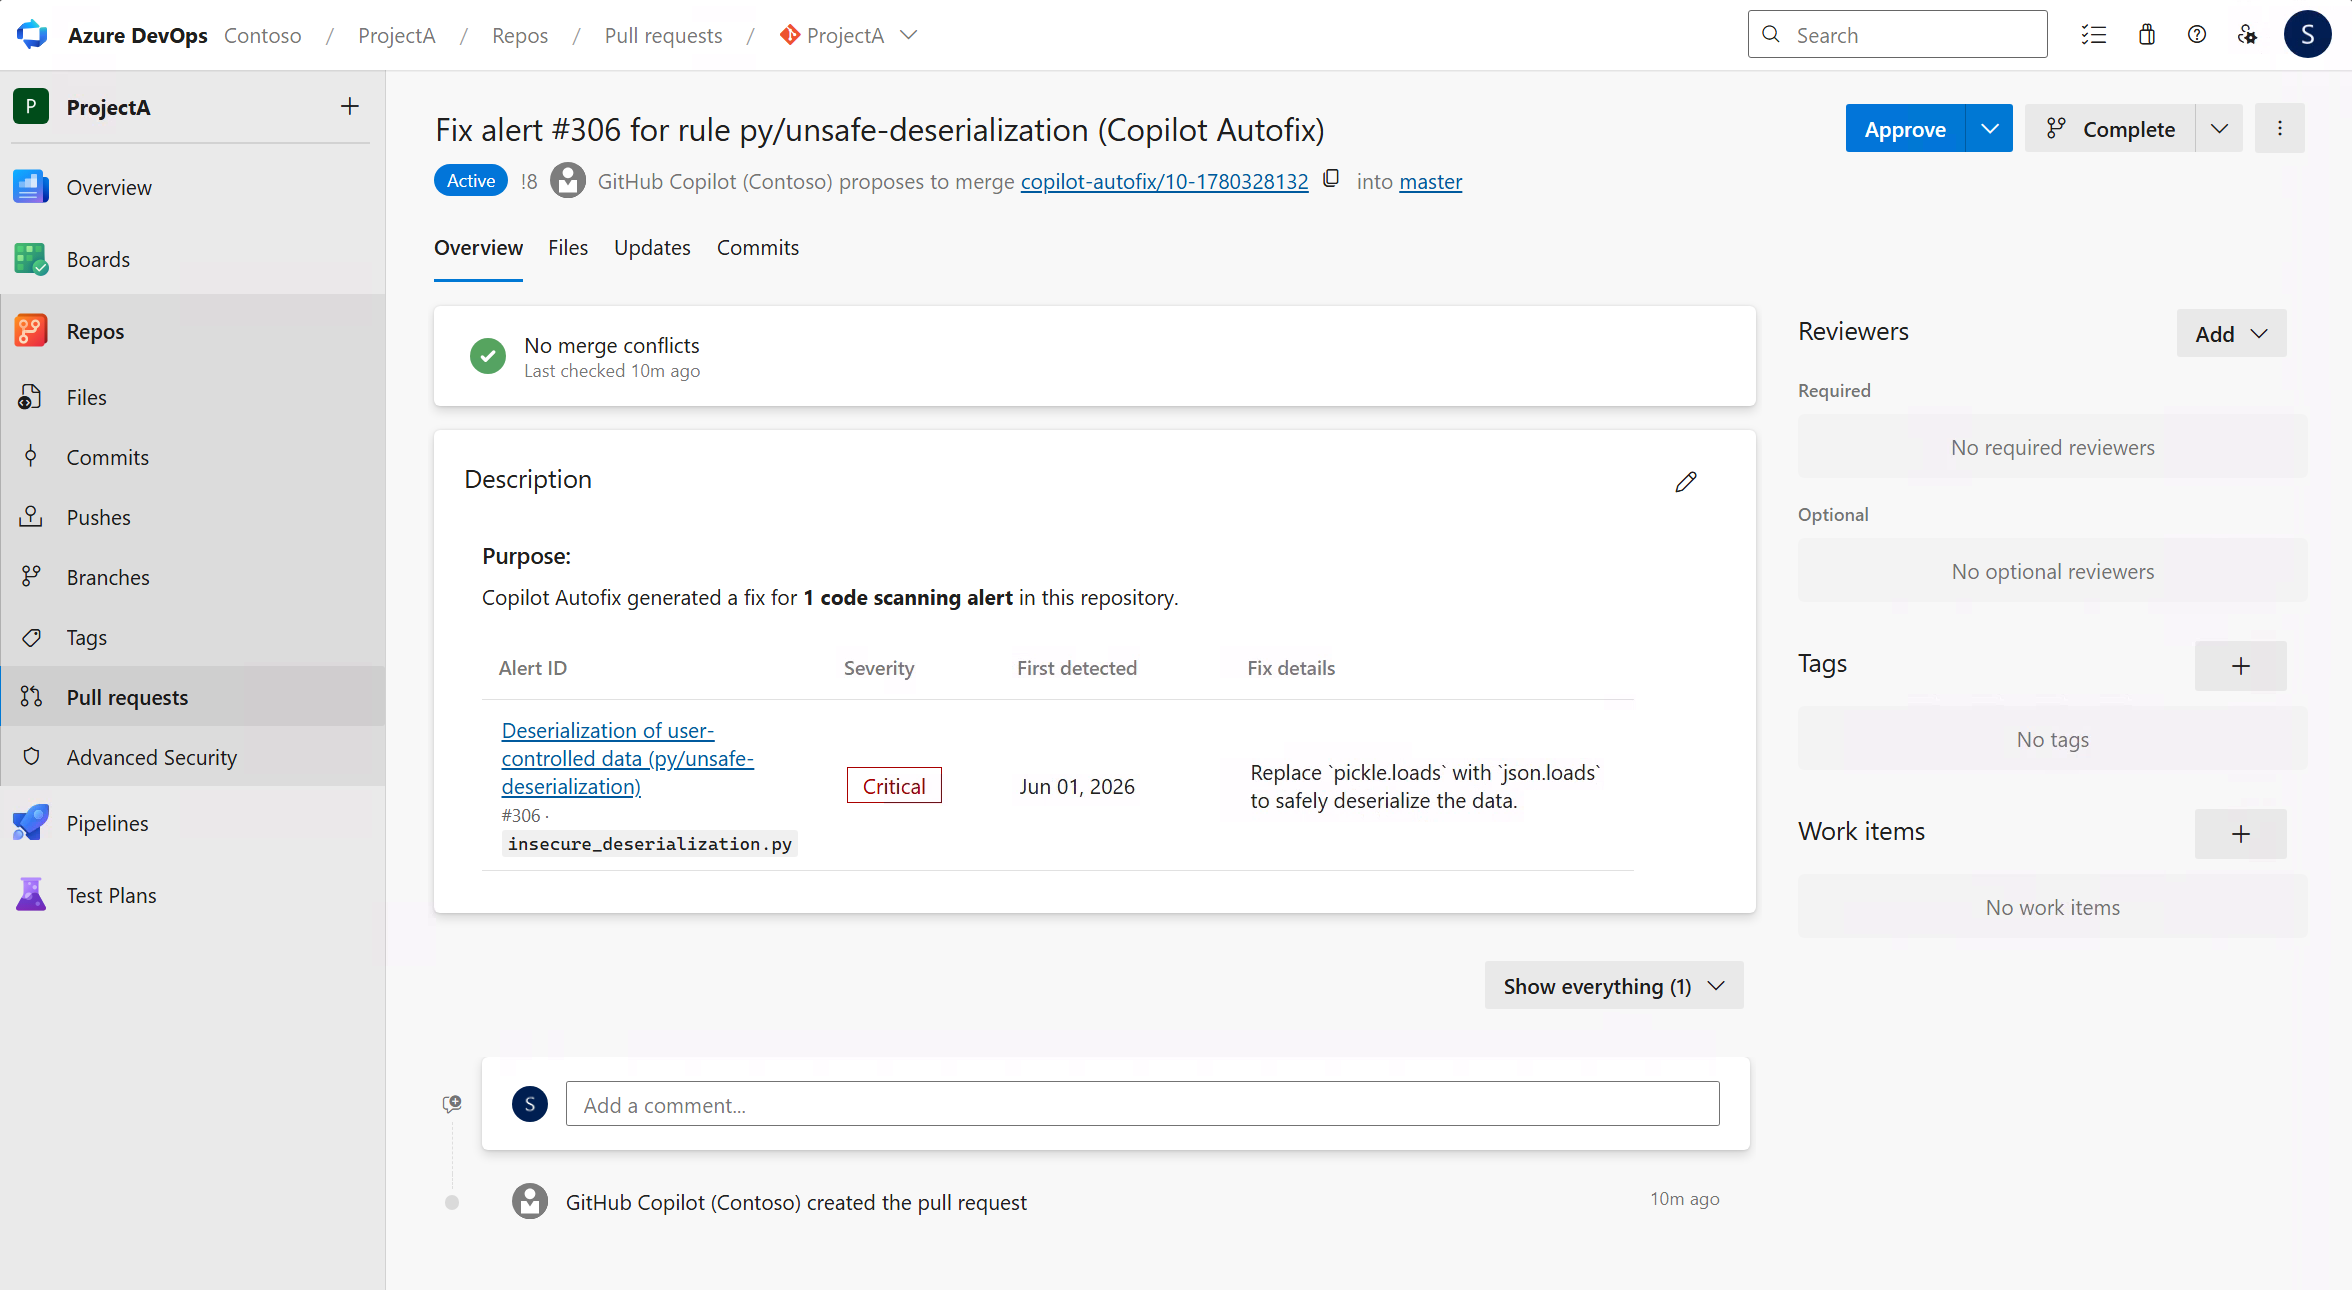
The Copilot Autofix label identifies autofix pull requests.
- Open the pull request from the alert's Related pull requests section, or from Repos > Pull requests.
- Review the proposed change in the Files tab across all affected files.
- Edit the change if you need to match your code style, naming conventions, or project requirements.
- Approve and complete the pull request through your normal review workflow.
After you merge the pull request, run CodeQL on the merged target branch and upload the new SARIF results. Copilot Autofix doesn't run this post-merge scan. The alert closes automatically after the updated analysis no longer reports the vulnerability.
Tip
A generated fix is a starting point, not a final answer. Treat the pull request like any other change: review it, test it, and request additional reviewers as needed before you merge.
Troubleshoot Copilot Autofix
Fix in progress
The time required to generate a fix varies based on the available pipeline capacity and the complexity of the change. If all parallel jobs are in use, the pipeline remains queued and the alert continues to show Fix in progress until capacity becomes available.
A request that remains pending before a pipeline is queued fails after 30 minutes. A queued or running pipeline has a two-hour timeout. The alert might stop updating automatically before the backend timeout is reached. If the alert remains in progress:
- Refresh the alert detail page.
- If View run is available, open the pipeline run and check whether it's queued or running.
- Wait for the request to reach a succeeded or failed state. Don't submit another request while the existing request is active.
- If the request fails, review the failure message and select Retry fix after you address the cause.
Pull request created but not linked to the alert
The pull request can be created successfully before it appears under Related pull requests. Refresh the alert detail page. If the pull request still isn't linked, select Repos > Pull requests and look for:
- The Copilot Autofix label.
- A source branch that begins with
copilot-autofix/. - A pull request title that references the code scanning alert.
Review and merge the pull request through the normal pull request workflow, even if the link doesn't appear on the alert.
Repository or pull request operations fail
Copilot Autofix performs a shallow clone of the branch associated with the alert. It doesn't initialize Git submodules. It creates a uniquely named copilot-autofix/... branch, pushes the generated change, and opens a pull request that targets the alert branch.
Use View run from the alert failure state to inspect the pipeline logs. The following table lists common causes and actions:
| Failure | What to check |
|---|---|
| The repository or branch can't be cloned | Verify that the repository and alert branch still exist. For an alert found in a pull request, the source branch and pull request must still be active. If the branch was deleted, run CodeQL on the current branch and generate a fix from the resulting alert. |
| The fix depends on code in a Git submodule | Copilot Autofix doesn't initialize submodules. Remediate the alert manually if the required code context is stored in a submodule. |
| The default branch changed or the alert branch was deleted | Copilot Autofix targets the branch associated with the alert, which isn't necessarily the current default branch. Run CodeQL on the intended branch and generate a fix from that branch's alert. |
| A fix branch can't be created | Check repository branch-name restrictions and explicit deny permissions for the GitHub Copilot ({organization}) identity. Allow branches with the copilot-autofix/ prefix. A retry creates a new uniquely named branch. |
| A branch policy blocks the change | Pull request completion policies apply to the Autofix pull request like any other pull request. Satisfy the required reviewers and validation policies before you complete it. If a repository policy blocks the initial push, update the policy to allow the Autofix identity and branch prefix. |
| The generated commit can't be pushed | Check the Contribute and Create branch permissions for the GitHub Copilot ({organization}) identity, including explicit denies. Also check commit author email validation as described in A fix was generated but couldn't be committed or pushed. |
| The pull request can't be created | Check the Contribute to pull requests permission and permission to create the Copilot Autofix label for the GitHub Copilot ({organization}) identity. |
A fix was generated but couldn't be committed or pushed
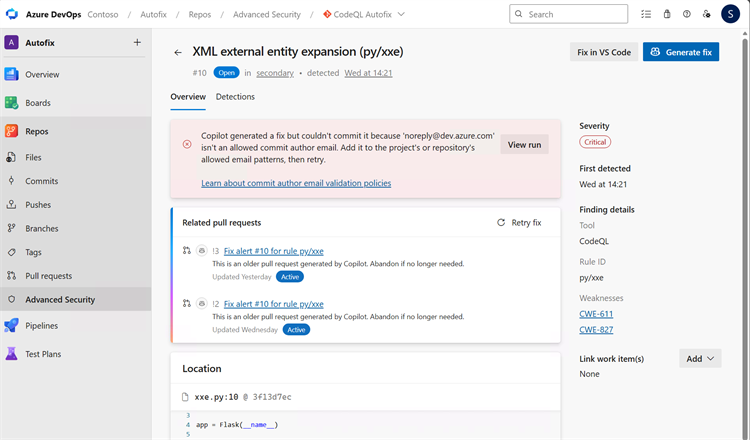
Copilot Autofix uses noreply@dev.azure.com as the commit author email. If a commit author email validation policy doesn't allow this address, Copilot Autofix can generate the code change but can't commit or push it to create the pull request.
The alert detail view shows an error that identifies the blocked commit author email.
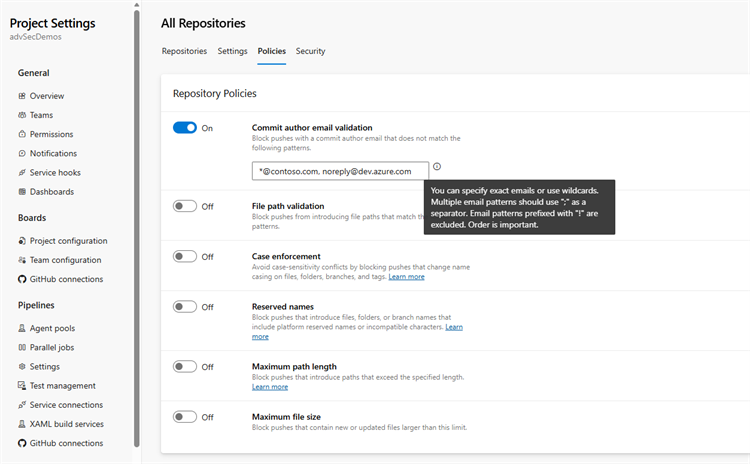
Add noreply@dev.azure.com to the allowed email patterns in the commit author email validation policy:
- Select Project settings > Repositories.
- Select All Repositories to update the project-level policy, or select the repository that has the policy.
- Select Policies.
- Under Repository Policies, find Commit author email validation.
- Add
noreply@dev.azure.comto the allowed email patterns. - Return to the code scanning alert and select Retry fix.
A run fails
If a Copilot Autofix run can't complete, the alert shows a prominent failure state so you can quickly see that the run didn't succeed. From the failure state, you can retry the run to generate a new fix.
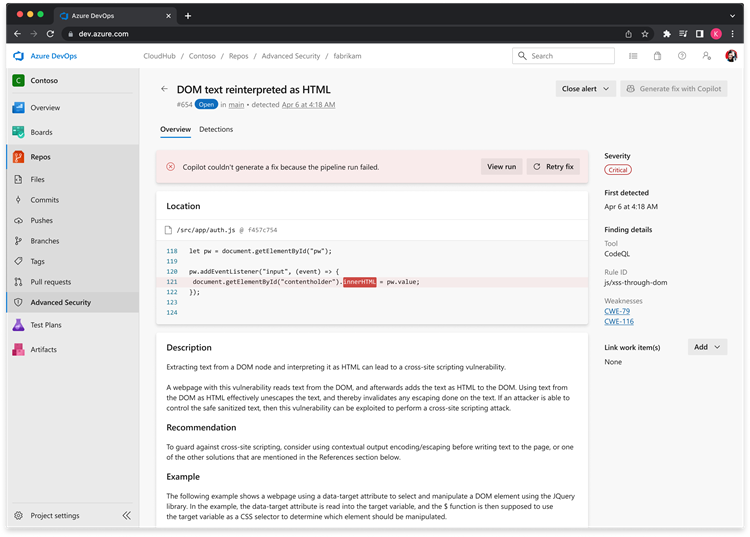
A run can fail for transient reasons, or when the run doesn't produce a usable code change. Retry the run to generate the fix again.
An alert remains open after you merge the fix
Merging an Autofix pull request doesn't close the alert until a later CodeQL analysis processes the merged code. If the alert remains open:
- Verify that the pull request was merged into the same branch where the alert was detected.
- Confirm that a CodeQL scan ran after the merge and analyzed the merged commit.
- Confirm that the scan successfully uploaded SARIF results for the correct repository and branch.
- Review the new results to verify that the vulnerability is no longer detected.
- If the vulnerability is still present, update the fix and run CodeQL again.
Fix isn't available
Copilot Autofix can't generate a fix for every alert. A fix might not be available when:
- The alert type isn't currently supported by Copilot Autofix.
- Copilot determines that the alert could be a false positive.
- A custom query or a third-party tool, rather than CodeQL, generates the alert.
- Copilot Autofix runs but doesn't produce any code changes. In this case, no branch or pull request is created.
If Copilot Autofix determines that the alert could be a false positive and doesn't produce any changes, the alert detail view shows the result. You can review the run or retry the fix.
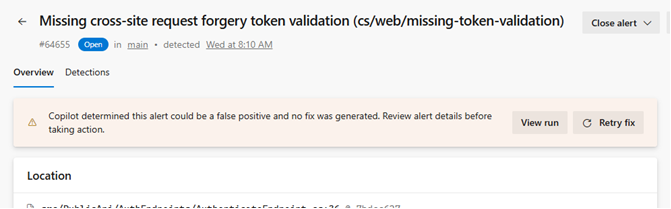
When a fix isn't available, use the Recommendation and Example sections of the alert to remediate it or dismiss the alert manually. For more information, see Alert details.