Note
Access to this page requires authorization. You can try signing in or changing directories.
Access to this page requires authorization. You can try changing directories.
Azure Managed Grafana can use its system-assigned managed identity, a user-assigned managed identity, or an app registration to authenticate to an Azure Monitor data source. The selected identity also needs an Azure role that authorizes it to read the monitoring data.
During workspace creation in the Azure portal, Monitoring Reader at the subscription scope is selected by default for the system-assigned managed identity. The role assignment is created only if the person creating the workspace has permission to assign Azure roles at that scope.
If the role wasn't assigned during creation, or if you want to use a narrower scope, follow the steps in this article. Grant access at the smallest scope that contains the monitoring data your dashboards need. You can assign the role at the subscription, resource group, or individual resource scope.
Note
The Monitoring Reader role provides access to Azure Monitor metrics and logs. To query Prometheus data in an Azure Monitor workspace, grant Monitoring Data Reader instead. For more information, see Connect an Azure Monitor workspace.
Prerequisites
- An Azure account with an active subscription. Create an account for free.
- An Azure Managed Grafana workspace. If you don't have one yet, create an Azure Managed Grafana workspace.
- An Azure resource that contains the monitoring data you want to visualize.
- The object ID of the identity used by your Azure Monitor data source:
- For managed identity authentication, configure the system-assigned or user-assigned managed identity.
- For app registration authentication, use the object ID of the app registration's service principal, not its application (client) ID.
- Permission to create role assignments at the selected scope, such as Role Based Access Control Administrator, User Access Administrator, or Owner.
- To use the Azure CLI instructions, Azure CLI version 2.75.0 or later. The
amgextension installs automatically when you first run anaz grafanacommand.
Sign in to Azure
For the portal instructions, sign in to the Azure portal with your Azure account.
For the Azure CLI instructions, sign in by running az login.
Edit Azure Monitor permissions
Use either the Azure portal or Azure CLI to assign a role to the identity used by your Azure Monitor data source.
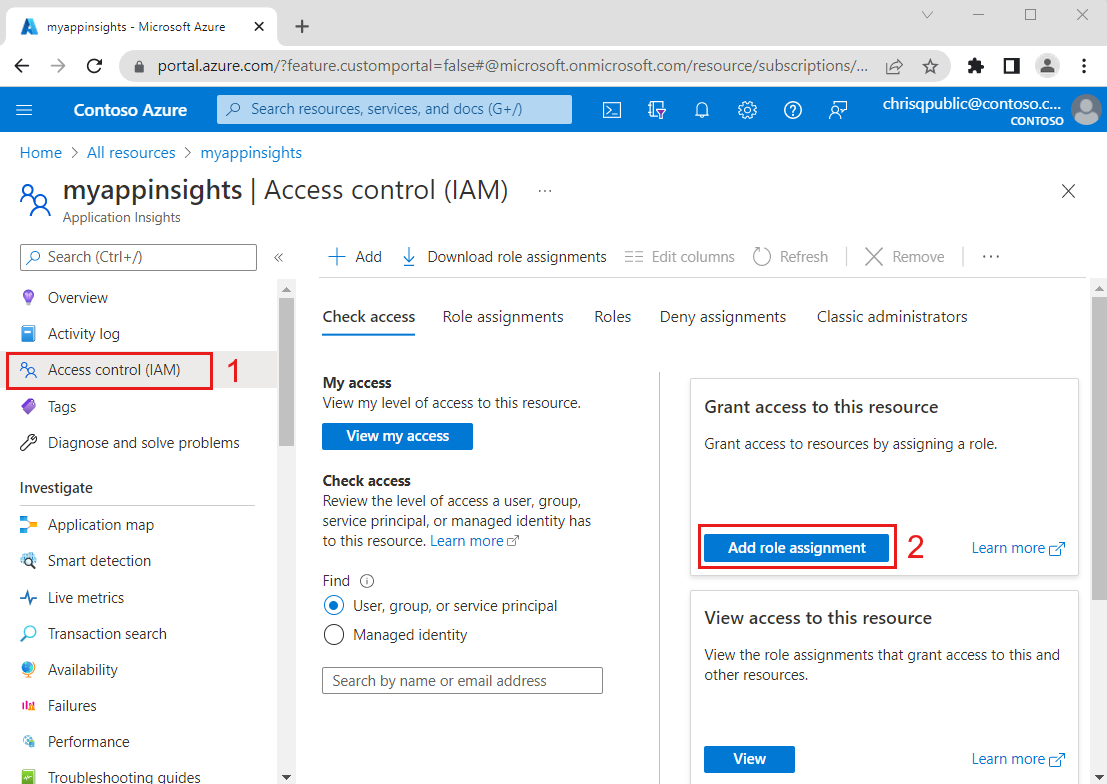
Open the subscription, resource group, or resource that contains the monitoring data you want Azure Managed Grafana to access.
Select Access control (IAM).
Select Add > Add role assignment.
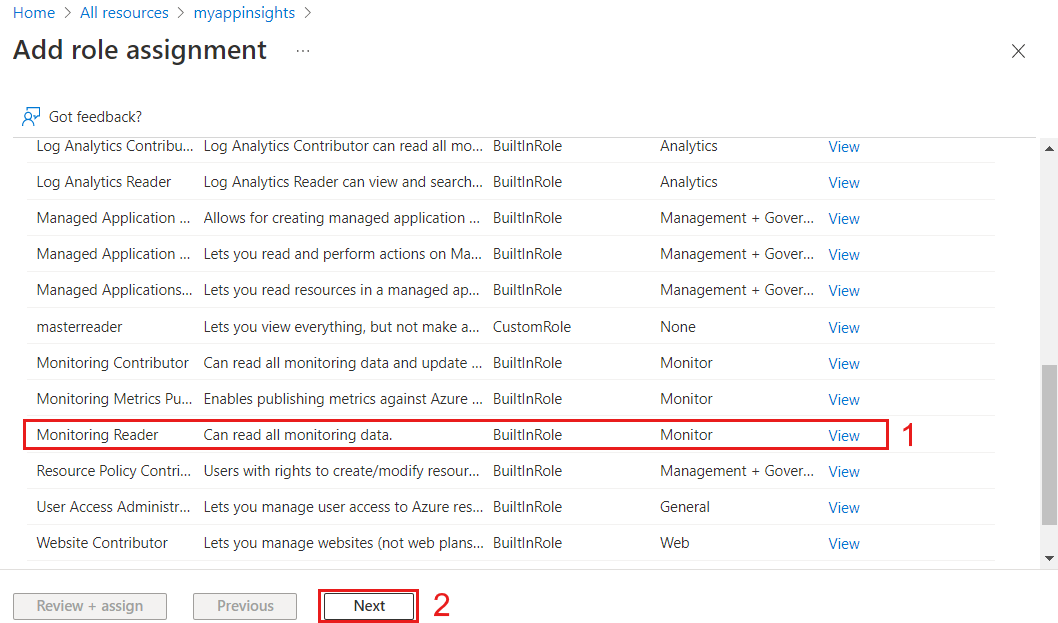
On the Role tab, select Monitoring Reader, and then select Next.
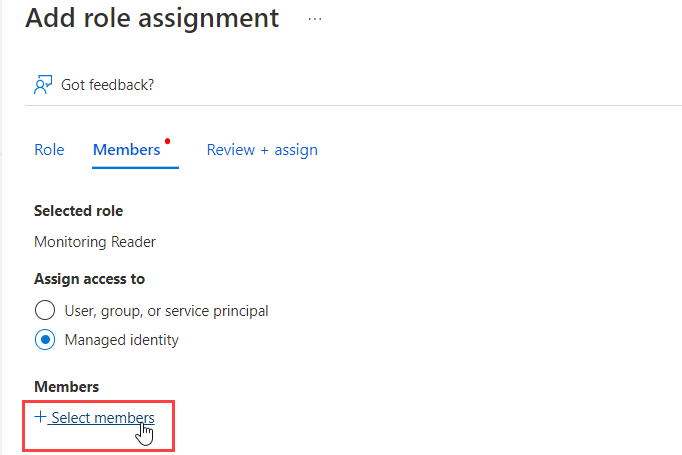
On the Members tab, select the member type for your data source identity:
- For a system-assigned or user-assigned managed identity, select Managed identity, and then select Select members.
- For an app registration, select User, group, or service principal, and then select Select members.
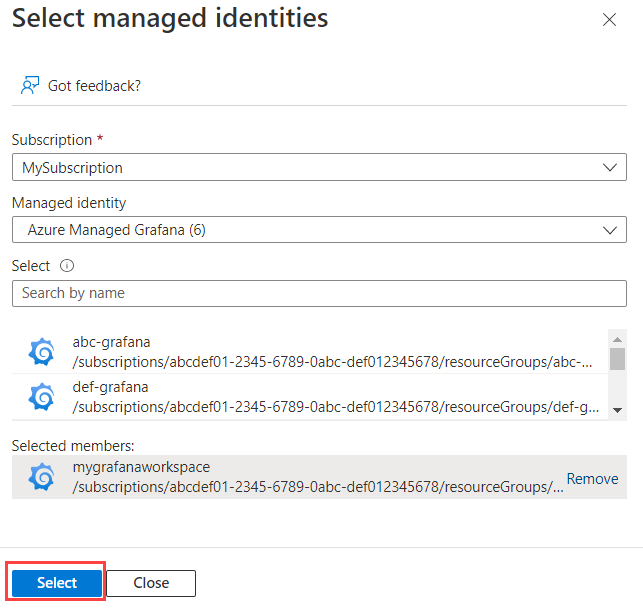
Select the identity used by your Azure Monitor data source:
- For the system-assigned identity, select Azure Managed Grafana, and then select your workspace.
- For a user-assigned identity, select User-assigned managed identity, and then select the identity.
- For an app registration, search for and select its name.
Select Select.
Select Review + assign, and then select Review + assign again to create the assignment.
To verify the assignment, return to Access control (IAM), select Role assignments, and confirm that your workspace has the Monitoring Reader role.
For more information about using Azure Managed Grafana with Azure Monitor, see Use Azure Managed Grafana with Azure Monitor.