Note
Access to this page requires authorization. You can try signing in or changing directories.
Access to this page requires authorization. You can try changing directories.
Applies to:
- Windows 365 Cloud PCs
- Azure Virtual Desktop session hosts
Overview
Display protection helps protect Windows 365 Cloud PC and Azure Virtual Desktop session video from screen capture malware on the user's local Windows device. The local device is the physical Windows device running Windows App. It supports both managed endpoints and unmanaged or bring-your-own-device (BYOD) endpoints.
Display protection doesn't require a GPU-enabled Cloud PC. Hardware-based protection uses a compatible GPU on the endpoint.
The feature uses Microsoft PlayReady to encrypt remote-session video and protect its decryption on the endpoint. Depending on the configured protection level and endpoint capabilities, it uses either hardware DRM (digital rights management) or software DRM:
- Hardware DRM (SL3000) uses hardware-backed PlayReady protection with a compatible endpoint GPU, which can be discrete or integrated.
- Software DRM (SL2000) uses software-based PlayReady protection. Software fallback is allowed only when the configured protection level permits it.
For background on these security levels, see PlayReady security levels.
Note
Input protection is in public preview and is a separate component of Input and Output Protection that protects keyboard input against keylogger threats. Input protection is configured independently from display protection. For more information, see Input Protection (preview).
How display protection works
Display protection adds a protected video path between the remote session and the endpoint's PlayReady decryption environment. The feature includes:
- Protected video decryption: Remote-session video is encrypted before it leaves the Cloud PC or session host. PlayReady protects decryption on the endpoint.
- Protection-level enforcement: A connection is allowed only when Windows App can establish the configured PlayReady protection level.
- Configurable protection levels: Organizations can allow hardware or software DRM, or require hardware DRM and block endpoints that can't meet that requirement.
- Session-specific protection: Protection applies to remote-session video, not to other applications running locally on the endpoint.
Protection boundaries
Hardware DRM and High-bandwidth Digital Content Protection (HDCP) protect different parts of the display path. Hardware DRM protects video decryption on the endpoint. HDCP concerns the physical output connection from the endpoint to a connected display, such as an HDMI or DisplayPort connection.
Display protection doesn't currently enforce HDCP, including when Hardware enforcement required is selected. That setting requires hardware DRM, not HDCP-capable monitors, docks, or adapters. Non-HDCP equipment isn't automatically rejected because it lacks HDCP support.
HDCP enforcement for external display connections is planned as a separate configuration option in a future update. It isn't available in the current release.
The feature is designed to help protect against malware on the device running Windows App, not to prevent a user from intentionally disclosing content they can view. It doesn't authenticate external displays or capture devices, guarantee that external capture hardware can't record the output, or prevent someone from photographing the screen. Don't treat a successful hardware DRM connection as proof that the external display path is protected.
Supported configurations
This feature supports the following configurations:
- Cloud PC or session host: Windows 365 Cloud PC or Azure Virtual Desktop session host running a supported Windows client OS version or Windows Server.
- Supported clients: Windows App on Windows, when running on a physical Windows 11 device.
- Not supported clients: Virtual endpoint devices (VMs), macOS, iOS, Android, web browsers.
Prerequisites
Before you configure display protection, ensure the following requirements are met:
- Windows App: Version 2.0.1236.0 or newer on Windows. Update to the latest version from the Microsoft Store.
Configure display protection
Enable display protection for the Cloud PCs or Azure Virtual Desktop session hosts you want to protect. Use the relevant configuration path for Azure Virtual Desktop or Windows 365.
Display protection levels
Both Azure Virtual Desktop and Windows 365 support the following protection levels. The hardware and software labels refer to PlayReady protection on the endpoint, not to HDCP enforcement on connected displays.
| Level | Description |
|---|---|
| Not configured | Display protection isn't enabled for the Cloud PC or session host. |
| Hardware or software enforcement | Uses hardware DRM (SL3000) when available. If the endpoint can't provide hardware DRM, software DRM (SL2000) is allowed. |
| Hardware enforcement required | Requires hardware DRM (SL3000). If the endpoint can't provide it, the connection is blocked and the user sees an error. This level doesn't permit software DRM fallback. |
Configure display protection for Azure Virtual Desktop
For Azure Virtual Desktop, add the display protection RDP property in the host pool advanced settings:
In the Azure portal, open the target host pool.
Go to RDP properties > Advanced tab.
Add the following RDP property:
enableWindowsCloudIODisplayProtection:i:<value>Where
<value>is:0(not configured),1(hardware or software enforcement), or2(hardware enforcement required).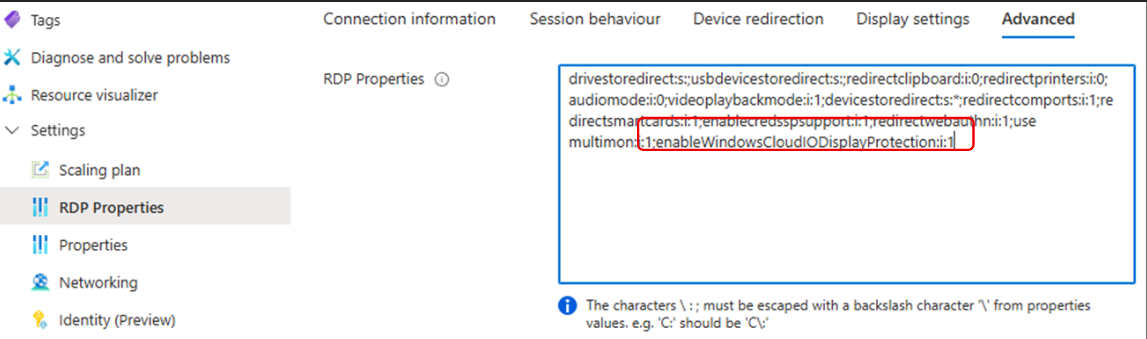
This property enables server-side verification that Display Protection is enforced on the endpoint.
Configure display protection for Windows 365
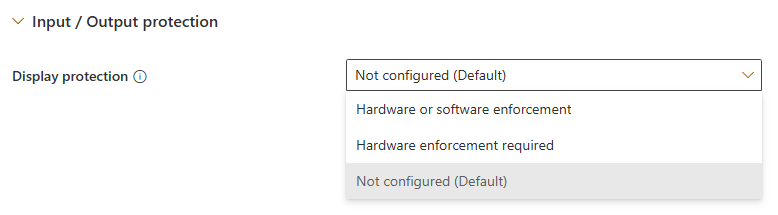
For Windows 365, configure display protection in Microsoft Intune:
Sign in to the Microsoft Intune admin center.
Go to Devices > Manage Windows 365 Cloud PCs > Cloud PC Settings.
Under IO Protection, select the desired level for Display Protection.
When you enable display protection or change its level in Intune or in host pool RDP properties, the setting is delivered to the endpoint device through the connection (RDP) properties and is cached on the device. To apply an updated configuration immediately, select Refresh in Windows App. Otherwise, configuration changes can take up to 8 hours to reach an endpoint.
If a connection is unexpectedly blocked with an incompatible-client error shortly after you enable or change display protection, select Refresh in Windows App to pull the latest configuration, or wait for it to propagate—up to 8 hours—and then try to connect again.
Validate protection
After you configure display protection on the target Cloud PCs or session hosts:
- From a Windows 11 physical endpoint, open Windows App (version 2.0.1236.0 or newer).
- Connect to a Cloud PC or session host that has display protection enabled.
- Verify that the connection succeeds without an error message.
- Attempt to use a screen capture tool on the endpoint while the remote session is active. The captured content from the remote session should be blocked or appear blank.
This capture test evaluates behavior on the endpoint. It doesn't validate HDCP enforcement or show that an external capture device is blocked.
To monitor display protection across your tenant, use Cloud PC monitoring (preview) and review the DisplayProtectionState connection event on the Connection health page. For steps, see Monitor Input and Output Protection.
Troubleshoot display protection
If display protection can't be established at the configured level, the connection is blocked and an error appears on the endpoint. Check the following:
- Use a supported physical Windows 11 endpoint and Windows App version.
- If you recently enabled or changed display protection, select Refresh in Windows App to retrieve the updated configuration, or allow up to 8 hours for propagation.
- If you require hardware enforcement, verify that the endpoint can provide hardware DRM. This requirement is separate from the HDCP capability of the attached display.
For help with connection errors, see Troubleshoot connection errors. If the issue continues, contact Microsoft support and provide the activity ID, timestamp of the failure, and steps to reproduce the issue.
Limitations and considerations
- Physical devices only: Display protection requires a physical Windows 11 endpoint. Virtual machines aren't supported as endpoint devices.
- Supported clients: Windows App on Windows is the only supported client for display protection.
- Not supported clients: Virtual endpoint devices (VMs), macOS, iOS, Android, web browsers, and other non-Windows App on Windows clients, including Windows 365 Link devices.
- External displays, docks, and adapters: HDCP support alone doesn't determine whether an endpoint meets the configured PlayReady protection level. Don't assume that display protection blocks a non-HDCP monitor, a DisplayLink dock, or a USB display adapter. Validate the endpoint and display setup against your selected protection level; this doesn't establish protection against external capture devices.
- Performance with software DRM: When hardware DRM isn't available and the configured level allows software DRM, the session uses software DRM. Software DRM can increase the time needed to establish a session. If hardware enforcement is required instead, the connection is blocked rather than falling back.
- Display resolution: Display protection supports resolutions up to 4K (3840 x 2160). 5K monitors aren't currently supported. Use a 4K or lower-resolution monitor for protected sessions.
Related features
- Input Protection (preview): Protects keyboard input against keylogger threats. Input protection is a separate component of Input and Output Protection and is configured independently from display protection.
- Enable screen capture protection: A separate screen capture protection feature for Azure Virtual Desktop.
- Watermarking: Adds visible watermarks to remote sessions to discourage photo-based screen capture.