Microsoft Security DevOps는 정적 분석 도구를 개발 수명 주기에 통합하는 명령줄 애플리케이션입니다. Security DevOps는 SDL, 보안 및 규정 준수 도구와 같은 최신 버전의 정적 분석 도구를 설치, 구성 및 실행합니다. 보안 DevOps는 여러 환경에서 결정적 실행을 가능하게 하는 이식 가능한 구성으로 데이터 기반입니다.
Microsoft Security DevOps는 다음 오픈 소스 도구를 사용합니다.
| Name | 언어 | License |
|---|---|---|
| 맬웨어 방지 | 맬웨어를 검색하고 맬웨어가 발견되면 빌드를 중단하는 엔드포인트용 Microsoft Defender Windows 맬웨어 방지 보호. 이 도구는 windows-latest 에이전트에서 기본적으로 검색합니다. | 오픈 소스 아님 |
| Bandit | Python | Apache 라이선스 2.0 |
| BinSkim | 바이너리--Windows, ELF | MIT 라이선스 |
| Checkov | Terraform, Terraform 플랜, CloudFormation, Amazon Web Services(AWS) SAM, Kubernetes, Helm 차트, Kustomize, Dockerfile, Serverless, Bicep, OpenAPI, ARM | Apache 라이선스 2.0 |
| ESlint | JavaScript | MIT 라이선스 |
| 템플릿 분석기 | ARM 템플릿, Bicep | MIT 라이선스 |
| Terrascan | Terraform(HCL2), Kubernetes(JSON/YAML), Helm v3, Kustomize, Dockerfiles, CloudFormation | Apache 라이선스 2.0 |
| Trivy | 컨테이너 이미지, IaC(Infrastructure as Code) | Apache 라이선스 2.0 |
사전 요구 사항
Microsoft Security DevOps GitHub 작업을 설정하기 전에 다음 전제 조건을 반드시 확인하세요:
Azure 구독입니다. Azure 구독이 아직 없는 경우 시작하기 전에 Azure 체험 계정을 만듭니다.
새 창에서 Microsoft Security DevOps GitHub 작업을 엽니다.
워크플로 권한이 GitHub 리포지토리에서 읽기 및 쓰기로 설정되어 있는지 확인합니다. 이 단계에는 클라우드용 Microsoft Defender와 페더레이션하기 위해 GitHub 워크플로에서
ID-token: write권한을 설정하는 작업이 포함됩니다.
GitHub 액션 워크플로우를 설정하세요
GitHub 작업을 설정하려면 다음을 수행합니다.
GitHub에 로그인하세요.
GitHub 작업을 구성하려는 리포지토리를 선택합니다.
작업을 선택합니다.
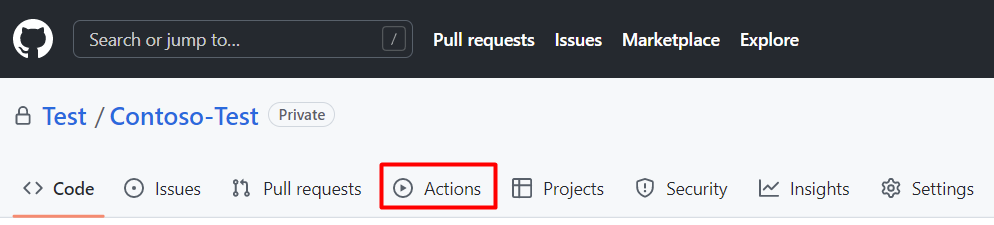
새 워크플로를 선택합니다.
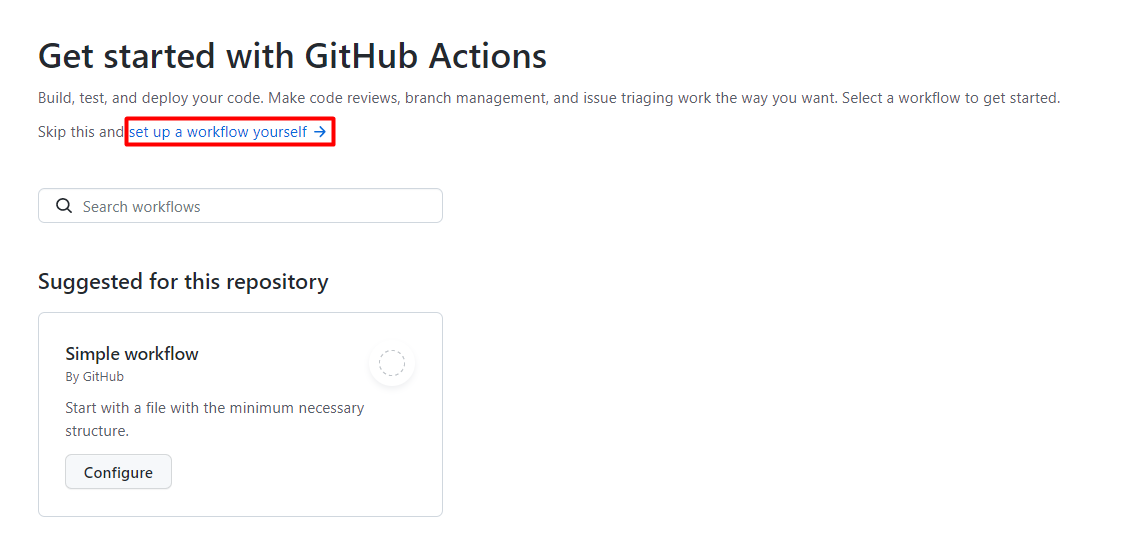
'GitHub Actions로 시작하기'에서 '직접 워크플로우를 설정하기'를 선택하세요.
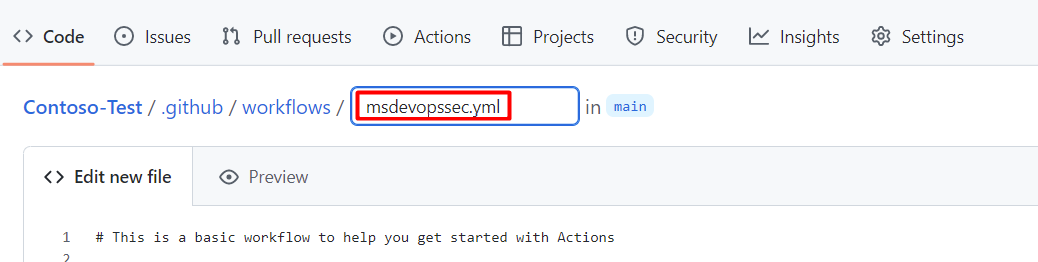
워크플로우 파일 이름을 입력하세요. 예를 들어, msdevopssec.yml.
다음 샘플 액션 워크플로우 를 새 파일 편집 탭에 복사해서 붙여넣으세요.
name: MSDO
on:
  push:
    branches:
      - main

jobs:
  sample:
    name: Microsoft Security DevOps

    # Windows and Linux agents are supported
    runs-on: windows-latest

    permissions:
      contents: read
      id-token: write
      actions: read
      # Write access for security-events is only required for customers looking for MSDO results to appear in the codeQL security alerts tab on GitHub (Requires GHAS)
      security-events: write

    steps:

      # Checkout your code repository to scan
    - uses: actions/checkout@v3

      # Run analyzers
    - name: Run Microsoft Security DevOps
      uses: microsoft/security-devops-action@latest
      id: msdo
    # with:
      # config: string. Optional. A file path to an MSDO configuration file ('*.gdnconfig').
      # policy: 'GitHub' | 'microsoft' | 'none'. Optional. The name of a well-known Microsoft policy. If no configuration file or list of tools is provided, the policy may instruct MSDO which tools to run. Default: GitHub.
      # categories: string. Optional. A comma-separated list of analyzer categories to run. Values: 'code', 'artifacts', 'IaC', 'containers'. Example: 'IaC, containers'. Defaults to all.
      # languages: string. Optional. A comma-separated list of languages to analyze. Example: 'javascript,typescript'. Defaults to all.
      # tools: string. Optional. A comma-separated list of analyzer tools to run. Values: 'bandit', 'binskim', 'checkov', 'eslint', 'templateanalyzer', 'terrascan', 'trivy'.

      # Upload alerts to the Security tab - required for MSDO results to appear in the codeQL security alerts tab on GitHub (Requires GHAS)
    # - name: Upload alerts to Security tab
    #  uses: github/codeql-action/upload-sarif@v3
    #  with:
    #    sarif_file: ${{ steps.msdo.outputs.sarifFile }}

      # Upload alerts file as a workflow artifact - required for MSDO results to appear in the codeQL security alerts tab on GitHub (Requires GHAS)
    # - name: Upload alerts file as a workflow artifact
    #  uses: actions/upload-artifact@v3
    #  with:
    #    name: alerts
    #    path: ${{ steps.msdo.outputs.sarifFile }}
메모
더 많은 도구 구성 옵션과 지침은 Microsoft Security DevOps 위키를 참조하세요.
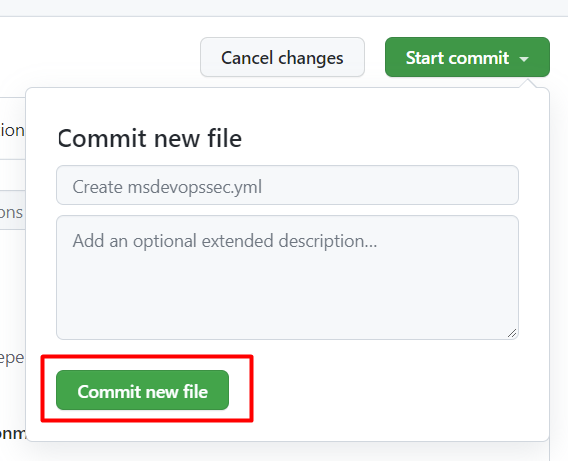
커밋 시작을 선택합니다.
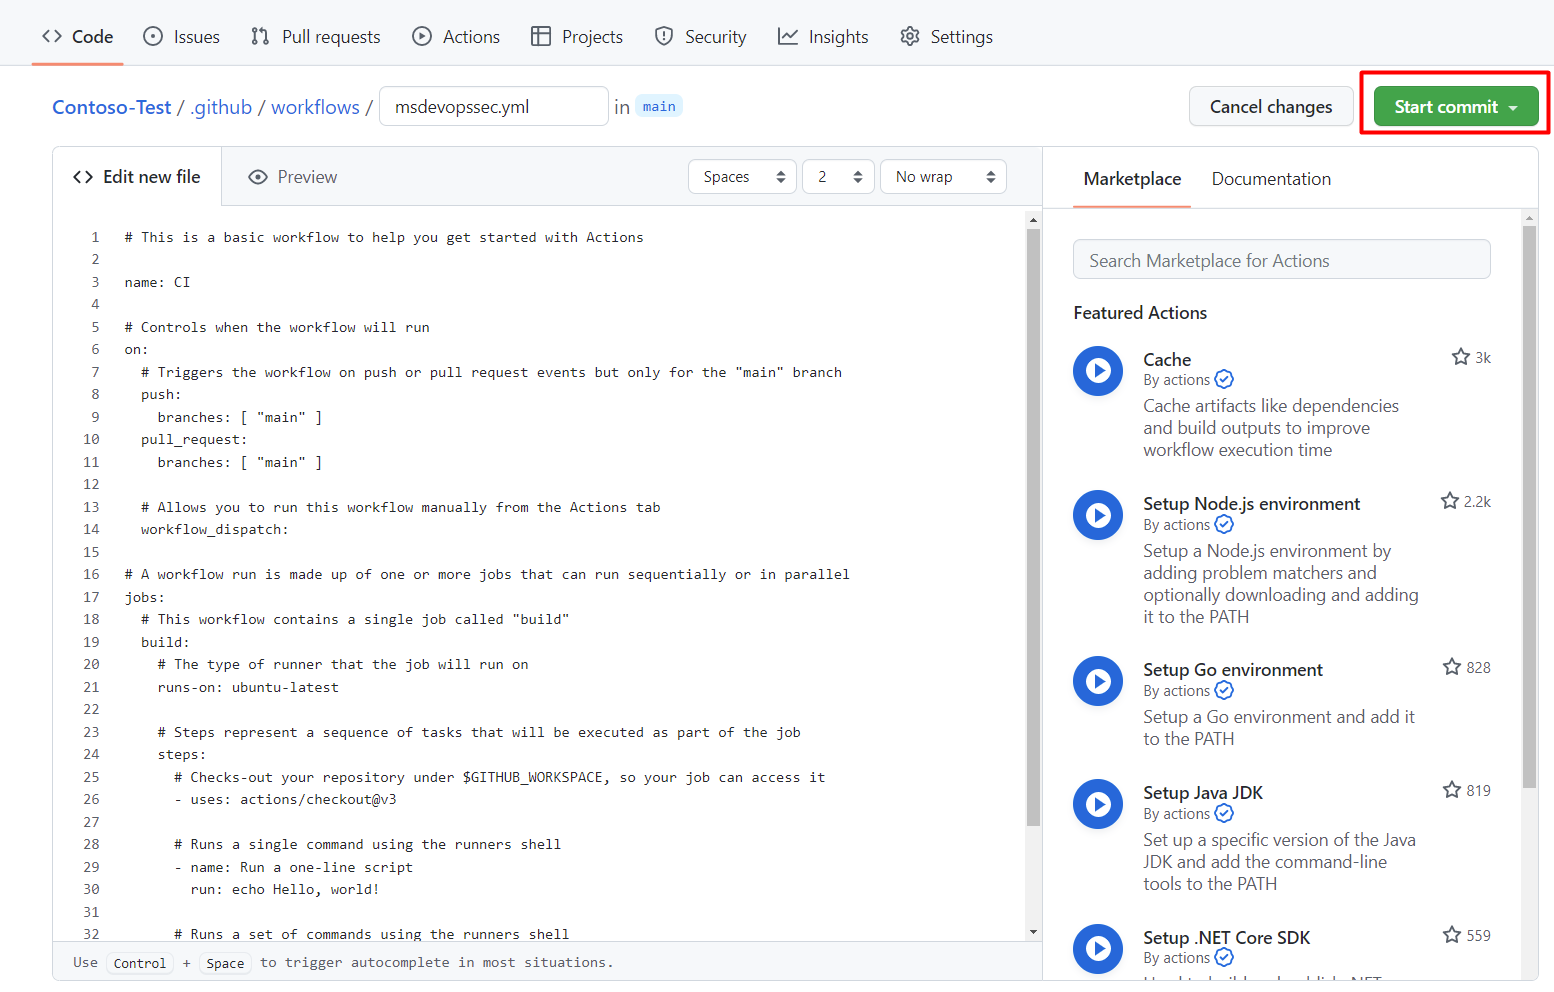
새 파일 커밋을 선택합니다. 이 과정은 완료하는 데 최대 1분이 걸릴 수 있습니다.
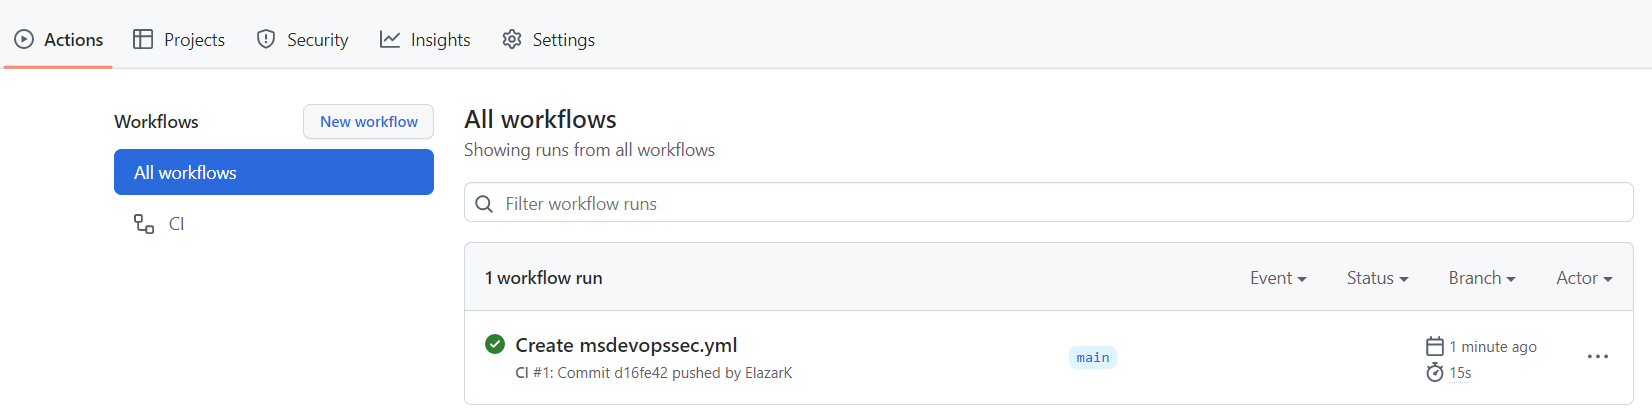
작업을 선택하고 새 작업이 실행 중인지 확인합니다.


검사 결과 보기
검사 결과를 보려면 다음을 수행합니다.
Azure에 로그인합니다.
클라우드용 Defender>로 이동하세요.
DevOps 보안 창에서 동일한 Microsoft Security DevOps(MSDO) 보안 결과를 확인할 수 있습니다. 개발자들은 관련 저장소의 CI 로그에서 이 결과를 몇 분 만에 확인할 수 있습니다. GitHub Advanced Security를 사용하는 고객은 이러한 도구에서 수집된 결과도 확인합니다.