Not
Bu sayfaya erişim yetkilendirme gerektiriyor. Oturum açmayı veya dizinleri değiştirmeyi deneyebilirsiniz.
Bu sayfaya erişim yetkilendirme gerektiriyor. Dizinleri değiştirmeyi deneyebilirsiniz.
Örnek sahipleri, kanıtlama akışı sırasında neyin doğrulanması gerektiğini tanımlamak için Azure Doğrulama ilkesini kullanabilir. Bu makalede kanıtlama hizmetinin ve ilke altyapısının çalışmalarına yer verilmiştir. Her kanıtlama türünün kendi kanıtlama ilkesi vardır. Desteklenen dil bilgisi ve işleme genel olarak aynıdır.
İlke sürümü 1.2
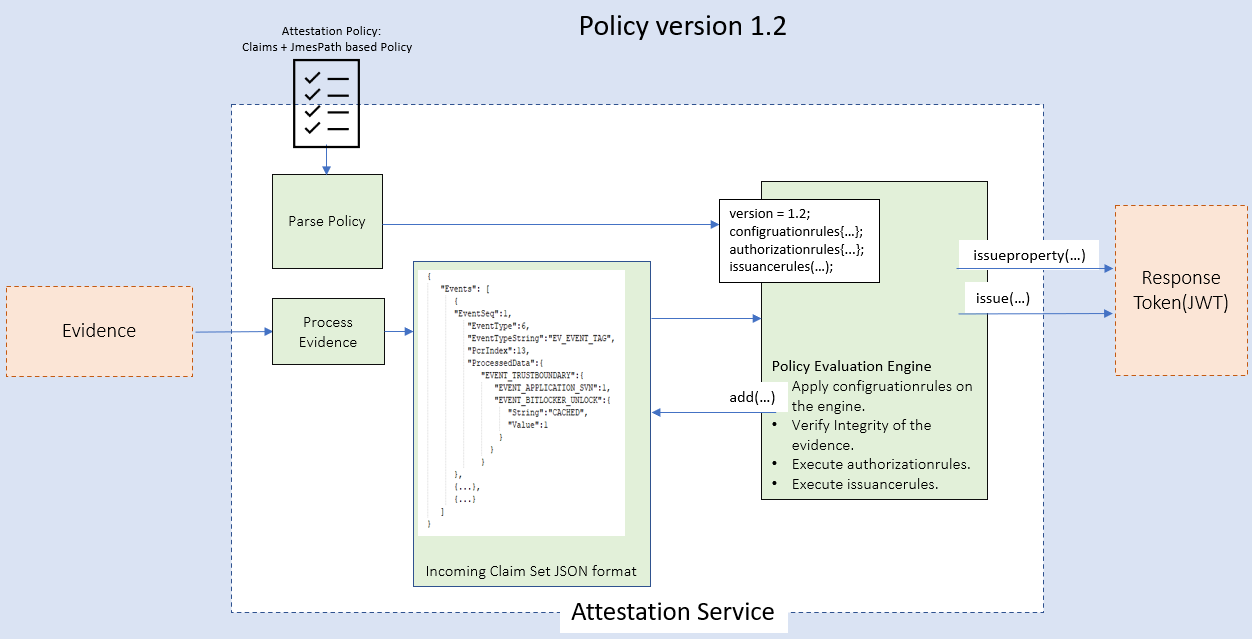
Kanıtlama akışı aşağıdaki gibidir:
- Platform, kanıtlama çağrısındaki kanıtlama kanıtını kanıtlama hizmetine gönderir.
- Kanıtlama hizmeti, kanıtı ayrıştırarak kanıtlama değerlendirmesinde kullanılan taleplerin listesini oluşturur. Ayrıca kanıt ayrıştırılır ve ilke yazıcısına daha geniş bir ölçü kümesi sağlamak için kullanılan bir JSON biçimi olarak korunur. Bu talepler mantıksal olarak gelen talep kümeleri olarak kategorilere ayrılmıştır.
- Kanıtlama hizmeti örneğinin sahibi tarafından karşıya yüklenen kanıtlama ilkesi daha sonra yanıtta talepleri değerlendirmek ve vermek için kullanılır. Artık kendi taleplerinizi ve sonraki talep kurallarınızı oluşturmak üzere kanıtta arama yapmak için JmesPath tabanlı sorguları kullanabilirsiniz. Değerlendirme sırasında yapılandırma kuralları, ilke değerlendirme altyapısına belirli taleplerin nasıl işleneceğini göstermek için de kullanılabilir.
İlke sürüm 1.2'nin dört segmenti vardır:
- version: Sürüm, dil bilgisinin sürüm numarasıdır.
- configurationrules: İlke değerlendirmesi sırasında bazen ilke altyapısının davranışını denetlemeniz gerekebilir. İlke değerlendirme altyapısına değerlendirmedeki bazı taleplerin nasıl işleneceğini göstermek için yapılandırma kurallarını kullanabilirsiniz.
- authorizationrules: Kanıtlamanın verme işlemlerine devam etmesi gerekip gerekmediğini belirlemek için önce denetlenen talep kuralları koleksiyonu. Verme kurallarının uygulanmasını gerektirmeyen çağrıları filtrelemek için bu bölümü kullanın. Bu bölümden yanıt belirtecine hiçbir talep verilemiyor. Bu kurallar kanıtlamanın başarısız olması için kullanılabilir.
- verme kuralları: İlkede tanımlandığı gibi kanıtlama sonucuna bilgi eklemek için değerlendirilen talep kuralları koleksiyonu. Talep kuralları tanımlanma sırasına göre uygulanır. Ayrıca isteğe bağlıdır. Bu kurallar, giden talep kümesine ve yanıt belirtecine eklemek için kullanılabilir. Bu kurallar kanıtlamayı başarısız yapmak için kullanılamaz.
İlke yazarı aşağıdaki yapılandırma kurallarını kullanabilir.
| Kanıtlama türü | ConfigurationRule özellik adı | Tür | Default value | Açıklama |
|---|---|---|---|---|
| Güvenilen Platform Modülü (TPM), sanallaştırma tabanlı güvenlik (VBS) | require_valid_aik_cert | Boole | true | Geçerli bir kanıtlama kimlik anahtarı sertifikasının gerekli olup olmadığını gösterir. Yalnızca TPM verileri mevcut olduğunda uygulanır. |
| TPM, VBS | required_pcr_mask | Int | 0xFFFFFF | TPM teklifine eklenmesi gereken PCR dizinleri için bit maskesi. Bit 0 PCR 0'ı, bit 1 ise PCR 1'i vb. temsil eder. |
Gelen taleplerin bir parçası olarak desteklenen taleplerin listesi
İlke sürümü 1.2, ilke dil bilgisinin işlevlerini de tanıtır. Talep kuralı işlevlerindeki işlevler hakkında daha fazla bilgi edinin. JmesPath tabanlı işlevlerin kullanıma sunulmasıyla, kanıtlama ilkesi yazarı tarafından gerektiğinde gelen talepler oluşturulabilir.
Talep oluşturmak için kullanabileceğiniz bazı temel kurallar burada listelenmiştir.
| Özellik | Açıklama | İlke kuralı |
|---|---|---|
| Güvenli önyükleme | Cihaz, yalnızca OEM tarafından güvenilen yazılımları kullanarak ön yüklemesini sağlar. | c:[type == "events", issuer=="AttestationService"] => add(type = "efiConfigVariables", value = JmesPath(c.value, "Events[?EventTypeString == 'EV_EFI_VARIABLE_DRIVER_CONFIG' && ProcessedData.VariableGuid == '8BE4DF61-93CA-11D2-AA0D-00E098032B8C']"));=> issue(type = "secureBootEnabled", value = JsonToClaimValue(JmesPath(c.value, "[?ProcessedData.UnicodeName == 'SecureBoot'] \| length(@) ==1 && @[0].ProcessedData.VariableData == 'AQ'"))); ![type=="secureBootEnabled", issuer=="AttestationPolicy"] => issue(type="secureBootEnabled", value=false); |
| Kod bütünlüğü | Kod bütünlüğü, sürücü veya sistem dosyasının belleğe her yüklendiğinde bütünlüğünü doğrulayan bir özelliktir. | // Retrieve bool properties c:[type=="events", issuer=="AttestationService"] => add(type="boolProperties", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && (PcrIndex ==12\|\| PcrIndex ==13\|\| PcrIndex ==19\|\| PcrIndex ==20)].ProcessedData.EVENT_TRUSTBOUNDARY"));c:[type=="boolProperties", issuer=="AttestationPolicy"] => add(type="codeIntegrityEnabledSet", value=JsonToClaimValue(JmesPath(c.value, "[*].EVENT_CODEINTEGRITY")));c:[type=="codeIntegrityEnabledSet", issuer=="AttestationPolicy"] => issue(type="codeIntegrityEnabled", value=ContainsOnlyValue(c.value, true));![type=="codeIntegrityEnabled", issuer=="AttestationPolicy"] => issue(type="codeIntegrityEnabled", value=false); |
| BitLocker [Önyükleme durumu] | Cihaz sürücülerini şifrelemek için kullanılır. | // Bitlocker Boot Status, The first non zero measurement or zero.c:[type=="events", issuer=="AttestationService"] => add(type="srtmDrtmEventPcr", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && (PcrIndex == 12\|\| PcrIndex ==19)].ProcessedData.EVENT_TRUSTBOUNDARY"));c:[type=="srtmDrtmEventPcr", issuer=="AttestationPolicy"] => issue(type="bitlockerStatus", value=JsonToClaimValue(JmesPath(c.value, "[*].EVENT_BITLOCKER_UNLOCK \| @[? Value != 0].Value \| @[0]")));![type=="bitlockerStatus"] => issue(type="bitlockerStatus", value=0); |
| Erken Başlatma Kötü Amaçlı Yazılımdan Koruma (ELAM) | ELAM, önyükleme sırasında imzalanmamış veya kötü amaçlı sürücülerin yüklenmesine karşı koruma sağlar. | // Elam Driver (windows defender) Loaded.c:[type=="events", issuer=="AttestationService"] => add(type="boolProperties", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && (PcrIndex == 12\|\| PcrIndex ==13\|\| PcrIndex ==19\|\| PcrIndex ==20)].ProcessedData.EVENT_TRUSTBOUNDARY"));c:[type=="boolProperties", issuer=="AttestationPolicy"] => issue(type="elamDriverLoaded", value=JsonToClaimValue(JmesPath(c.value, "[*].EVENT_LOADEDMODULE_AGGREGATION[] \| [? EVENT_IMAGEVALIDATED == true&& (equals_ignore_case(EVENT_FILEPATH, '\\windows\\system32\\drivers\\wdboot.sys') \|\| equals_ignore_case(EVENT_FILEPATH, '\\windows\\system32\\drivers\\wd\\wdboot.sys'))] \| @ !=null")));![type=="elamDriverLoaded", issuer=="AttestationPolicy"] => issue(type="elamDriverLoaded", value=false); |
| Önyükleme hata ayıklaması | Kullanıcının bir önyükleme hata ayıklayıcısına bağlanmasına izin verir. Güvenli önyükleme ve diğer önyükleme korumalarını atlamak için kullanılabilir. | // Boot debuggingc:[type=="events", issuer=="AttestationService"] => add(type="boolProperties", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && (PcrIndex == 12\|\| PcrIndex ==13\|\| PcrIndex ==19\|\| PcrIndex ==20)].ProcessedData.EVENT_TRUSTBOUNDARY"));c:[type=="boolProperties", issuer=="AttestationPolicy"] => add(type="bootDebuggingEnabledSet", value=JsonToClaimValue(JmesPath(c.value, "[*].EVENT_BOOTDEBUGGING")));c:[type=="bootDebuggingEnabledSet", issuer=="AttestationPolicy"] => issue(type="bootDebuggingDisabled", value=ContainsOnlyValue(c.value, false));![type=="bootDebuggingDisabled", issuer=="AttestationPolicy"] => issue(type="bootDebuggingDisabled", value=false); |
| Çekirdek hata ayıklaması | Kullanıcının çekirdek hata ayıklayıcısını bağlamasına izin verir. Tüm sistem kaynaklarına erişim verir (daha az sanallaştırma tabanlı güvenlik [VBS] korumalı kaynaklar). | // Kernel Debuggingc:[type=="events", issuer=="AttestationService"] => add(type="boolProperties", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && (PcrIndex == 12\|\| PcrIndex ==13\|\| PcrIndex ==19\|\| PcrIndex ==20)].ProcessedData.EVENT_TRUSTBOUNDARY"));c:[type=="boolProperties", issuer=="AttestationPolicy"] => add(type="osKernelDebuggingEnabledSet", value=JsonToClaimValue(JmesPath(c.value, "[*].EVENT_OSKERNELDEBUG")));c:[type=="osKernelDebuggingEnabledSet", issuer=="AttestationPolicy"] => issue(type="osKernelDebuggingDisabled", value=ContainsOnlyValue(c.value, false));![type=="osKernelDebuggingDisabled", issuer=="AttestationPolicy"] => issue(type="osKernelDebuggingDisabled", value=false); |
| Veri Yürütme Engelleme (DEP) ilkesi | DEP ilkesi, kötü amaçlı kodun sistemde çalışmasını önlemeye yardımcı olmak için bellek üzerinde ek denetimler gerçekleştiren bir dizi donanım ve yazılım teknolojisidir. | // DEP Policyc:[type=="events", issuer=="AttestationService"] => add(type="boolProperties", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && (PcrIndex == 12\|\| PcrIndex ==13\|\| PcrIndex ==19\|\| PcrIndex ==20)].ProcessedData.EVENT_TRUSTBOUNDARY"));c:[type=="boolProperties", issuer=="AttestationPolicy"] => issue(type="depPolicy", value=JsonToClaimValue(JmesPath(c.value, "[*].EVENT_DATAEXECUTIONPREVENTION.Value \| @[-1]")));![type=="depPolicy"] => issue(type="depPolicy", value=0); |
| Test ve uçuş imzalama | Kullanıcının testle imzalanan kodu çalıştırmasını sağlar. | // Test Signing c:[type=="events", issuer=="AttestationService"] => add(type="boolProperties", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && (PcrIndex == 12\|\| PcrIndex ==13\|\| PcrIndex ==19\|\| PcrIndex ==20)].ProcessedData.EVENT_TRUSTBOUNDARY")); c:[type=="boolProperties", issuer=="AttestationPolicy"] => add(type="testSigningEnabledSet", value=JsonToClaimValue(JmesPath(c.value, "[*].EVENT_TESTSIGNING"))); c:[type=="testSigningEnabledSet", issuer=="AttestationPolicy"] => issue(type="testSigningDisabled", value=ContainsOnlyValue(c.value, false)); ![type=="testSigningDisabled", issuer=="AttestationPolicy"] => issue(type="testSigningDisabled", value=false);//Flight Signingc:[type=="boolProperties", issuer=="AttestationPolicy"] => add(type="flightSigningEnabledSet", value=JsonToClaimValue(JmesPath(c.value, "\[\*\].EVENT_FLIGHTSIGNING")));c:[type=="flightSigningEnabledSet", issuer=="AttestationPolicy"] => issue(type="flightSigningNotEnabled", value=ContainsOnlyValue(c.value, false));![type=="flightSigningNotEnabled", issuer=="AttestationPolicy"] => issue(type="flightSigningNotEnabled", value=false); |
| Sanal Güvenli Mod/VBS | VBS, önemli sistem ve işletim sistemi kaynaklarını ve kimlik bilgilerini korumak için kullanılan bu sanal güvenli modu oluşturmak için Windows hiper yöneticisini kullanır. | // VSM enabled c:[type=="events", issuer=="AttestationService"] => add(type="srtmDrtmEventPcr", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && (PcrIndex ==12\|\| PcrIndex ==19)].ProcessedData.EVENT_TRUSTBOUNDARY"));c:[type=="srtmDrtmEventPcr", issuer=="AttestationPolicy"] => add(type="vsmEnabledSet", value=JsonToClaimValue(JmesPath(c.value, "\[\*\].EVENT_VBS_VSM_REQUIRED")));c:[type=="srtmDrtmEventPcr", issuer=="AttestationPolicy"] => add(type="vsmEnabledSet", value=JsonToClaimValue(JmesPath(c.value, "[*].EVENT_VBS_MANDATORY_ENFORCEMENT")));c:[type=="vsmEnabledSet", issuer=="AttestationPolicy"] => issue(type="vsmEnabled", value=ContainsOnlyValue(c.value, true));![type=="vsmEnabled", issuer=="AttestationPolicy"] => issue(type="vsmEnabled", value=false);c:[type=="vsmEnabled", issuer=="AttestationPolicy"] => issue(type="vbsEnabled", value=c.value); |
| Hiper yönetici korumalı kod bütünlüğü (HVCI) | HVCI, bir sistem dosyasının belleğe her yüklendiğinde bütünlüğünü doğrulayan bir özelliktir. | // HVCIc:[type=="events", issuer=="AttestationService"] => add(type="srtmDrtmEventPcr", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && (PcrIndex == 12\|\| PcrIndex ==19)].ProcessedData.EVENT_TRUSTBOUNDARY"));c:[type=="srtmDrtmEventPcr", issuer=="AttestationPolicy"] => add(type="hvciEnabledSet", value=JsonToClaimValue(JmesPath(c.value, "[*].EVENT_VBS_HVCI_POLICY \| @[?String == 'HypervisorEnforcedCodeIntegrityEnable'].Value")));c:[type=="hvciEnabledSet", issuer=="AttestationPolicy"] => issue(type="hvciEnabled", value=ContainsOnlyValue(c.value, 1));![type=="hvciEnabled", issuer=="AttestationPolicy"] => issue(type="hvciEnabled", value=false); |
| Giriş-çıkış bellek yönetim birimi (IOMMU) | IOMMU, Doğrudan bellek erişimi özellikli cihaz çevre birimleri için sanalı fiziksel bellek adreslerine çevirir. IOMMU hassas bellek bölgelerini korur. | // IOMMUc:[type=="events", issuer=="AttestationService"] => add(type="boolProperties", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && (PcrIndex == 12\|\| PcrIndex ==13\|\| PcrIndex ==19\|\| PcrIndex ==20)].ProcessedData.EVENT_TRUSTBOUNDARY"));c:[type=="boolProperties", issuer=="AttestationPolicy"] => add(type="iommuEnabledSet", value=JsonToClaimValue(JmesPath(c.value, "[*].EVENT_VBS_IOMMU_REQUIRED")));c:[type=="iommuEnabledSet", issuer=="AttestationPolicy"] => issue(type="iommuEnabled", value=ContainsOnlyValue(c.value, true));![type=="iommuEnabled", issuer=="AttestationPolicy"] => issue(type="iommuEnabled", value=false); |
| PCR değer değerlendirmesi | PCR'ler önyükleme sırasında yapılan bileşenlerin ölçümlerini içerir. Bu ölçümler, bileşenleri altın veya bilinen ölçümlere karşı doğrulamak için kullanılabilir. | //PCRS are only read-only and thus cannot be used with issue operation, but they can be used to validate expected/golden measurements.c:[type == "pcrs", issuer=="AttestationService"] && c1:[type=="pcrMatchesExpectedValue", value==JsonToClaimValue(JmesPath(c.value, "PCRs[? Index == 0].Digests.SHA1 \| @[0] == "KCk6Ow""))] => issue(claim = c1); |
| Önyükleme Yöneticisi sürümü | Test edilen cihazda ilk önyükleme sırasında yüklenen Önyükleme Yöneticisi'nin güvenlik sürümü numarası. | // Find the first EVENT_APPLICATION_SVN. That value is the Boot Manager SVN// Find the first EV_SEPARATOR in PCR 12, 13, Or 14c:[type=="events", issuer=="AttestationService"] => add(type="evSeparatorSeq", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_SEPARATOR' && (PcrIndex == 12\|\| PcrIndex ==13\|\| PcrIndex ==14)] \| @[0].EventSeq"));c:[type=="evSeparatorSeq", value != "null", issuer=="AttestationPolicy"] => add(type="beforeEvSepClause", value=AppendString(AppendString("Events[? EventSeq < ", c.value), ""));[type=="evSeparatorSeq", value=="null", issuer=="AttestationPolicy"] => add(type="beforeEvSepClause", value="Events[? true ");// Find the first EVENT_APPLICATION_SVN. That value is the Boot Manager SVNc:[type=="beforeEvSepClause", issuer=="AttestationPolicy"] => add(type="bootMgrSvnSeqQuery", value=AppendString(c.value, " && EventTypeString == 'EV_EVENT_TAG' && PcrIndex == 12 && ProcessedData.EVENT_TRUSTBOUNDARY.EVENT_APPLICATION_SVN] \| @[0].EventSeq"));c1:[type=="bootMgrSvnSeqQuery", issuer=="AttestationPolicy"] && c2:[type=="events", issuer=="AttestationService"] => add(type="bootMgrSvnSeq", value=JmesPath(c2.value, c1.value));c:[type=="bootMgrSvnSeq", value!="null", issuer=="AttestationPolicy"] => add(type="bootMgrSvnQuery", value=AppendString(AppendString("Events[? EventSeq == ", c.value), "].ProcessedData.EVENT_TRUSTBOUNDARY.EVENT_APPLICATION_SVN \| @[0]"));c1:[type=="bootMgrSvnQuery", issuer=="AttestationPolicy"] && c2:[type=="events", issuer=="AttestationService"] => issue(type="bootMgrSvn", value=JsonToClaimValue(JmesPath(c2.value, c1.value))); |
| Güvenli mod | Güvenli mod, windows için bilgisayarınızı sınırlı bir durumda başlatan bir sorun giderme seçeneğidir. Yalnızca Windows'u çalıştırmak için gereken temel dosyalar ve sürücüler başlatılır. | // Safe modec:[type=="events", issuer=="AttestationService"] => add(type="boolProperties", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && (PcrIndex == 12\|\| PcrIndex ==13\|\| PcrIndex ==19\|\| PcrIndex ==20)].ProcessedData.EVENT_TRUSTBOUNDARY"));c:[type=="boolProperties", issuer=="AttestationPolicy"] => add(type="safeModeEnabledSet", value=JsonToClaimValue(JmesPath(c.value, "[*].EVENT_SAFEMODE")));c:[type=="safeModeEnabledSet", issuer=="AttestationPolicy"] => issue(type="notSafeMode", value=ContainsOnlyValue(c.value, false));![type=="notSafeMode", issuer=="AttestationPolicy"] => issue(type="notSafeMode", value=true); |
| WinPE önyüklemesi | Windows yükleme öncesi Ortamı (Windows PE), bir bilgisayarı Windows yüklemesine hazırlamak, bir ağ dosya sunucusundan disk görüntülerini kopyalamak ve Windows kurulumunu başlatmak için kullanılan sınırlı hizmetlere sahip en düşük düzeyde bir işletim sistemidir. | // Win PEc:[type=="events", issuer=="AttestationService"] => add(type="boolProperties", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && (PcrIndex == 12\|\| PcrIndex ==13\|\| PcrIndex ==19\|\| PcrIndex ==20)].ProcessedData.EVENT_TRUSTBOUNDARY"));c:[type=="boolProperties", issuer=="AttestationPolicy"] => add(type="winPEEnabledSet", value=JsonToClaimValue(JmesPath(c.value, "\[\*\].EVENT_WINPE")));c:[type=="winPEEnabledSet", issuer=="AttestationPolicy"] => issue(type="notWinPE", value=ContainsOnlyValue(c.value, false));![type=="notWinPE", issuer=="AttestationPolicy"] => issue(type="notWinPE", value=true); |
| Kod bütünlüğü (CI) ilkesi | Önyükleme ortamının güvenliğini denetleen CI ilkesinin karması. | // CI Policyc :[type=="events", issuer=="AttestationService"] => issue(type="codeIntegrityPolicy", value=JsonToClaimValue(JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && PcrIndex == 13].ProcessedData.EVENT_TRUSTBOUNDARY.EVENT_SI_POLICY[].RawData"))); |
| Güvenli Önyükleme Yapılandırma İlkesi Karması (SBCPHash) | SBCPHash, bilgisayarlar dışında Windows cihazlarında önyükleme sırasında yüklenen Özel SBCP'nin parmak izidir. | // Secure Boot Custom Policyc:[type=="events", issuer=="AttestationService"] => issue(type="secureBootCustomPolicy", value=JsonToClaimValue(JmesPath(c.value, "Events[? EventTypeString == 'EV_EFI_VARIABLE_DRIVER_CONFIG' && PcrIndex == 7 && ProcessedData.UnicodeName == 'CurrentPolicy' && ProcessedData.VariableGuid == '77FA9ABD-0359-4D32-BD60-28F4E78F784B'].ProcessedData.VariableData \| @[0]"))); |
| System Guard (DRTM Doğrulama ve SMM Düzeyleri) | Önyükleme sırasında System Guard'ın doğrulandığından ve buna karşılık gelen Sistem Yönetim Modu Düzeyi'nin doğrulandığından emin olun | // Extract the DRTM state auth event.// The rule attempts to find the valid DRTM state auth event by applying following conditions:// 1. There is only one DRTM state auth event in the events log// 2. The EVENT_DRTM_STATE_AUTH.SignatureValid field in the DRTM state auth event is set to truec:[type=="events", issuer=="AttestationService"] => add(type="validDrtmStateAuthEvent", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && PcrIndex ==20 && ProcessedData.EVENT_TRUSTBOUNDARY.EVENT_DRTM_STATE_AUTH.SignatureValid !=null] \| length(@) == 1 && @[0] \| @.{EventSeq:EventSeq, SignatureValid:ProcessedData.EVENT_TRUSTBOUNDARY.EVENT_DRTM_STATE_AUTH.SignatureValid}")); // Check if Signature is valid in extracted state auth eventsc:[type=="validDrtmStateAuthEvent", issuer=="AttestationPolicy"] => issue(type="drtmMleValid", value=JsonToClaimValue(JmesPath(c.value, "SignatureValid")));![type=="drtmMleValid", issuer=="AttestationPolicy"] => issue(type="drtmMleValid", value=false);// Get the sequence number of the DRTM state auth event.// The sequence number is used to ensure that the SMM event appears before the last DRTM state auth event.[type=="drtmMleValid", value==true, issuer=="AttestationPolicy"] && c:[type=="validDrtmStateAuthEvent", issuer=="AttestationPolicy"] => add(type="validDrtmStateAuthEventSeq", value=JmesPath(c.value, "EventSeq")); // Create query for SMM event// The query is constructed to find the SMM level from the SMM level event that appears exactly once before the valid DRTM state auth event in the event log[type=="drtmMleValid", value==true, issuer=="AttestationPolicy"] && c:[type=="validDrtmStateAuthEventSeq", issuer=="AttestationPolicy"] => add(type="smmQuery", value=AppendString(AppendString("Events[? EventTypeString == 'EV_EVENT_TAG' && PcrIndex == 20 && EventSeq <", c.value), "].ProcessedData.EVENT_DRTM_SMM \| length(@) == 1 && @[0] \| @.Value"));// Extract SMM value[type=="drtmMleValid", value==true, issuer=="AttestationPolicy"] && c1:[type=="smmQuery", issuer=="AttestationPolicy"] && c2:[type=="events", issuer=="AttestationService"] => issue(type="smmLevel", value=JsonToClaimValue(JmesPath(c2.value, c1.value))); |
| Önyükleme uygulaması alt sürüm | Cihazda çalışan Önyükleme Yöneticisi sürümü. | // Find the first EV_SEPARATOR in PCR 12, 13, Or 14, the ordering of the events is critical to ensure correctness.c:[type=="events", issuer=="AttestationService"] => add(type="evSeparatorSeq", value=JmesPath(c.value, "Events[? EventTypeString == 'EV_SEPARATOR' && (PcrIndex == 12\|\| PcrIndex ==13\|\| PcrIndex ==14)] \| @[0].EventSeq"));c:[type=="evSeparatorSeq", value != "null", issuer=="AttestationPolicy"] => add(type="beforeEvSepClause", value=AppendString(AppendString("Events[? EventSeq < ", c.value), ""));[type=="evSeparatorSeq", value=="null", issuer=="AttestationPolicy"] => add(type="beforeEvSepClause", value="Events[? true ");// No restriction of EV_SEPARATOR in case it is not present// Find the first EVENT_TRANSFER_CONTROL with value 1 or 2 in PCR 12 that is before the EV_SEPARATORc1:[type=="beforeEvSepClause", issuer=="AttestationPolicy"] && c2:[type=="bootMgrSvnSeq", value != "null", issuer=="AttestationPolicy"] => add(type="beforeEvSepAfterBootMgrSvnClause", value=AppendString(AppendString(AppendString(c1.value, "&& EventSeq >="), c2.value), ""));c:[type=="beforeEvSepAfterBootMgrSvnClause", issuer=="AttestationPolicy"] => add(type="tranferControlQuery", value=AppendString(c.value, " && EventTypeString == 'EV_EVENT_TAG' && PcrIndex == 12&& (ProcessedData.EVENT_TRUSTBOUNDARY.EVENT_TRANSFER_CONTROL.Value == 1\|\| ProcessedData.EVENT_TRUSTBOUNDARY.EVENT_TRANSFER_CONTROL.Value ==2)] \| @[0].EventSeq"));c1:[type=="tranferControlQuery", issuer=="AttestationPolicy"] && c2:[type=="events", issuer=="AttestationService"] => add(type="tranferControlSeq", value=JmesPath(c2.value, c1.value));// Find the first non-null EVENT_MODULE_SVN in PCR 13 after the transfer control.c:[type=="tranferControlSeq", value!="null", issuer=="AttestationPolicy"] => add(type="afterTransferCtrlClause", value=AppendString(AppendString(" && EventSeq > ", c.value), ""));c1:[type=="beforeEvSepClause", issuer=="AttestationPolicy"] && c2:[type=="afterTransferCtrlClause", issuer=="AttestationPolicy"] => add(type="moduleQuery", value=AppendString(AppendString(c1.value, c2.value), " && EventTypeString == 'EV_EVENT_TAG' && PcrIndex == 13 && ((ProcessedData.EVENT_TRUSTBOUNDARY.EVENT_LOADEDMODULE_AGGREGATION[].EVENT_MODULE_SVN \| @[0]) \|\| (ProcessedData.EVENT_LOADEDMODULE_AGGREGATION[].EVENT_MODULE_SVN \| @[0]))].EventSeq \| @[0]"));c1:[type=="moduleQuery", issuer=="AttestationPolicy"] && c2:[type=="events", issuer=="AttestationService"] => add(type="moduleSeq", value=JmesPath(c2.value, c1.value));// Find the first EVENT_APPLICATION_SVN after EV_EVENT_TAG in PCR 12. That value is Boot App SVNc:[type=="moduleSeq", value!="null", issuer=="AttestationPolicy"] => add(type="applicationSvnAfterModuleClause", value=AppendString(AppendString(" && EventSeq > ", c.value), ""));c1:[type=="beforeEvSepClause", issuer=="AttestationPolicy"] && c2:[type=="applicationSvnAfterModuleClause", issuer=="AttestationPolicy"] => add(type="bootAppSvnQuery", value=AppendString(AppendString(c1.value, c2.value), " && EventTypeString == 'EV_EVENT_TAG' && PcrIndex == 12].ProcessedData.EVENT_TRUSTBOUNDARY.EVENT_APPLICATION_SVN \| @[0]"));c1:[type=="bootAppSvnQuery", issuer=="AttestationPolicy"] && c2:[type=="events", issuer=="AttestationService"] => issue(type="bootAppSvn", value=JsonToClaimValue(JmesPath(c2.value, c1.value))); |
| Önyükleme düzeltme listesi | Cihazın etkinliklerini daha fazla izlemek için cihazı kurumsal bir bal deposuna yönlendirmek için kullanılan önyükleme düzeltme listesi. | // Boot Rev List Info c:[type=="events", issuer=="AttestationService"] => issue(type="bootRevListInfo", value=JsonToClaimValue(JmesPath(c.value, "Events[? EventTypeString == 'EV_EVENT_TAG' && PcrIndex == 13].ProcessedData.EVENT_TRUSTBOUNDARY.EVENT_BOOT_REVOCATION_LIST.RawData \| @[0]"))); |
1.2 sürümünü kullanan TPM kanıtlama için örnek ilkeler
version=1.2;

authorizationrules {
    => permit();
};


issuancerules
{

// Verify if secure boot is enabled.
c:[type == "events", issuer=="AttestationService"] => add(type = "efiConfigVariables", value = JmesPath(c.value, "Events[?EventTypeString == 'EV_EFI_VARIABLE_DRIVER_CONFIG' && ProcessedData.VariableGuid == '8BE4DF61-93CA-11D2-AA0D-00E098032B8C']"));

c:[type=="efiConfigVariables", issuer=="AttestationPolicy"]=> add(type = "secureBootEnabled", value = JsonToClaimValue(JmesPath(c.value, "[?ProcessedData.UnicodeName == 'SecureBoot'] | length(@) == `1` && @[0].ProcessedData.VariableData == 'AQ'")));
![type=="secureBootEnabled", issuer=="AttestationPolicy"] => add(type="secureBootEnabled", value=false);

//Verify if Defender ELAM is loaded.
c:[type=="boolProperties", issuer=="AttestationPolicy"] => add(type="elamDriverLoaded", value=JsonToClaimValue(JmesPath(c.value, "[*].EVENT_LOADEDMODULE_AGGREGATION[] | [? EVENT_IMAGEVALIDATED == `true` && (equals_ignore_case(EVENT_FILEPATH, '\\windows\\system32\\drivers\\wdboot.sys') || equals_ignore_case(EVENT_FILEPATH, '\\windows\\system32\\drivers\\wd\\wdboot.sys'))] | @ != `null`")));
[type=="elamDriverLoaded", issuer=="AttestationPolicy"] => add(type="WindowsDefenderElamDriverLoaded", value=true);
![type=="elamDriverLoaded", issuer=="AttestationPolicy"] => add(type="WindowsDefenderElamDriverLoaded", value=false);

[type=="WindowsDefenderElamDriverLoaded", value==true] &&
[type=="secureBootEnabled", value==true] => issue("PlatformAttested", value=true);

};