Microsoft Security | Microsoft Entra | Microsoft Entra ID
A cloud-based identity and access management service for securing user authentication and resource access

This browser is no longer supported.
Upgrade to Microsoft Edge to take advantage of the latest features, security updates, and technical support.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EKC%3C/text%3E%3C/svg%3E)
Hi
The security team approached us to provide them with logs for a device that an Admin wiped on Azure Endpoint.
We used the Tenant Admin Logs to search for the event by date and action, but couldn't correlate it to a specific device since the log event does not include the Device ID.
We tried to search for the event from the Admin logs that we are downloading daily from Azure Graph API but it seems that the wipe activity is not being logged there.
Is there a way to find out the device ID from the Tenant Admin Logs in the case of a wipe event?
A cloud-based identity and access management service for securing user authentication and resource access
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ESM%3C/text%3E%3C/svg%3E)
Hi @Kristian Cardona ,
Just checking in to see if the below answer helped. If this answers your query, please don’t forget to click "Accept the answer" and Up-Vote for the same, which might be beneficial to other community members reading this thread. And, if you have any further query do let us know.
Thanks,
Shweta
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EK%3C/text%3E%3C/svg%3E)
Exactly. We only have the ObjectId or the DeviceId, but after the wipe they no longer exist, so they’re useless.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EDK%3C/text%3E%3C/svg%3E)
Why are the Computer Name, Serial Number or the MAC-Address of the LAN Adapter missing in the the Log? This doesn´t help me at all.
Hello @Kristian Cardona
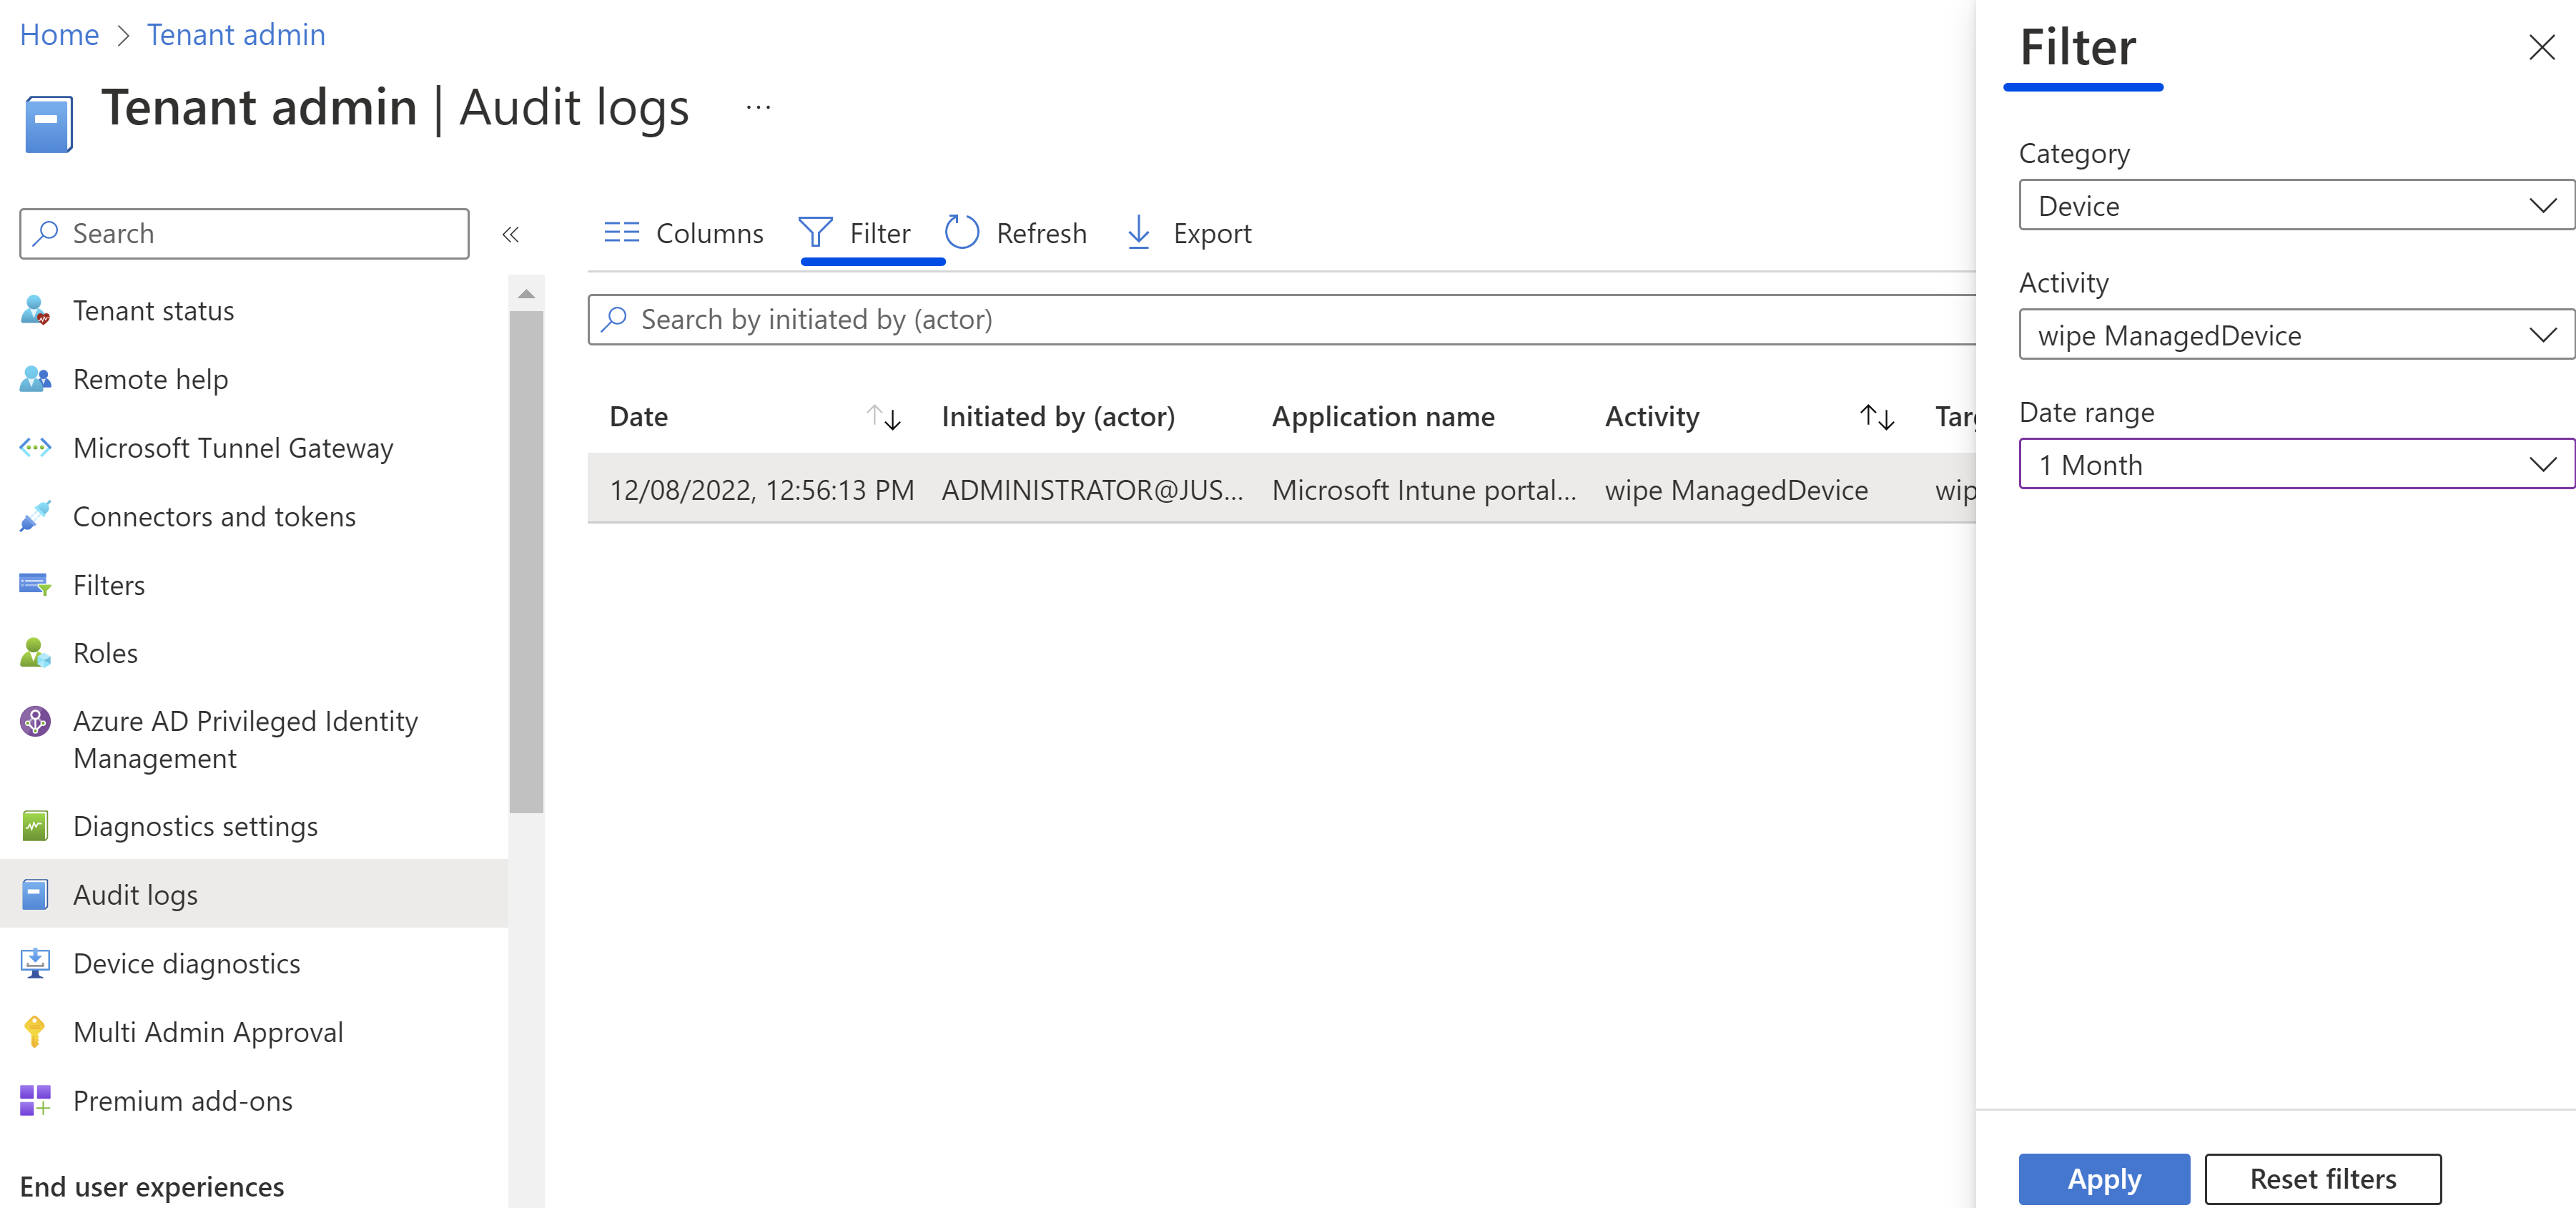
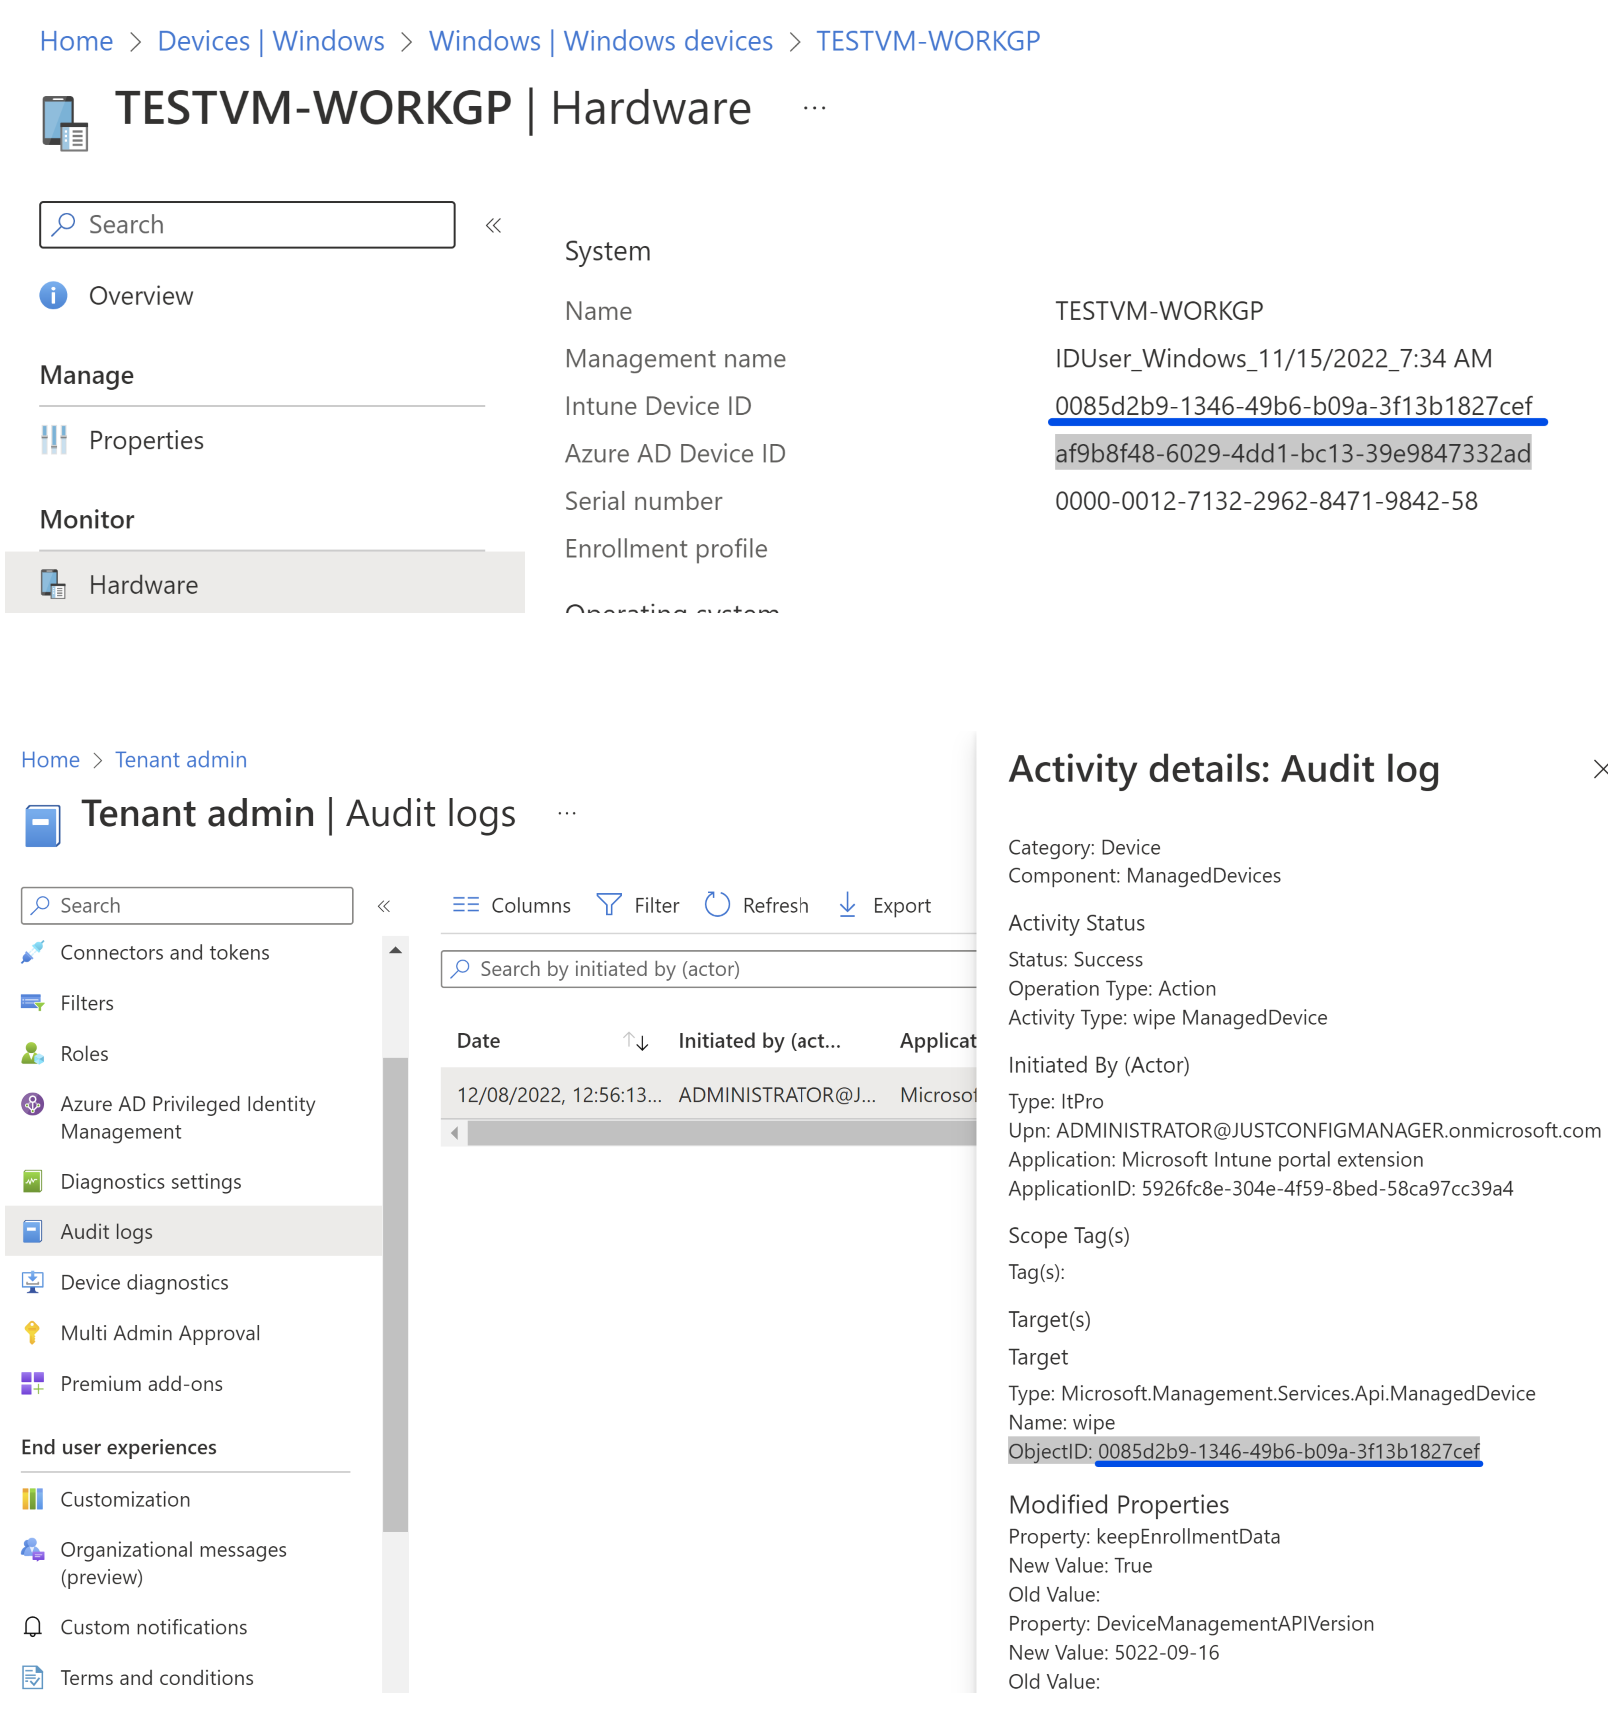
Please do let me know if you have any queries in the comments section.
Thanks,
Akshay Kaushik
Please "Accept the answer", "Upvote" and rate your experience if the suggestion works as per your business need. This will help us and others in the community as well.
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3EAK%3C/text%3E%3C/svg%3E)
Hello Akshay,
Hope you are well.
I am in this position now too. Thing is right, when you wipe a device, you will not have it under devices in Intune nor Entra so that means you cannot connect the dots of what device specifically was deleted based on the object ID because that object doesn't exist in your tenant anymore
' cx='32' cy='32' r='32' /%3E%3Ctext x='50%25' y='55%25' dominant-baseline='middle' text-anchor='middle' fill='%23FFF' %3ESG%3C/text%3E%3C/svg%3E)
Thank you for posting this in Microsoft Q&A platform.
You can look at the Azure AD audit logs to get more information about the device and time stamp of delete operation.
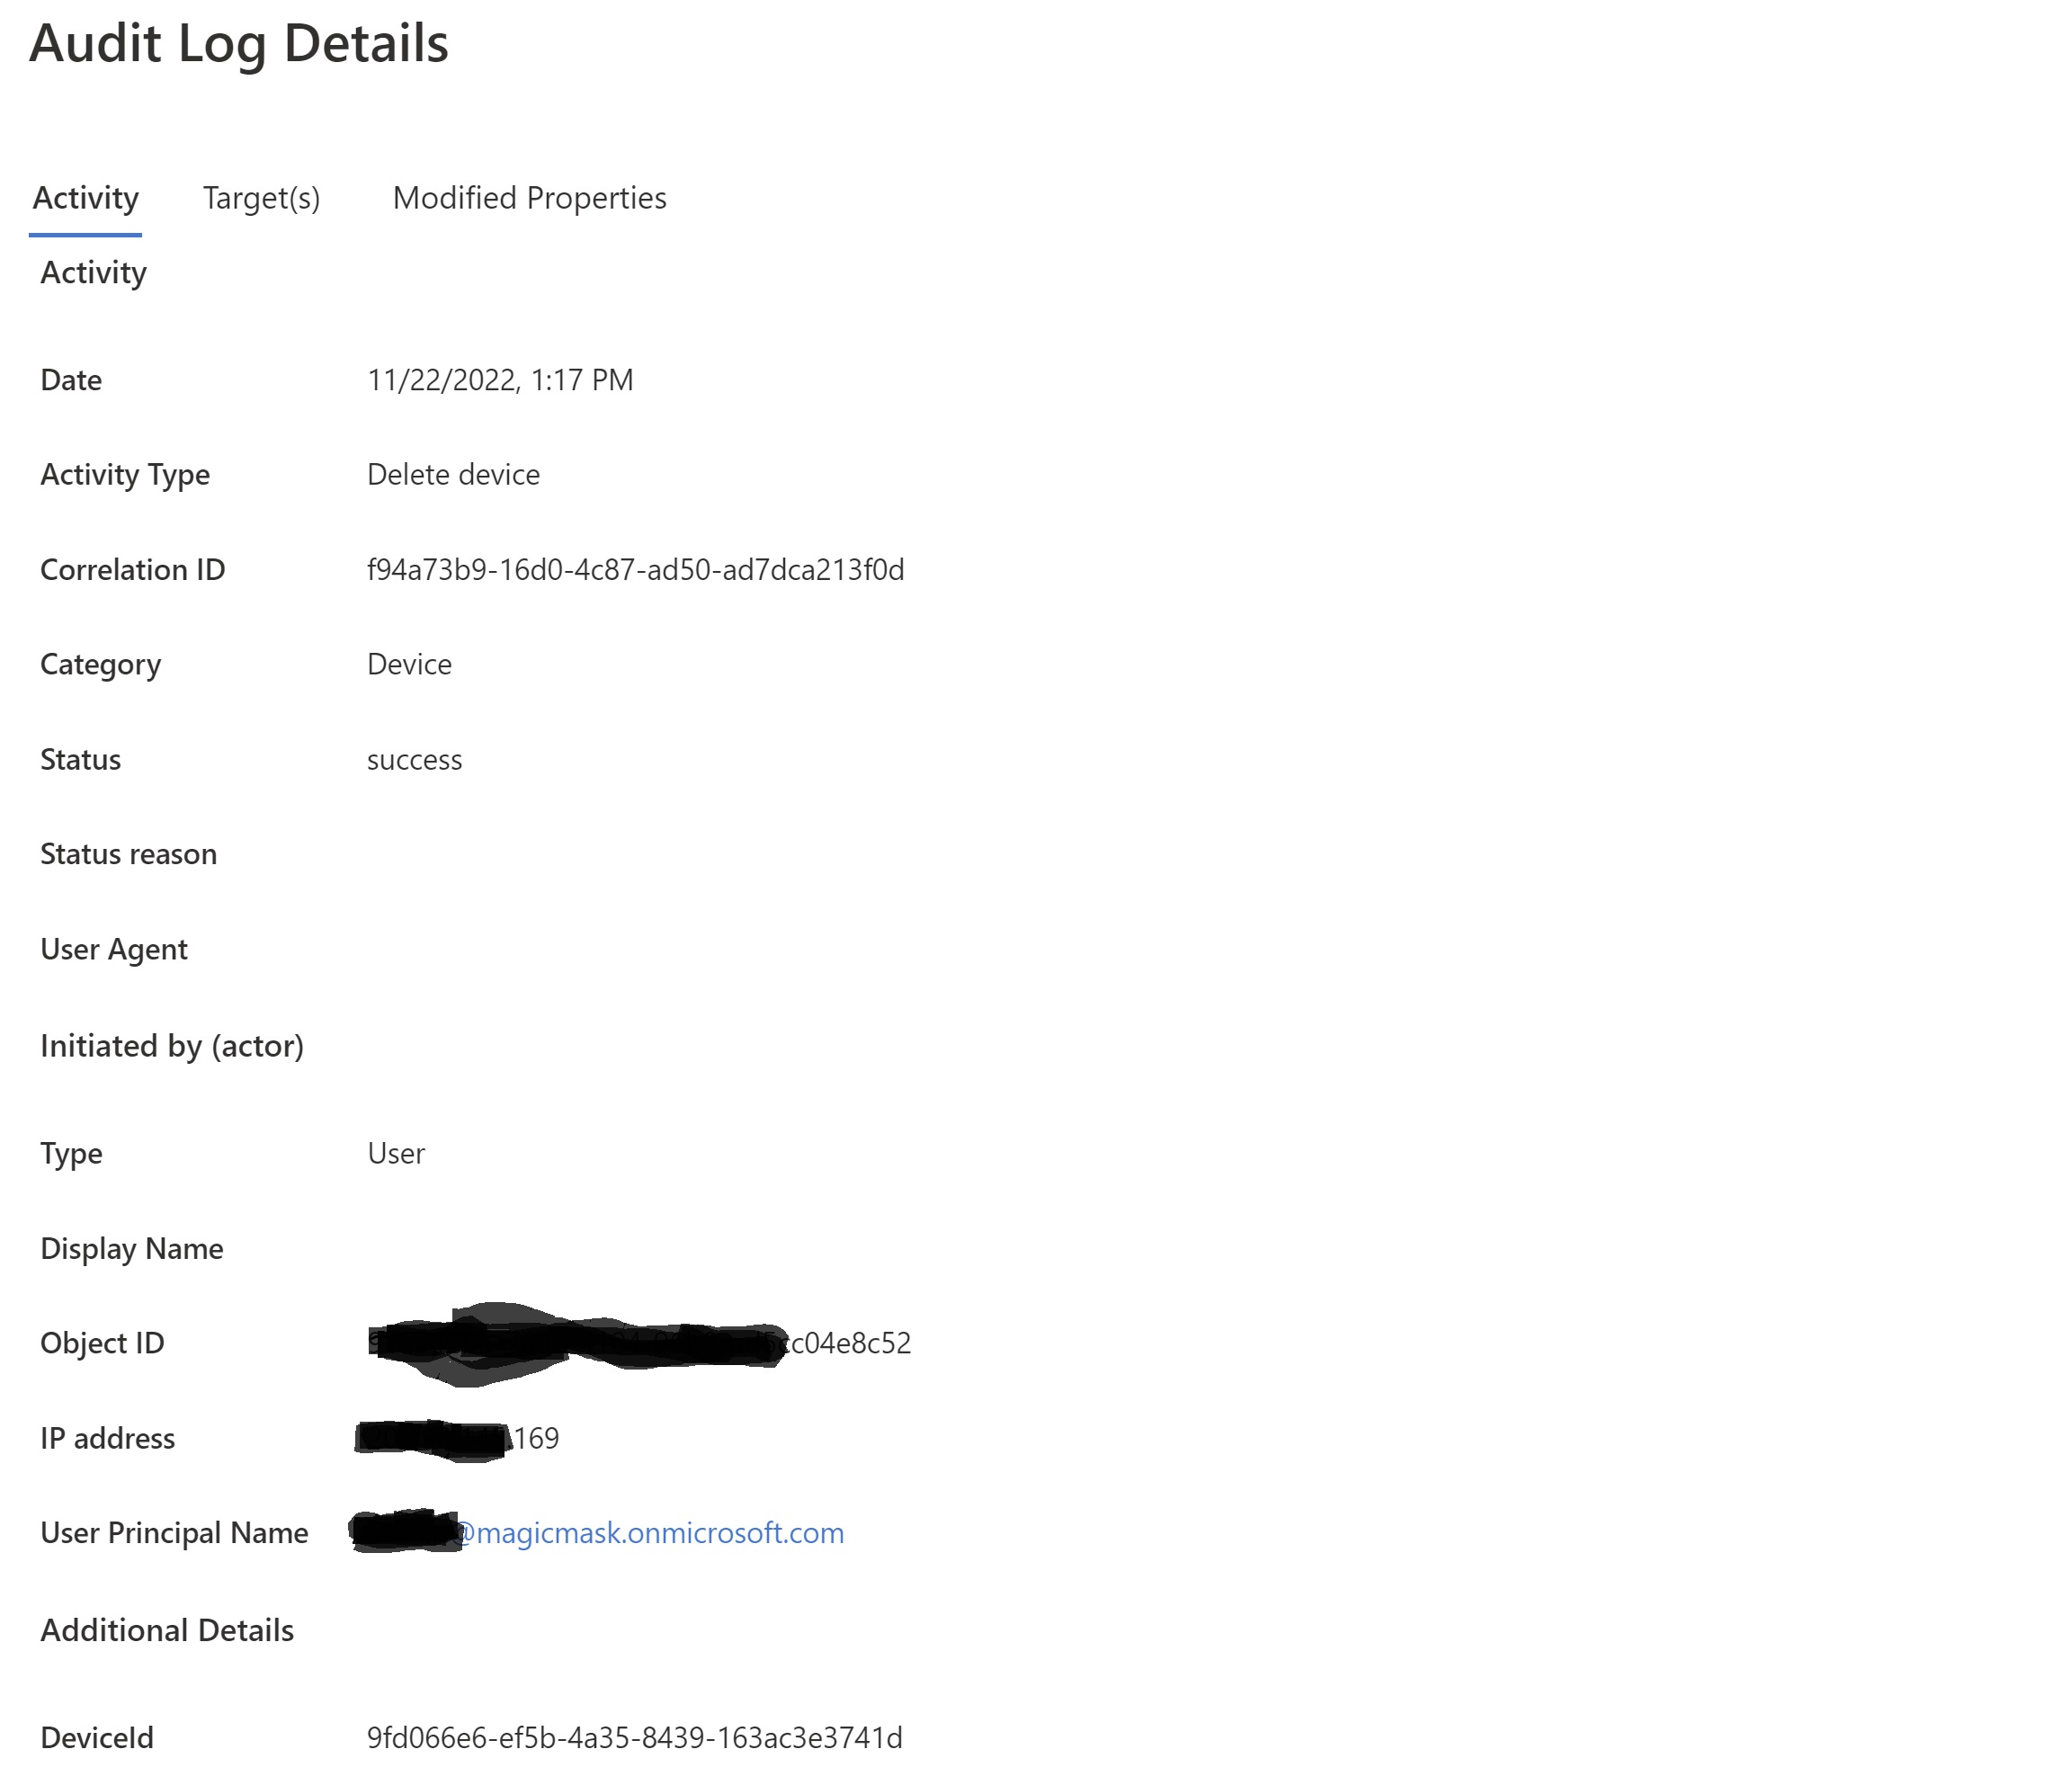
Do let me know if this answers your question.
Please "Accept the answer" if the information helped you. This will help us and others in the community as well.
thanks for your reply, the issue is with an audit trail for Wiped devices not deleted devices, unfortunately.
Wipe logs cannot be found as per your advice
Currently we do not have a feature to get the logs for wiped devices. However, you can submit for feedback in Azure feedback portal. This portal is directly monitored by our PM's. You can get response from them regarding this if this feature is planned for near future.
https://feedback.azure.com/d365community/forum/22920db1-ad25-ec11-b6e6-000d3a4f0789
Do let me know if you have any further questions
Please "Accept the answer" if the information helped you. This will help us and others in the community as well.