Note
Access to this page requires authorization. You can try signing in or changing directories.
Access to this page requires authorization. You can try changing directories.
In this article, you learn how to integrate Image Relay with Microsoft Entra ID. When you integrate Image Relay with Microsoft Entra ID, you can:
- Control in Microsoft Entra ID who has access to Image Relay.
- Enable your users to be automatically signed-in to Image Relay with their Microsoft Entra accounts.
- Manage your accounts in one central location.
Prerequisites
The scenario outlined in this article assumes that you already have the following prerequisites:
- A Microsoft Entra user account with an active subscription. If you don't already have one, you can Create an account for free.
- One of the following roles:
- Image Relay single sign-on (SSO) enabled subscription.
Scenario description
In this article, you configure and test Microsoft Entra single sign-on in a test environment.
- Image Relay supports SP initiated SSO.
Add Image Relay from the gallery
To configure the integration of Image Relay into Microsoft Entra ID, you need to add Image Relay from the gallery to your list of managed SaaS apps.
- Sign in to the Microsoft Entra admin center as at least a Cloud Application Administrator.
- Browse to Entra ID > Enterprise apps > New application.
- In the Add from the gallery section, type Image Relay in the search box.
- Select Image Relay from results panel and then add the app. Wait a few seconds while the app is added to your tenant.
Alternatively, you can also use the Enterprise App Configuration Wizard. In this wizard, you can add an application to your tenant, add users/groups to the app, assign roles, and walk through the SSO configuration as well. Learn more about Microsoft 365 wizards.
Configure and test Microsoft Entra SSO for Image Relay
Configure and test Microsoft Entra SSO with Image Relay using a test user called B.Simon. For SSO to work, you need to establish a link relationship between a Microsoft Entra user and the related user in Image Relay.
To configure and test Microsoft Entra SSO with Image Relay, perform the following steps:
- Configure Microsoft Entra SSO - to enable your users to use this feature.
- Create a Microsoft Entra test user - to test Microsoft Entra single sign-on with B.Simon.
- Assign the Microsoft Entra test user - to enable B.Simon to use Microsoft Entra single sign-on.
- Configure Image Relay SSO - to configure the single sign-on settings on application side.
- Create Image Relay test user - to have a counterpart of B.Simon in Image Relay that's linked to the Microsoft Entra representation of user.
- Test SSO - to verify whether the configuration works.
Configure Microsoft Entra SSO
Follow these steps to enable Microsoft Entra SSO.
Sign in to the Microsoft Entra admin center as at least a Cloud Application Administrator.
Browse to Entra ID > Enterprise apps > Image Relay > Single sign-on.
On the Select a single sign-on method page, select SAML.
On the Set up single sign-on with SAML page, select the pencil icon for Basic SAML Configuration to edit the settings.
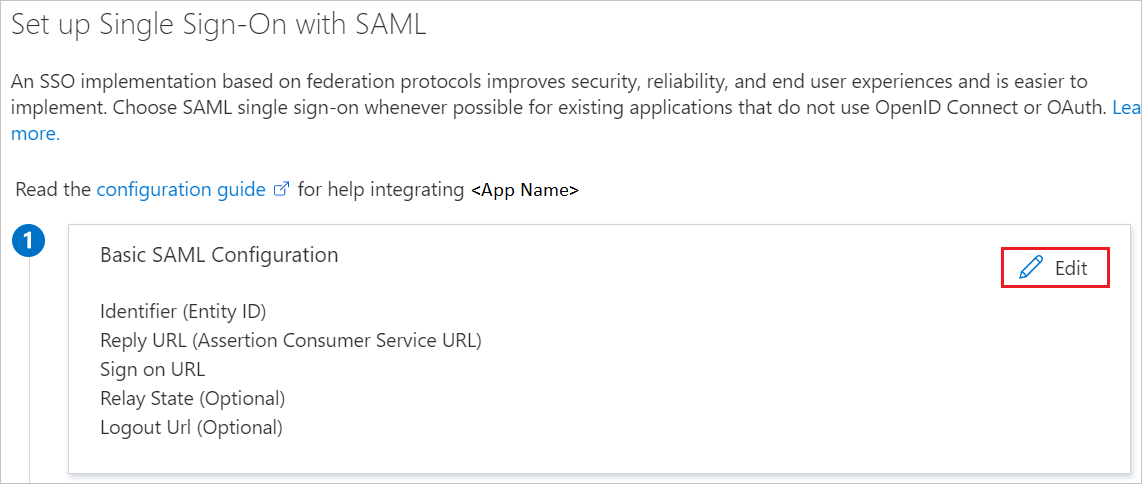
On the Basic SAML Configuration section, perform the following steps:
a. In the Identifier (Entity ID) text box, type a URL using the following pattern:
https://<COMPANYNAME>.imagerelay.com/sso/metadatab. In the Sign on URL text box, type a URL using the following pattern:
https://<COMPANYNAME>.imagerelay.com/Note
These values aren't real. Update these values with the actual Identifier and Sign on URL. Contact Image Relay Client support team to get these values. You can also refer to the patterns shown in the Basic SAML Configuration section.
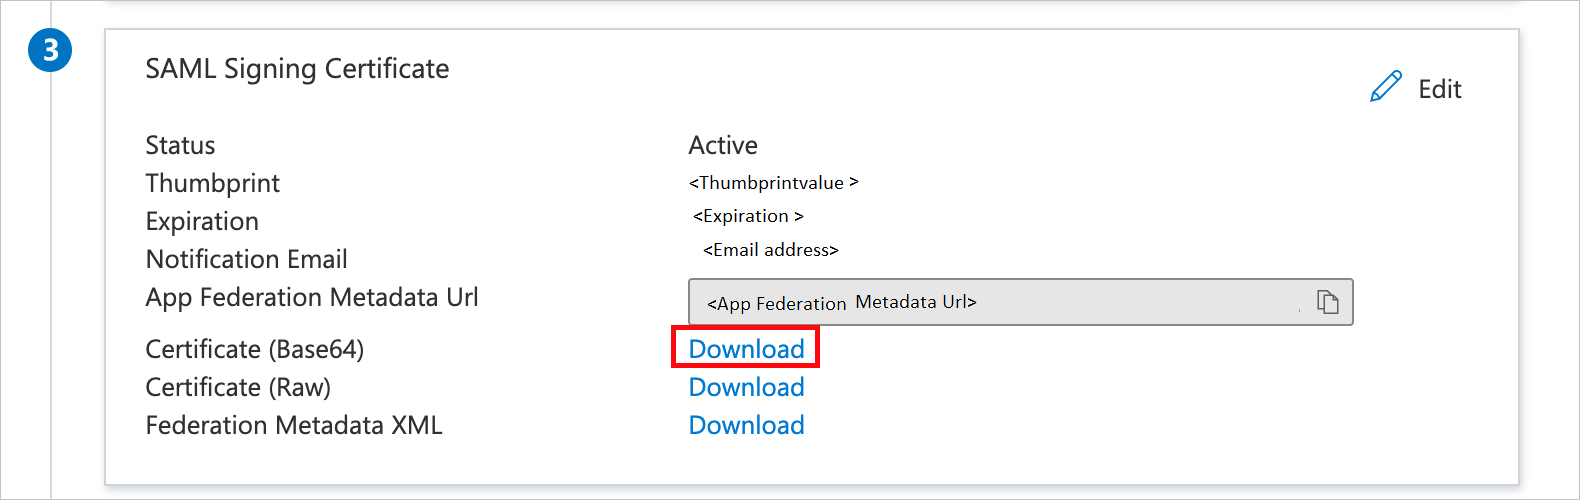
On the Set up Single Sign-On with SAML page, in the SAML Signing Certificate section, select Download to download the Certificate (Base64) from the given options as per your requirement and save it on your computer.
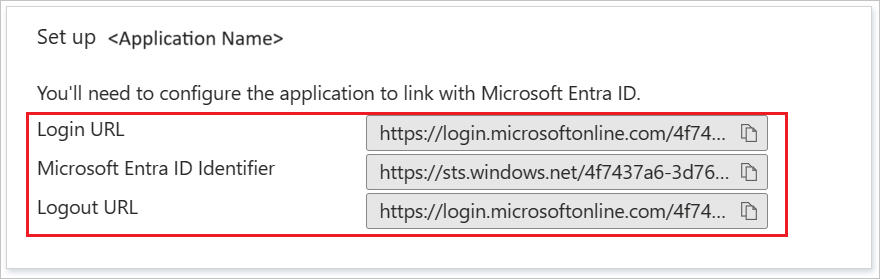
On the Set up Image Relay section, copy the appropriate URL(s) as per your requirement.
Create and assign Microsoft Entra test user
Follow the guidelines in the create and assign a user account quickstart to create a test user account called B.Simon.
Configure Image Relay SSO
In another browser window, sign in to your Image Relay company site as an administrator.
In the toolbar on the top, select the Users & Permissions workload.

Select Create New Permission.
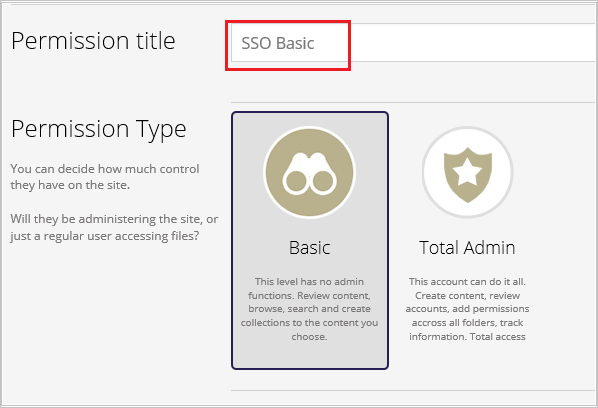
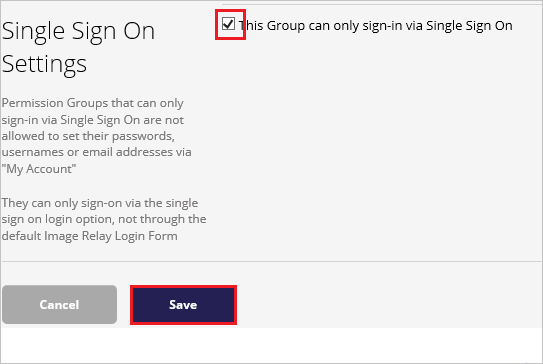
In the Single Sign On Settings workload, select the This Group can only sign-in via Single Sign On check box, and then select Save.
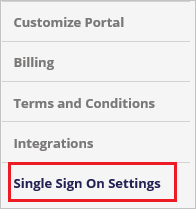
Go to Account Settings.

Go to the Single Sign On Settings workload.
On the SAML Settings dialog, perform the following steps:
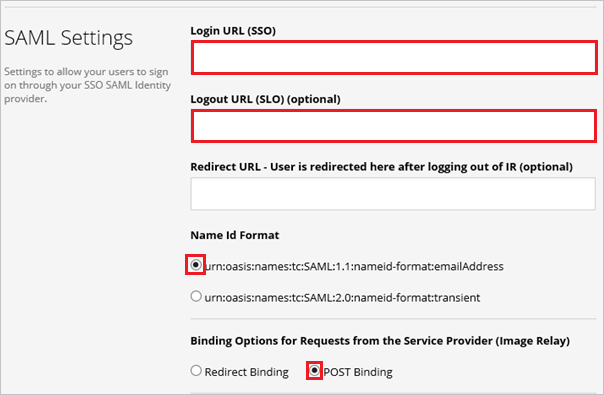
a. In Login URL textbox, paste the value of Login URL..
b. In Logout URL textbox, paste the value of Logout URL..
c. As Name Id Format, select urn:oasis:names:tc:SAML:1.1:nameid-format:emailAddress.
d. As Binding Options for Requests from the Service Provider (Image Relay), select POST Binding.
e. Under x.509 Certificate, select Update Certificate.
f. Open the downloaded certificate in notepad, copy the content, and then paste it into the x.509 Certificate textbox.
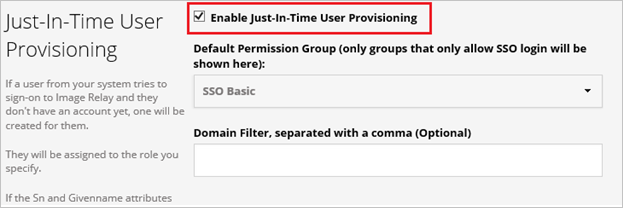
g. In Just-In-Time User Provisioning section, select the Enable Just-In-Time User Provisioning.
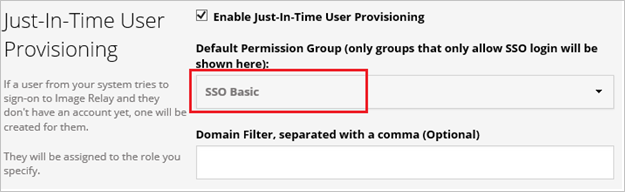
h. Select the permission group (for example, SSO Basic) which is allowed to sign in only through single sign-on.
i. Select Save.
Create Image Relay test user
The objective of this section is to create a user called Britta Simon in Image Relay.
To create a user called Britta Simon in Image Relay, perform the following steps:
Sign-on to your Image Relay company site as an administrator.
Go to Users & Permissions and select Create SSO User.
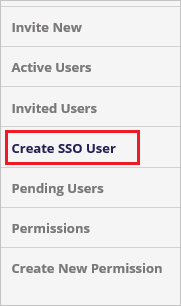
Enter the Email, First Name, Last Name, and Company of the user you want to provision and select the permission group (for example, SSO Basic) which is the group that can sign in only through single sign-on.
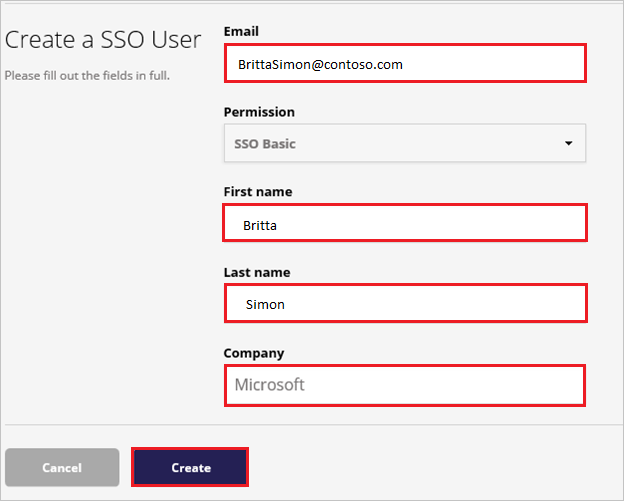
Select Create.
Test SSO
In this section, you test your Microsoft Entra single sign-on configuration with following options.
Select Test this application, this option redirects to Image Relay Sign-on URL where you can initiate the login flow.
Go to Image Relay Sign-on URL directly and initiate the login flow from there.
You can use Microsoft My Apps. When you select the Image Relay tile in the My Apps, this option redirects to Image Relay Sign-on URL. For more information about the My Apps, see Introduction to the My Apps.
Related content
Once you configure Image Relay you can enforce session control, which protects exfiltration and infiltration of your organization’s sensitive data in real time. Session control extends from Conditional Access. Learn how to enforce session control with Microsoft Defender for Cloud Apps.