Note
Access to this page requires authorization. You can try signing in or changing directories.
Access to this page requires authorization. You can try changing directories.
Features
- Agentic Autofix now in public preview
- Batch dismiss security alerts through the REST API
- CodeQL changes for macOS 27, Xcode 27, and Swift 6.4
- Security overview metrics are generally available
- Pipeline access requirements for Advanced Security API calls
Agentic Autofix now in public preview
Agentic Autofix for GitHub Advanced Security for Azure DevOps is now in public preview, supporting both dependency scanning vulnerabilities and code scanning alerts. After enablement, select Generate fix on an alert. The Copilot coding agent uses your repository context to draft a fix in a pull request, making it easy to review and validate changes before merging.
For more information, see Copilot Autofix for code security alerts.
Batch dismiss security alerts through the REST API
You can now dismiss up to 100 GitHub Advanced Security for Azure DevOps alerts in a single REST API request, reducing the number of calls needed to automate alert triage. Each request targets one repository and alert type, with a dismissal reason and optional comment for each alert.
For request details, see the Alerts Batch - Update API documentation.
Security overview metrics are generally available
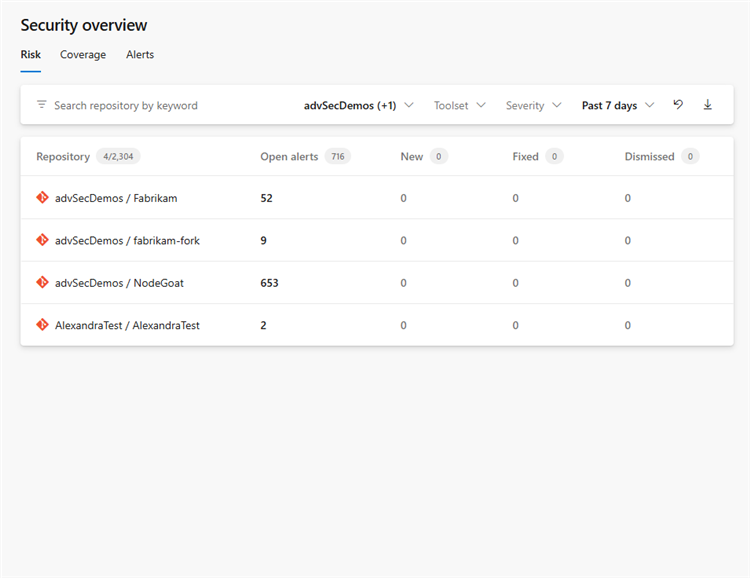
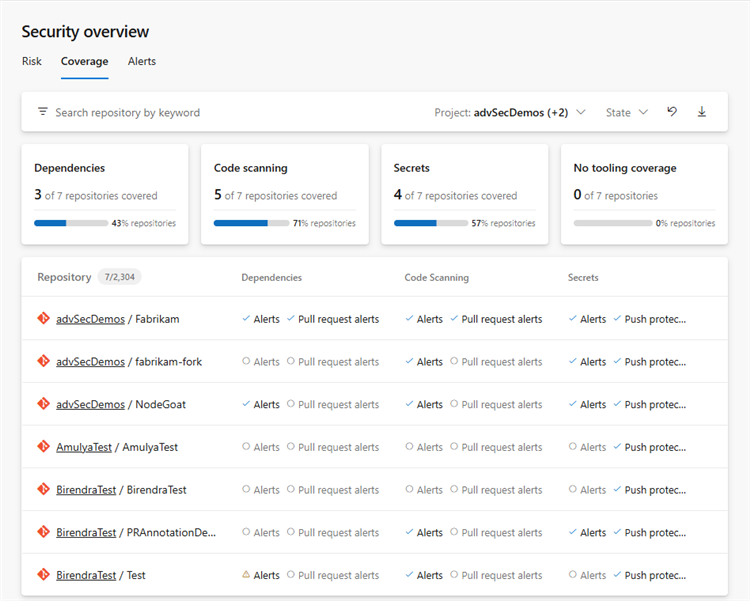
The security overview risk and coverage pages now show organization-wide rollup metrics for alert exposure and scanning coverage. Apply filters to narrow the results and understand your security posture.
Risk:
Coverage:
Pipeline access requirements for Advanced Security API calls
Azure Pipelines that query Advanced Security data might return permission errors or incomplete results if the job doesn't reference every repository it queries. In YAML, reference each required repository in the job with a checkout step or, for script-only use, a uses.repositories entry.
To reference a repository by using checkout:
jobs:
- job: SecurityScan
  steps:
  - checkout: self
  - checkout: git://FabrikamProject/FabrikamTools
  - script: echo "Run your Advanced Security API call here"
Or, to reference it without checking it out:
resources:
  repositories:
  - repository: FabrikamTools
    type: git
    name: FabrikamProject/FabrikamTools

jobs:
- job: SecurityScan
  uses:
    repositories:
    - FabrikamTools
  steps:
  - script: echo "Run your Advanced Security API call here"
For more information about repository access, see Protect access to repositories in YAML pipelines.
CodeQL changes for macOS 27, Xcode 27, and Swift 6.4
CodeQL cannot perform traced extraction with Xcode 27 for C/C++, C#, Go, Java, Kotlin, or Swift; traced extraction may also be unavailable on macOS 27. Swift 6.4 is unsupported on all platforms. To keep scans running, pin workflows to macOS 26 or earlier and Xcode 26 or earlier. For C/C++, C#, and Java, none build mode avoids build tracing. Support for Intel-based Macs is scheduled for deprecation in mid-December 2026.
Read the CodeQL compatibility announcement.
Next steps
Note
These features will roll out over the next two to three weeks.
Head over to Azure DevOps and take a look.
How to provide feedback
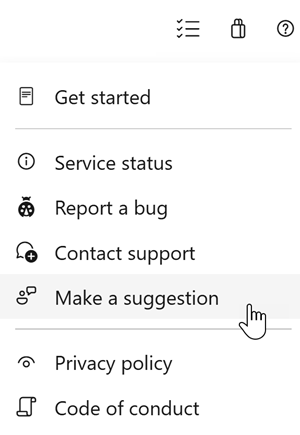
We would love to hear what you think about these features. Use the help menu to report a problem or provide a suggestion.
You can also get advice and your questions answered by the community on Stack Overflow.