Note
Access to this page requires authorization. You can try signing in or changing directories.
Access to this page requires authorization. You can try changing directories.
In this article, you learn how to integrate Samsung Knox and Business Services with Microsoft Entra ID. When you integrate Samsung Knox and Business Services with Microsoft Entra ID, you can:
- Control in Microsoft Entra ID who has access to Samsung Knox and Business Services.
- Enable your users to be automatically signed-in to Samsung Knox and Business Services with their Microsoft Entra accounts.
- Manage your accounts in one central location.
Prerequisites
The scenario outlined in this article assumes that you already have the following prerequisites:
- A Microsoft Entra user account with an active subscription. If you don't already have one, you can Create an account for free.
- One of the following roles:
- A Samsung Knox account.
Scenario description
In this article, you configure and test Microsoft Entra SSO in a test environment.
- Samsung Knox and Business Services support only SP initiated SSO.
Note
Identifier of this application is a fixed string value so only one instance can be configured in one tenant.
Adding Samsung Knox and Business Services from the gallery
To configure the integration of Samsung Knox and Business Services into Microsoft Entra ID, you need to add Samsung Knox and Business Services from the gallery to your list of managed SaaS apps.
- Sign in to the Microsoft Entra admin center as at least a Cloud Application Administrator.
- Browse to Entra ID > Enterprise apps > New application.
- In the Add from the gallery section, type Samsung Knox and Business Services in the search box.
- Select Samsung Knox and Business Services from results panel and then add the app. Wait a few seconds while the app is added to your tenant.
Alternatively, you can also use the Enterprise App Configuration Wizard. In this wizard, you can add an application to your tenant, add users/groups to the app, assign roles, and walk through the SSO configuration as well. Learn more about Microsoft 365 wizards.
Configure and test Microsoft Entra SSO for Samsung Knox and Business Services
Configure and test Microsoft Entra SSO with Samsung Knox and Business Services using a test user called B.Simon. For SSO to work, you need to establish a link relationship between a Microsoft Entra user and the related user in SamsungKnox.com.
To configure and test Microsoft Entra SSO with Samsung Knox and Business Services, perform the following steps:
- Configure Microsoft Entra SSO - to enable your users to use this feature.
- Create a Microsoft Entra test user - to test Microsoft Entra single sign-on with B.Simon.
- Assign the Microsoft Entra test user - to enable B.Simon to use Microsoft Entra single sign-on.
- Configure Samsung Knox and Business Services SSO - to configure the single sign-on settings on application side.
- Create Samsung Knox and Business Services test user - to have a counterpart of B.Simon in Samsung Knox and Business Services that's linked to the Microsoft Entra representation of user.
- Test SSO - to verify whether the configuration works.
Configure Microsoft Entra SSO
Follow these steps to enable Microsoft Entra SSO.
Sign in to the Microsoft Entra admin center as at least a Cloud Application Administrator.
Browse to Entra ID > Enterprise apps > Samsung Knox and Business Services > Single sign-on.
On the Select a single sign-on method page, select SAML.
On the Set up single sign-on with SAML page, select the pencil icon for Basic SAML Configuration to edit the settings.
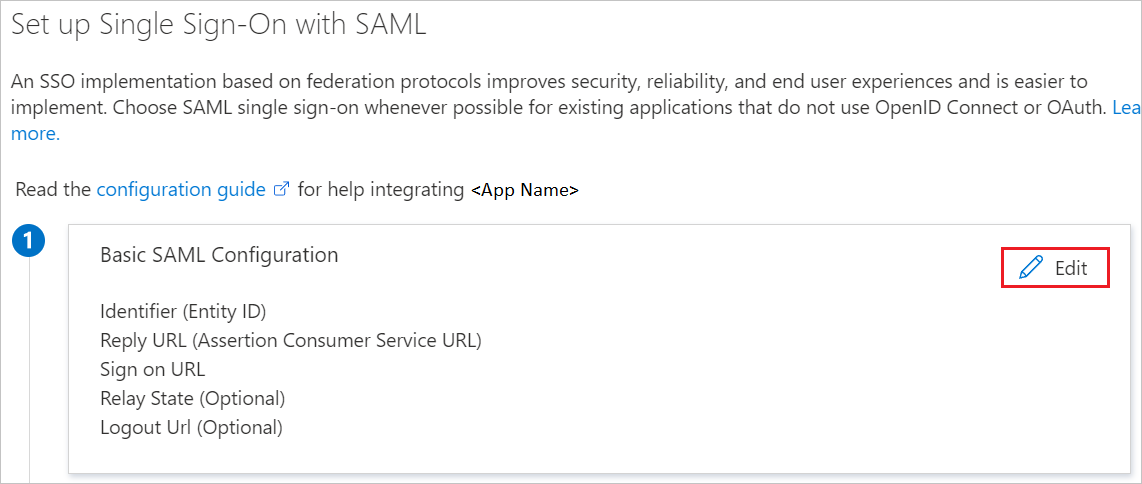
On the Basic SAML Configuration section, enter the values for the following fields:
a. In the Identifier (Entity ID) text box, type the URL:
https://www.samsungknox.com/b. In the Reply URL text box, type the URL:
https://central.samsungknox.com/ams/ad/saml/acsc. In the Sign on URL text box, type the URL:
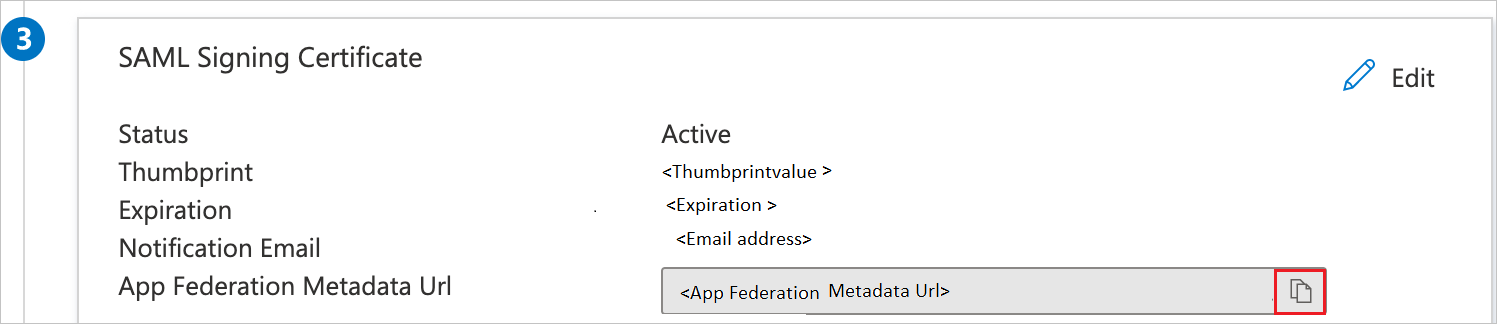
https://account.samsung.com/On the Set up single sign-on with SAML page, In the SAML Signing Certificate section, select copy button to copy App Federation Metadata Url and save it on your computer.
Create and assign Microsoft Entra test user
Follow the guidelines in the create and assign a user account quickstart to create a test user account called B.Simon.
Configure Samsung Knox and Business Services SSO
In a different web browser window, sign in to SamsungKnox.com as an administrator.
Select the Avatar on the top right corner.

Go to My account > SSO SETTINGS and perform the following steps.

a. In the Identifier (entity ID) text box, paste the Identifier URL which you have copied from the Microsoft Entra admin center.
b. Copy Reply URL (assertion consumer service URL) value, paste this value into the Reply URL text box in the Basic SAML Configuration section in Microsoft Entra admin center.
c. In the App federation metadata URL text box, paste the App federation metadata URL which you have copied From the Microsoft Entra admin center.
d. Select CONNECT TO SSO.
Create Samsung Knox and Business Services test user
In this section, you create a user called Britta Simon in Samsung Knox and Business Services. Refer to the Knox Configure or Knox Mobile Enrollment admin guides for instructions on how to invite a subadministrator, or test user, to your Samsung Knox organization. Users must be created and activated before you use single sign-on.
Test SSO
In this section, you test your Microsoft Entra single sign-on configuration with following options.
Select Test this application, this option redirects to SamsungKnox.com, where you can initiate the login flow.
Go to SamsungKnox.com directly and initiate the login flow from there.
You can use Microsoft My Apps. When you select the Samsung Knox and Business Services tile in the My Apps, this option redirects to SamsungKnox.com. For more information about the My Apps, see Introduction to the My Apps.
Related content
Once you configure Samsung Knox and Business Services you can enforce session control, which protects exfiltration and infiltration of your organization’s sensitive data in real time. Session control extends from Conditional Access. Learn how to enforce session control with Microsoft Defender for Cloud Apps.