Notitie
Voor toegang tot deze pagina is autorisatie vereist. U kunt proberen u aan te melden of de directory te wijzigen.
Voor toegang tot deze pagina is autorisatie vereist. U kunt proberen de mappen te wijzigen.
Microsoft Beveiliging DevOps is een commandoregelapplicatie die statische analysetools integreert in de ontwikkelingslevenscyclus. Security DevOps installeert, configureert en voert de nieuwste versies van statische analysehulpprogramma's zoals SDL, beveiliging en nalevingshulpprogramma's uit. Security DevOps is gegevensgestuurd met draagbare configuraties die deterministische uitvoering in meerdere omgevingen mogelijk maken.
Microsoft Beveiliging DevOps maakt gebruik van de volgende opensource-hulpprogramma's:
| Name | Taal | License |
|---|---|---|
| AntiMalware | Antimalwarebeveiliging in Windows van Microsoft Defender voor Eindpunt die scant op malware en de build onderbreekt als er malware wordt gevonden. Dit hulpprogramma scant standaard op windows-nieuwste agent. | Niet open source |
| Bandit | Python | Apache Licentie 2.0 |
| BinSkim | Binaire--Windows, ELF | MIT-licentie |
| Checkov | Terraform, Terraform plan, CloudFormation, Amazon Web Services (AWS) SAM, Kubernetes, Helm charts, Kustomize, Dockerfile, Serverless, Bicep, OpenAPI, ARM | Apache Licentie 2.0 |
| ESlint | JavaScript | MIT-licentie |
| Sjabloonanalyse | ARM-sjabloon, Bicep | MIT-licentie |
| Terrascan | Terraform (HCL2), Kubernetes (JSON/YAML), Helm v3, Kustomize, Dockerfiles, CloudFormation | Apache Licentie 2.0 |
| Trivy | containerafbeeldingen, Infrastructure as Code (IaC) | Apache Licentie 2.0 |
Prerequisites
Voordat je de Microsoft Beveiliging DevOps GitHub-actie configureert, zorg ervoor dat je aan de volgende voorwaarden voldoet:
Een Azure-abonnement. Als u geen Azure-abonnement hebt, maakt u een gratis Azure-account voordat u begint.
Open de GitHub-actie Microsoft Beveiliging DevOps in een nieuw venster.
Zorg ervoor dat werkstroommachtigingen zijn ingesteld op Lezen en Schrijven in de GitHub-opslagplaats. Deze stap omvat het instellen van de
ID-token: writetoestemming in de GitHub-workflow voor federatie met Microsoft Defender voor Cloud.
Stel de GitHub Actions-workflow in
De actie GitHub instellen:
Meld u aan bij GitHub.
Selecteer een opslagplaats waarnaar u de GitHub-actie wilt configureren.
Selecteer Acties.
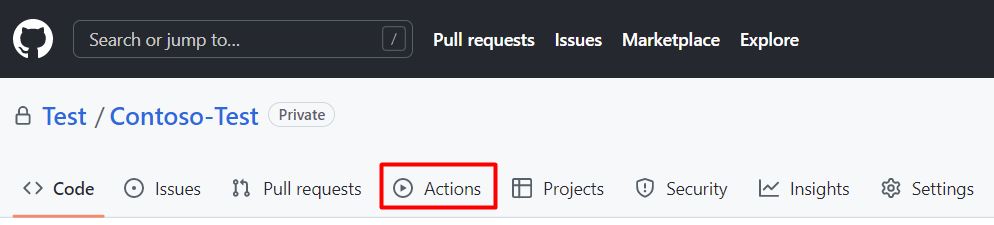
Selecteer Nieuwe werkstroom.
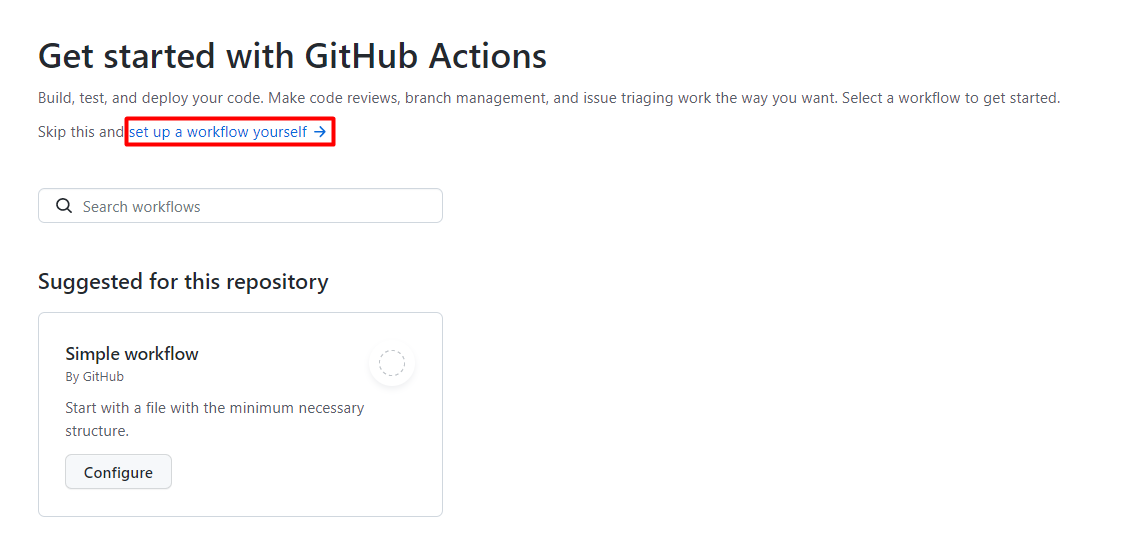
Op 'Begin met GitHub Actions kies je 'Zelf een workflow opzetten'.
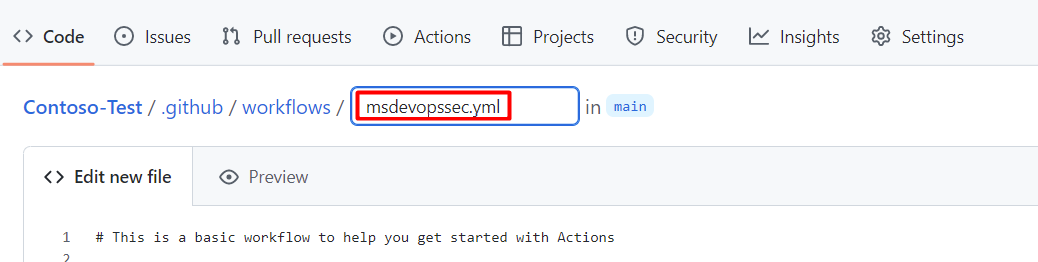
Voer een naam in voor je workflowbestand. Bijvoorbeeld, msdevopssec.yml.
Kopieer en plak de volgende voorbeeldactieworkflow in het tabblad Nieuw bestand bewerken .
name: MSDO
on:
  push:
    branches:
      - main

jobs:
  sample:
    name: Microsoft Security DevOps

    # Windows and Linux agents are supported
    runs-on: windows-latest

    permissions:
      contents: read
      id-token: write
      actions: read
      # Write access for security-events is only required for customers looking for MSDO results to appear in the codeQL security alerts tab on GitHub (Requires GHAS)
      security-events: write

    steps:

      # Checkout your code repository to scan
    - uses: actions/checkout@v3

      # Run analyzers
    - name: Run Microsoft Security DevOps
      uses: microsoft/security-devops-action@latest
      id: msdo
    # with:
      # config: string. Optional. A file path to an MSDO configuration file ('*.gdnconfig').
      # policy: 'GitHub' | 'microsoft' | 'none'. Optional. The name of a well-known Microsoft policy. If no configuration file or list of tools is provided, the policy may instruct MSDO which tools to run. Default: GitHub.
      # categories: string. Optional. A comma-separated list of analyzer categories to run. Values: 'code', 'artifacts', 'IaC', 'containers'. Example: 'IaC, containers'. Defaults to all.
      # languages: string. Optional. A comma-separated list of languages to analyze. Example: 'javascript,typescript'. Defaults to all.
      # tools: string. Optional. A comma-separated list of analyzer tools to run. Values: 'bandit', 'binskim', 'checkov', 'eslint', 'templateanalyzer', 'terrascan', 'trivy'.

      # Upload alerts to the Security tab - required for MSDO results to appear in the codeQL security alerts tab on GitHub (Requires GHAS)
    # - name: Upload alerts to Security tab
    #  uses: github/codeql-action/upload-sarif@v3
    #  with:
    #    sarif_file: ${{ steps.msdo.outputs.sarifFile }}

      # Upload alerts file as a workflow artifact - required for MSDO results to appear in the codeQL security alerts tab on GitHub (Requires GHAS)
    # - name: Upload alerts file as a workflow artifact
    #  uses: actions/upload-artifact@v3
    #  with:
    #    name: alerts
    #    path: ${{ steps.msdo.outputs.sarifFile }}
Note
Voor meer configuratieopties en instructies voor tools, zie de Microsoft Beveiliging DevOps wiki.
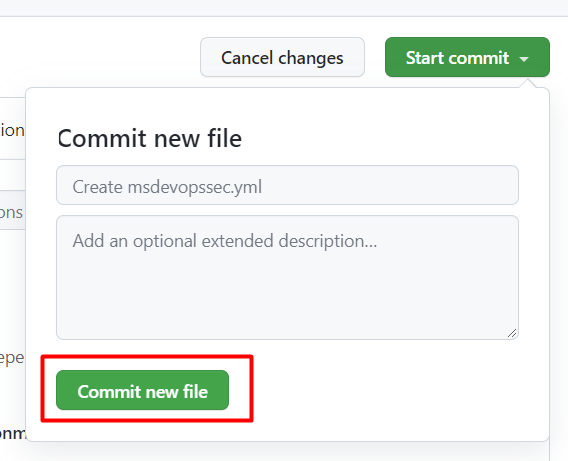
Selecteer Doorvoeren starten.
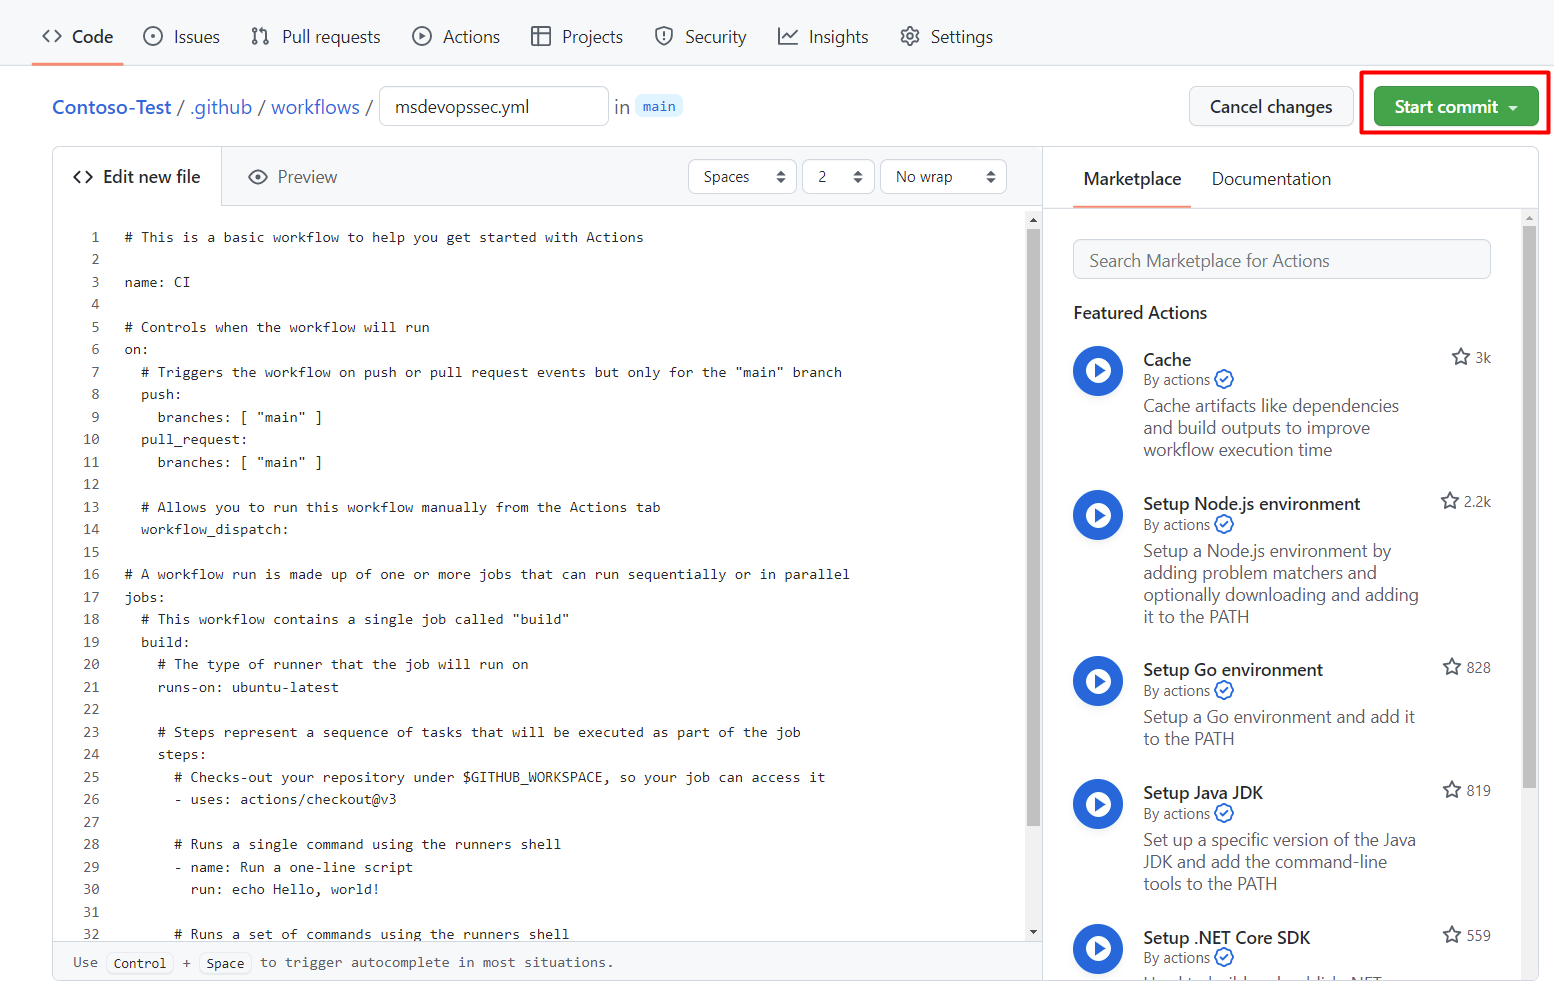
Selecteer Nieuw bestand doorvoeren. Het proces kan tot één minuut duren om te voltooien.
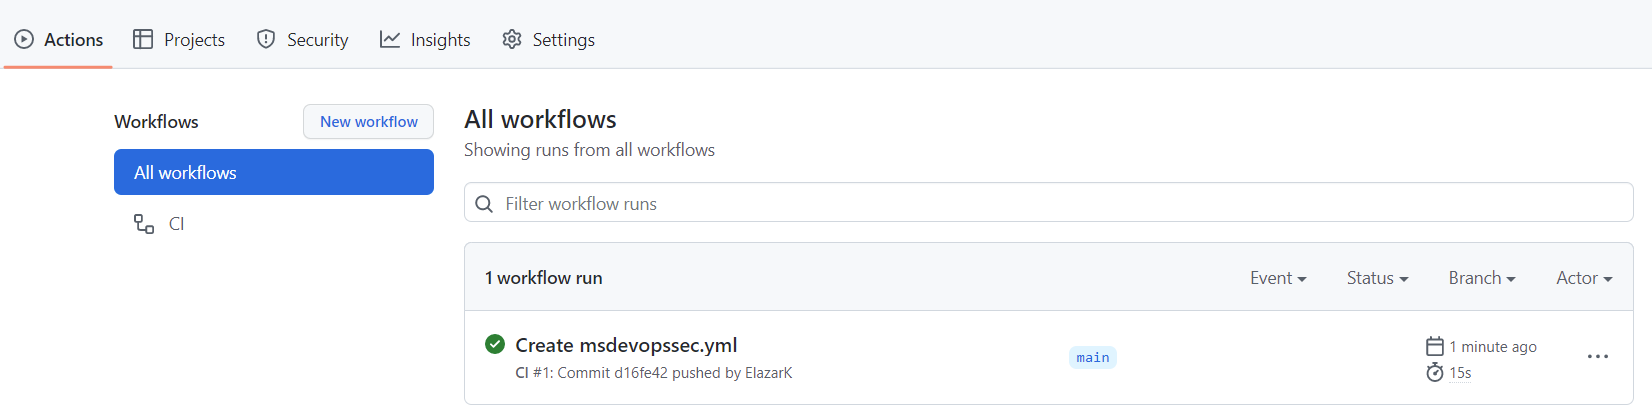
Selecteer Acties en controleer of de nieuwe actie wordt uitgevoerd.


Scanresultaten weergeven
Uw scanresultaten weergeven:
Meld u aan bij Azure.
Ga naar Defender voor Cloud>DevOps Security.
Vanuit het DevOps-beveiligingspaneel kun je dezelfde Microsoft Beveiliging DevOps (MSDO) beveiligingsresultaten zien. Ontwikkelaars zien deze resultaten in hun CI-logs voor de bijbehorende repository binnen enkele minuten. Klanten met GitHub Geavanceerde beveiliging zien ook de resultaten die zijn opgenomen in deze hulpprogramma's.
Verwante onderwerpen
- GitHub-acties voor Azure
- Deploy apps van GitHub naar Azure
- DevOps-beveiliging in Defender voor Cloud