概述
<basicAuthentication> 元素包含 Internet Information Services (IIS) 7 基本身份验证模块的配置设置。 配置此元素以启用或禁用基本身份验证、标识领域和默认登录域,并确定模块使用的登录方法。
基本身份验证方案是收集用户名和密码信息时广泛使用的行业标准方法。 基本身份验证以未加密的形式跨网络传输用户名和密码。 可以将 SSL 加密与基本身份验证结合使用,以帮助保护通过 Internet 或公司网络传输的用户帐户信息。
兼容性
| 版本 | 说明 |
|---|---|
| IIS 10.0 | <basicAuthentication> 元素在 IIS 10.0 中未进行修改。 |
| IIS 8.5 | <basicAuthentication> 元素在 IIS 8.5 中未进行修改。 |
| IIS 8.0 | <basicAuthentication> 元素在 IIS 8.0 中未进行修改。 |
| IIS 7.5 | <basicAuthentication> 元素未在 IIS 7.5 中进行修改。 |
| IIS 7.0 | <basicAuthentication> 元素是在 IIS 7.0 中引入的。 |
| IIS 6.0 | <basicAuthentication> 元素取代了 IIS 6.0 的 AuthType 和 AuthFlags 元数据库属性。 |
安装
IIS 7 及更高版本的默认安装不包括基本身份验证角色服务。 要在 Internet Information Services (IIS) 上使用基本身份验证,必须安装角色服务,为网站或应用程序禁用匿名身份验证,然后为网站或应用程序启用基本身份验证。
要安装基本身份验证角色服务,请执行以下步骤。
Windows Server 2012 或 Windows Server 2012 R2
- 在任务栏上,单击 “服务器管理器”。
- 在“服务器管理器”中,单击“管理”菜单,然后单击“添加角色和功能”。
- 在“添加角色和功能”向导中,单击“下一步”。 选择安装类型,然后单击“下一步”。 选择目标服务器,然后单击“下一步”。
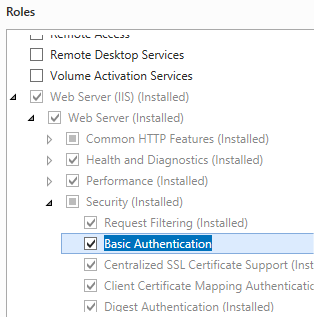
- 在“服务器角色”页上,依次展开“Web 服务器 (IIS)”、“Web 服务器”和“安全性”,然后选择“基本身份验证”。 单击 “下一步” 。
 .
- 在“选择功能”页上,单击“下一步”。
- 在“确认安装选择”页上,单击“安装”。
- 在“结果” 页面中单击“关闭” 。
Windows 8 或 Windows 8.1
- 在“开始”屏幕上,将指针一直移动到左下角,右键单击“开始”按钮,然后单击“控制面板”。
- 在“控制面板”中,单击“程序与功能”,然后单击“打开或关闭 Windows 功能”。
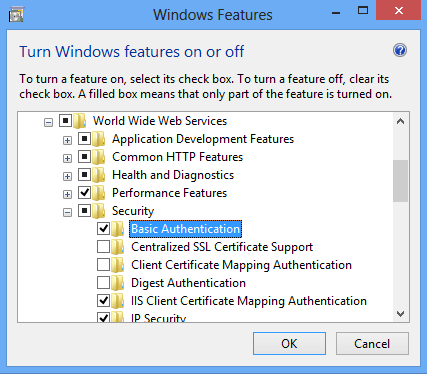
- 依次展开“Internet 信息服务”、“万维网服务”和“安全性”,然后选择“基本身份验证”。
- 单击“确定”。
- 单击“关闭” 。
Windows Server 2008 或 Windows Server 2008 R2
- 在任务栏上,单击“开始”,指向“管理工具”,然后单击“服务器管理器”。
- 在“服务器管理器”层次结构窗格中,展开“角色”,然后单击“Web 服务器(IIS)”。
- 在“Web 服务器(IIS)”窗格中,滚动到“角色服务”部分,然后单击“添加角色服务”。
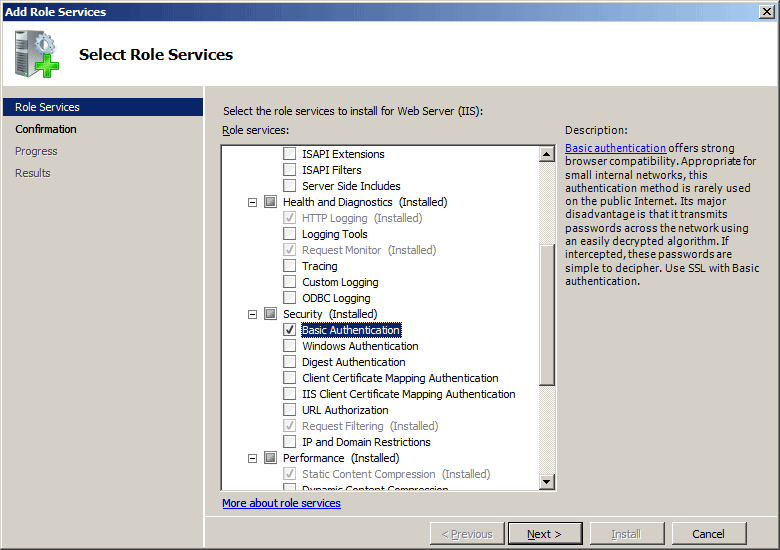
- 在“添加角色服务向导”的“选择角色服务”页上,选择“基本身份验证”,然后单击“下一步”。
- 在“确认安装选择”页中,单击“安装”。
- 在“结果” 页面中单击“关闭” 。
Windows Vista 或 Windows 7
- 在任务栏上,单击“开始”,然后单击“控制面板”。
- 在“控制面板”中,单击“程序与功能”,然后单击“打开或关闭 Windows 功能”。
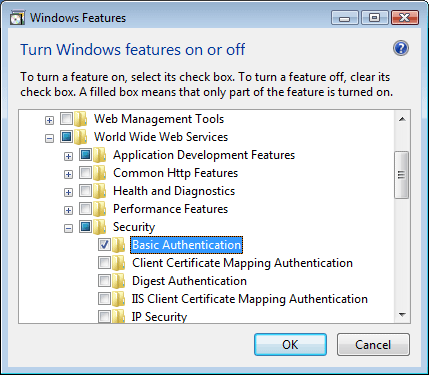
- 依次展开“Internet 信息服务”、“万维网服务”和“安全性”,选择“基本身份验证”,然后单击“确定”。
操作方式
如何启用基本身份验证和禁用匿名身份验证
打开 Internet Information Services (IIS) 管理器:
如果使用的是 Windows Server 2012 或 Windows Server 2012 R2:
- 在任务栏上,单击“服务器管理器”,单击“工具”,然后单击“Internet Information Services (IIS)管理器”。
如果使用的是 Windows 8 或 Windows 8.1:
- 按住 Windows 键,按字母 X,然后单击“控制面板”。
- 单击“管理工具”,然后双击“Internet 信息服务(IIS)管理器”。
如果使用的是 Windows Server 2008 或 Windows Server 2008 R2:
- 在任务栏上,单击“开始”,指向“管理工具”,然后单击“Internet Information Services (IIS)管理器”。
如果使用的是 Windows Vista 或 Windows 7:
- 在任务栏上,单击“开始”,然后单击“控制面板”。
- 双击“管理工具”,然后双击“Internet 信息服务(IIS)管理器”。
在“连接”窗格中,展开服务器名称,展开“站点”,然后单击要为其启用基本身份验证的站点、应用程序或 Web 服务。
滚动到“主页”窗格中的“安全性”部分,然后双击“身份验证”。
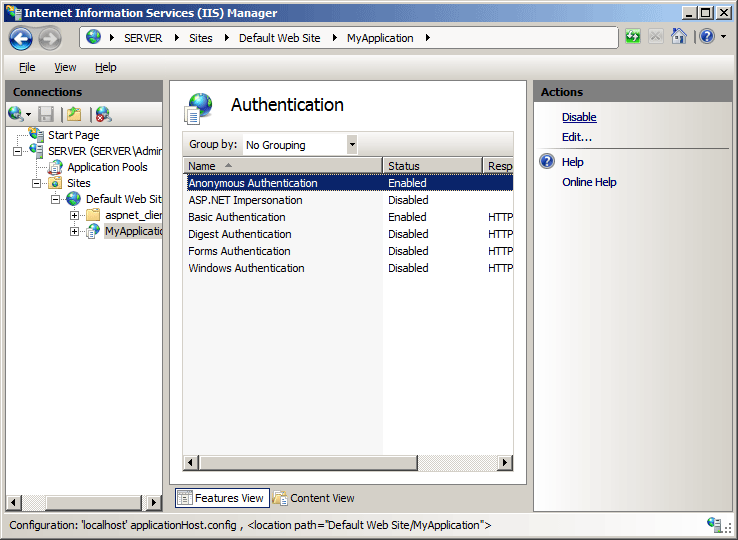
在“身份验证”窗格中,选择“基本身份验证”,然后在“操作”窗格中单击“启用”。
在“身份验证”窗格中,选择“匿名身份验证”,然后在“操作”窗格中单击“禁用”。
配置
可在站点、应用程序、虚拟目录和 URL 级别配置 <basicAuthentication> 元素。 安装角色服务后,IIS 7 会将以下配置设置提交到 ApplicationHost.config 文件。
<basicAuthentication enabled='false' />
特性
| 属性 | 说明 | ||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|
defaultLogonDomain |
可选的 String 属性。 指定基本身份验证的默认登录域。 |
||||||||||
enabled |
可选布尔属性。 指定是否启用基本身份验证。 默认值为 false。 |
||||||||||
logonMethod |
可选的枚举属性。 logonMethod 属性可以是下列可能值之一。 默认为 ClearText。
|
||||||||||
realm |
可选的 String 属性。 指定基本身份验证的领域。 |
子元素
无。
配置示例
以下配置示例为网站、Web 应用程序或 Web 服务启用基本身份验证。 默认情况下,这些设置必须包含在 ApplicationHost.config 文件中,并且必须在 <location> 元素中包含这些设置,还必须使用 path 属性定义要在其中应用身份验证设置的网站或应用程序。
<security>
   <authentication>
      <anonymousAuthentication enabled="false" />
      <basicAuthentication enabled="true" />
   </authentication>
</security>
代码示例
以下示例为站点启用基本身份验证。
AppCmd.exe
appcmd.exe set config "Contoso" -section:system.webServer/security/authentication/basicAuthentication /enabled:"True" /commit:apphost
注意
使用 AppCmd.exe 配置这些设置时,必须确保将 commit 参数设置为 apphost。 这会将配置设置提交到 ApplicationHost.config 文件中的相应位置部分。
C#
using System;
using System.Text;
using Microsoft.Web.Administration;

internal static class Sample
{

    private static void Main()
    {

        using (ServerManager serverManager = new ServerManager())
        {
            Configuration config = serverManager.GetApplicationHostConfiguration();

            ConfigurationSection basicAuthenticationSection = config.GetSection("system.webServer/security/authentication/basicAuthentication", "Contoso");
            basicAuthenticationSection["enabled"] = true;

            serverManager.CommitChanges();
        }
    }
}
VB.NET
Imports System
Imports System.Text
Imports Microsoft.Web.Administration

Module Sample
    Sub Main()
        Dim serverManager As ServerManager = New ServerManager
        Dim config As Configuration = serverManager.GetApplicationHostConfiguration

        Dim basicAuthenticationSection As ConfigurationSection = config.GetSection("system.webServer/security/authentication/basicAuthentication", "Contoso")
        basicAuthenticationSection("enabled") = True

        serverManager.CommitChanges()
    End Sub
End Module
JavaScript
var adminManager = new ActiveXObject('Microsoft.ApplicationHost.WritableAdminManager');
adminManager.CommitPath = "MACHINE/WEBROOT/APPHOST";

var basicAuthenticationSection = adminManager.GetAdminSection("system.webServer/security/authentication/basicAuthentication", "MACHINE/WEBROOT/APPHOST/Contoso");
basicAuthenticationSection.Properties.Item("enabled").Value = true;

adminManager.CommitChanges();
VBScript
Set adminManager = CreateObject("Microsoft.ApplicationHost.WritableAdminManager")
adminManager.CommitPath = "MACHINE/WEBROOT/APPHOST"

Set basicAuthenticationSection = adminManager.GetAdminSection("system.webServer/security/authentication/basicAuthentication", "MACHINE/WEBROOT/APPHOST/Contoso")
basicAuthenticationSection.Properties.Item("enabled").Value = True

adminManager.CommitChanges()